
rea
Reverse engineer anything with agents, from app behavior down to native binaries.
420k
 @morluto
Turns your coding assistant into a security scanner that checks your codebase for vulnerabilities such as business logic flaws, insecure file uploads, GraphQL injection and hardcoded secrets, without any third-party tools. Works with Claude Code, Codex, Cursor and other agent-skill assistants.
Claude Code
$ npx -y skills add utkusen/sast-skills --agent claude-code
Codex
$ npx skills add utkusen/sast-skills -a codex
Cursor
$ npx skills add utkusen/sast-skills -a cursor
Gemini CLI
$ npx skills add utkusen/sast-skills -a gemini-cli
GitHub Copilot
$ npx skills add utkusen/sast-skills -a github-copilot
OpenCode
$ npx skills add utkusen/sast-skills -a opencode
Windsurf
$ npx skills add utkusen/sast-skills -a windsurf
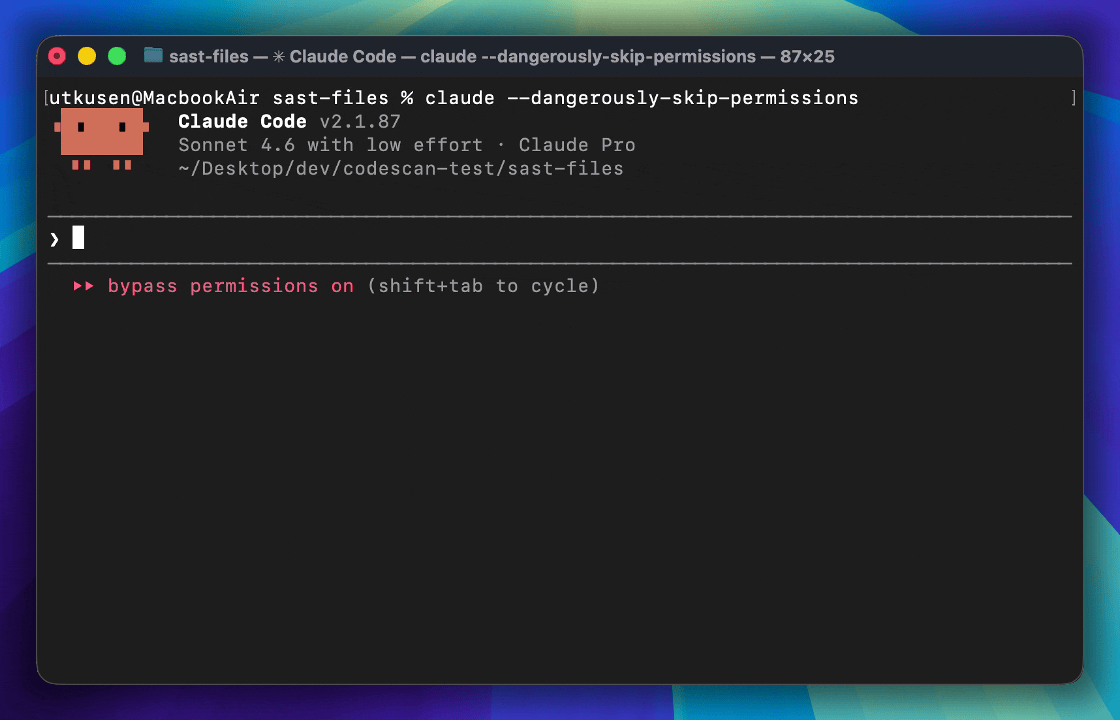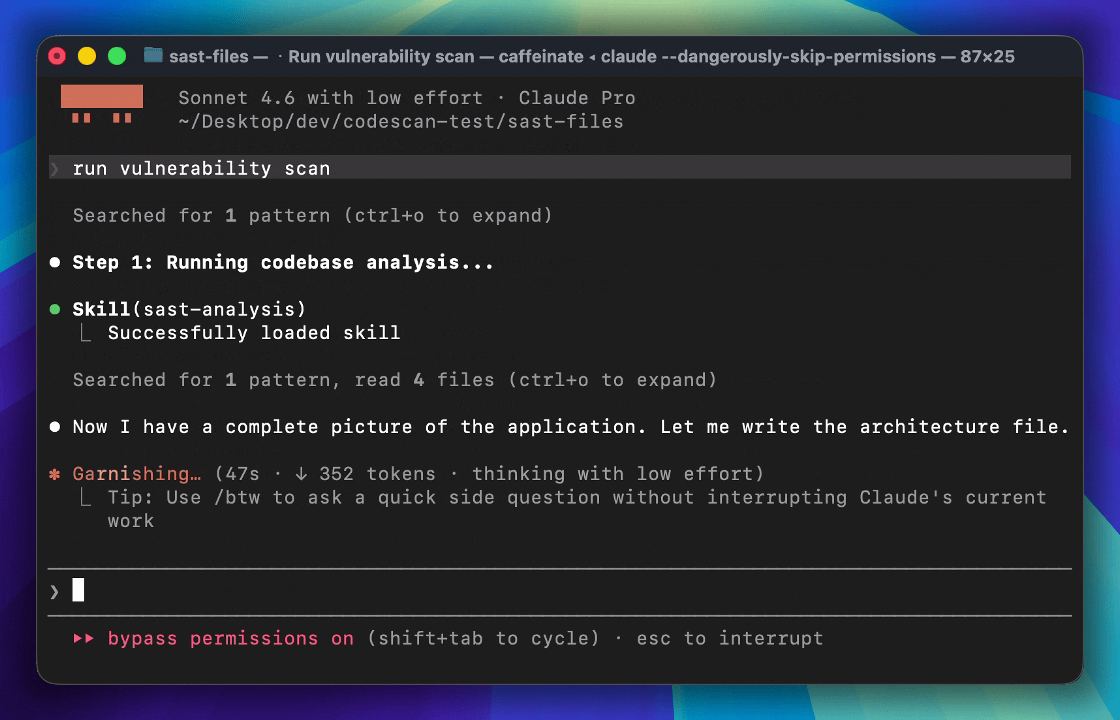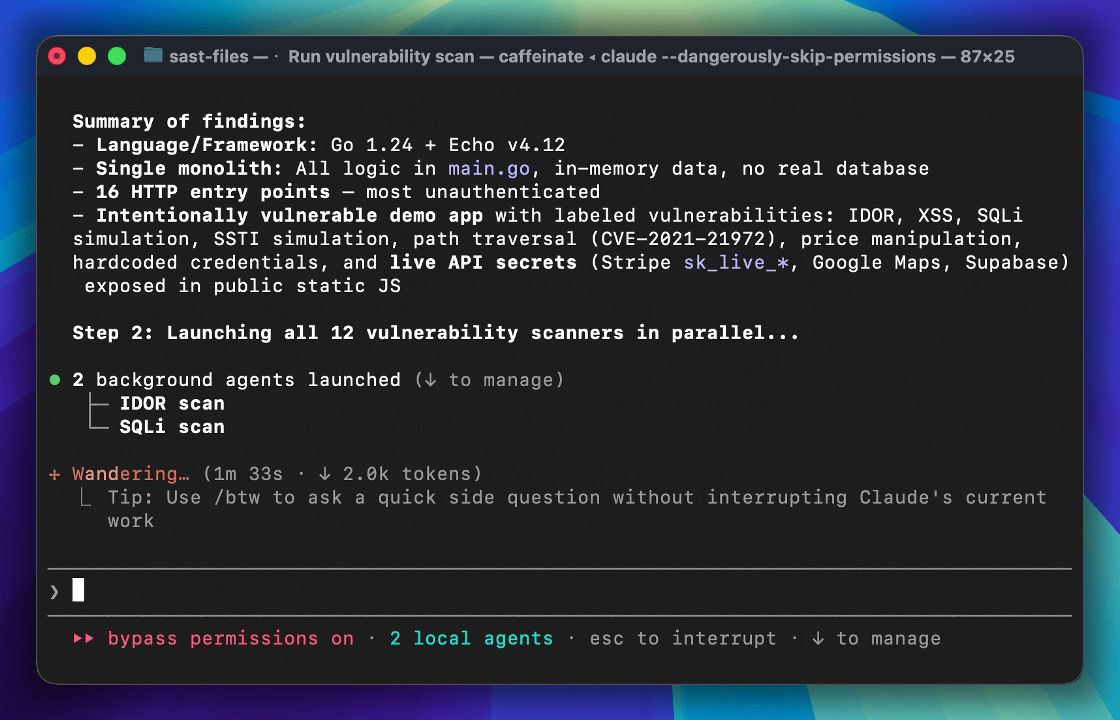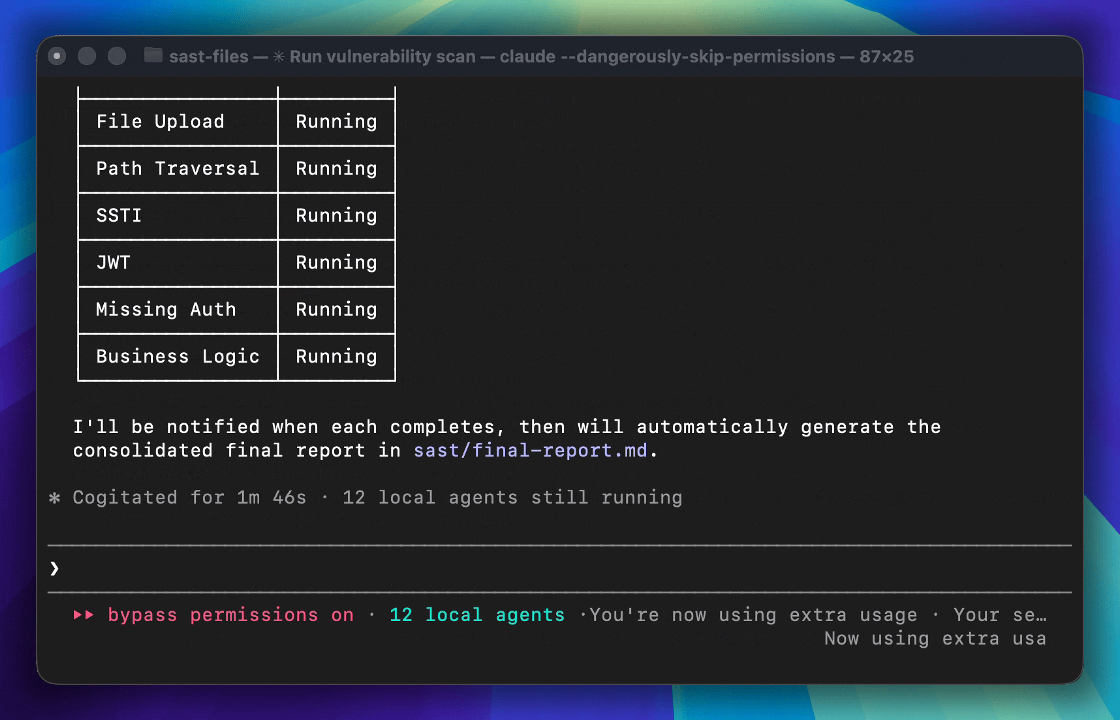
A collection of agent skills that turn your LLM coding assistant into a fully functional SAST scanner to find vulnerabilities in your codebase. Works natively with Claude Code, Codex, Opencode, Cursor and any other assistant that supports agent skills. No third-party tools required.
The main goal of this project is to find as many vulnerabilities as possible at the lowest possible cost.
CLAUDE.md (for Claude Code) or AGENTS.md (for Opencode and other IDEs) orchestrates the entire assessment workflow automatically. The assessment runs in three steps:
Codebase Analysis -- The sast-analysis skill maps the technology stack, architecture, entry points, data flows, and trust boundaries. It writes its findings to sast/architecture.md.
Vulnerability Detection (parallel) -- All 13 vulnerability detection skills run in parallel as subagents. Each skill follows a two-phase approach: first a recon/discovery phase to find candidate sections, then a verification phase to confirm exploitability. Results are written to sast/*-results.md.
Report Generation -- The sast-report skill consolidates all findings into a single sast/final-report.md, ranked by severity with full remediation guidance and dynamic test instructions.
| Skill | Vulnerability Class |
|---|---|
| sast-analysis | Codebase reconnaissance, architecture mapping, threat modeling |
| sast-sqli | SQL Injection |
| sast-graphql | GraphQL injection |
| sast-xss | Cross-Site Scripting (XSS) |
| sast-rce | Remote Code Execution (command injection, eval, unsafe deserialization) |
| sast-ssrf | Server-Side Request Forgery |
| sast-idor | Insecure Direct Object Reference |
| sast-xxe | XML External Entity |
| sast-ssti | Server-Side Template Injection |
| sast-jwt | Insecure JWT implementations |
| sast-missingauth | Missing authentication and broken function-level authorization |
| sast-pathtraversal | Path / directory traversal |
| sast-fileupload | Insecure file upload |
| sast-businesslogic | Business logic flaws (price manipulation, workflow bypass, race conditions, etc.) |
| sast-report | Consolidated final report ranked by severity |
Copy your project into the sast-files folder, then open sast-files as your workspace in your AI coding assistant.
cp -r /path/to/your/project sast-files/
Note: If your project already contains a
CLAUDE.mdorAGENTS.mdfile, remove it before running the assessment — otherwise it will conflict with the orchestration file provided by this toolkit.
After copying the files, open your project in your AI coding assistant and ask:
Run vulnerability scan
or
Find vulnerabilities in this codebase
The entry point file (CLAUDE.md or AGENTS.md) orchestrates the full workflow automatically. It will skip any steps whose output files already exist, so you can safely re-run it after fixing issues.
All output is written to a sast/ folder in your project root:
| File | Description |
|---|---|
sast/architecture.md | Technology stack, architecture, entry points, data flows |
sast/*-results.md | Per-vulnerability-class findings with proof and remediation |
sast/final-report.md | Consolidated report ranked by severity |
Stars on GitHub
See 12 sast-skills alternatives
Reverse engineer anything with agents, from app behavior down to native binaries.
@morlutoA skill pack for authorized reverse engineering, security research, and penetration testing that routes tasks to the right skill and sets up needed tools on demand. It covers API security assessment and Android APK analysis, among others.
 @zhaoxuya520
Gives an AI agent the step-by-step workflow a senior security analyst follows, covering when to use each technique, what to check first, how to run it and how to verify the result. Covers incident response, forensics, threat intelligence, malware analysis, penetration testing and red teaming.
 @mukul975
Agent skill + stdlib Python service to strip multi-vendor AI provenance marks from text and files, for privacy and hygiene on content you own. The skill is a thin client: it drives the machinery over HTTP, so the agent host needs no Python.
 @guillaumemeyer
Install it with the command on its page. It includes sast-analysis, sast-businesslogic, sast-fileupload. Its skills do not fire on their own yet. Free and open source.
Is this plugin yours?
Claim it with GitHubSubmit a pluginPromote it