
Agent Orchestration
MCP
bernstein
Ships with bernstein: The open-source governance layer for AI agents: write the rules declaratively, Bernstein enforces them and produces the verifiable, replayable record. Free, Apache-2.0.…
Claude Code
$ uv tool install bernstein # or: pipx install bernstein
Codex
$ uv tool install bernstein # or: pipx install bernstein
Cursor
$ uv tool install bernstein # or: pipx install bernstein
Gemini CLI
$ uv tool install bernstein # or: pipx install bernstein
GitHub Copilot
$ uv tool install bernstein # or: pipx install bernstein
OpenCode
$ uv tool install bernstein # or: pipx install bernstein
Windsurf
$ uv tool install bernstein # or: pipx install bernstein
Security report
Info
Not enough data
Known flaws
Not published
Signed build
Not published
Maintained
Nov 11, 2026
Last push
Licence
Apache-2.0
Runs as
Local process
On your machine
Deprecated
Not published
Signals from public registries, not an audit. Checked Nov 14, 2026.
bernstein README

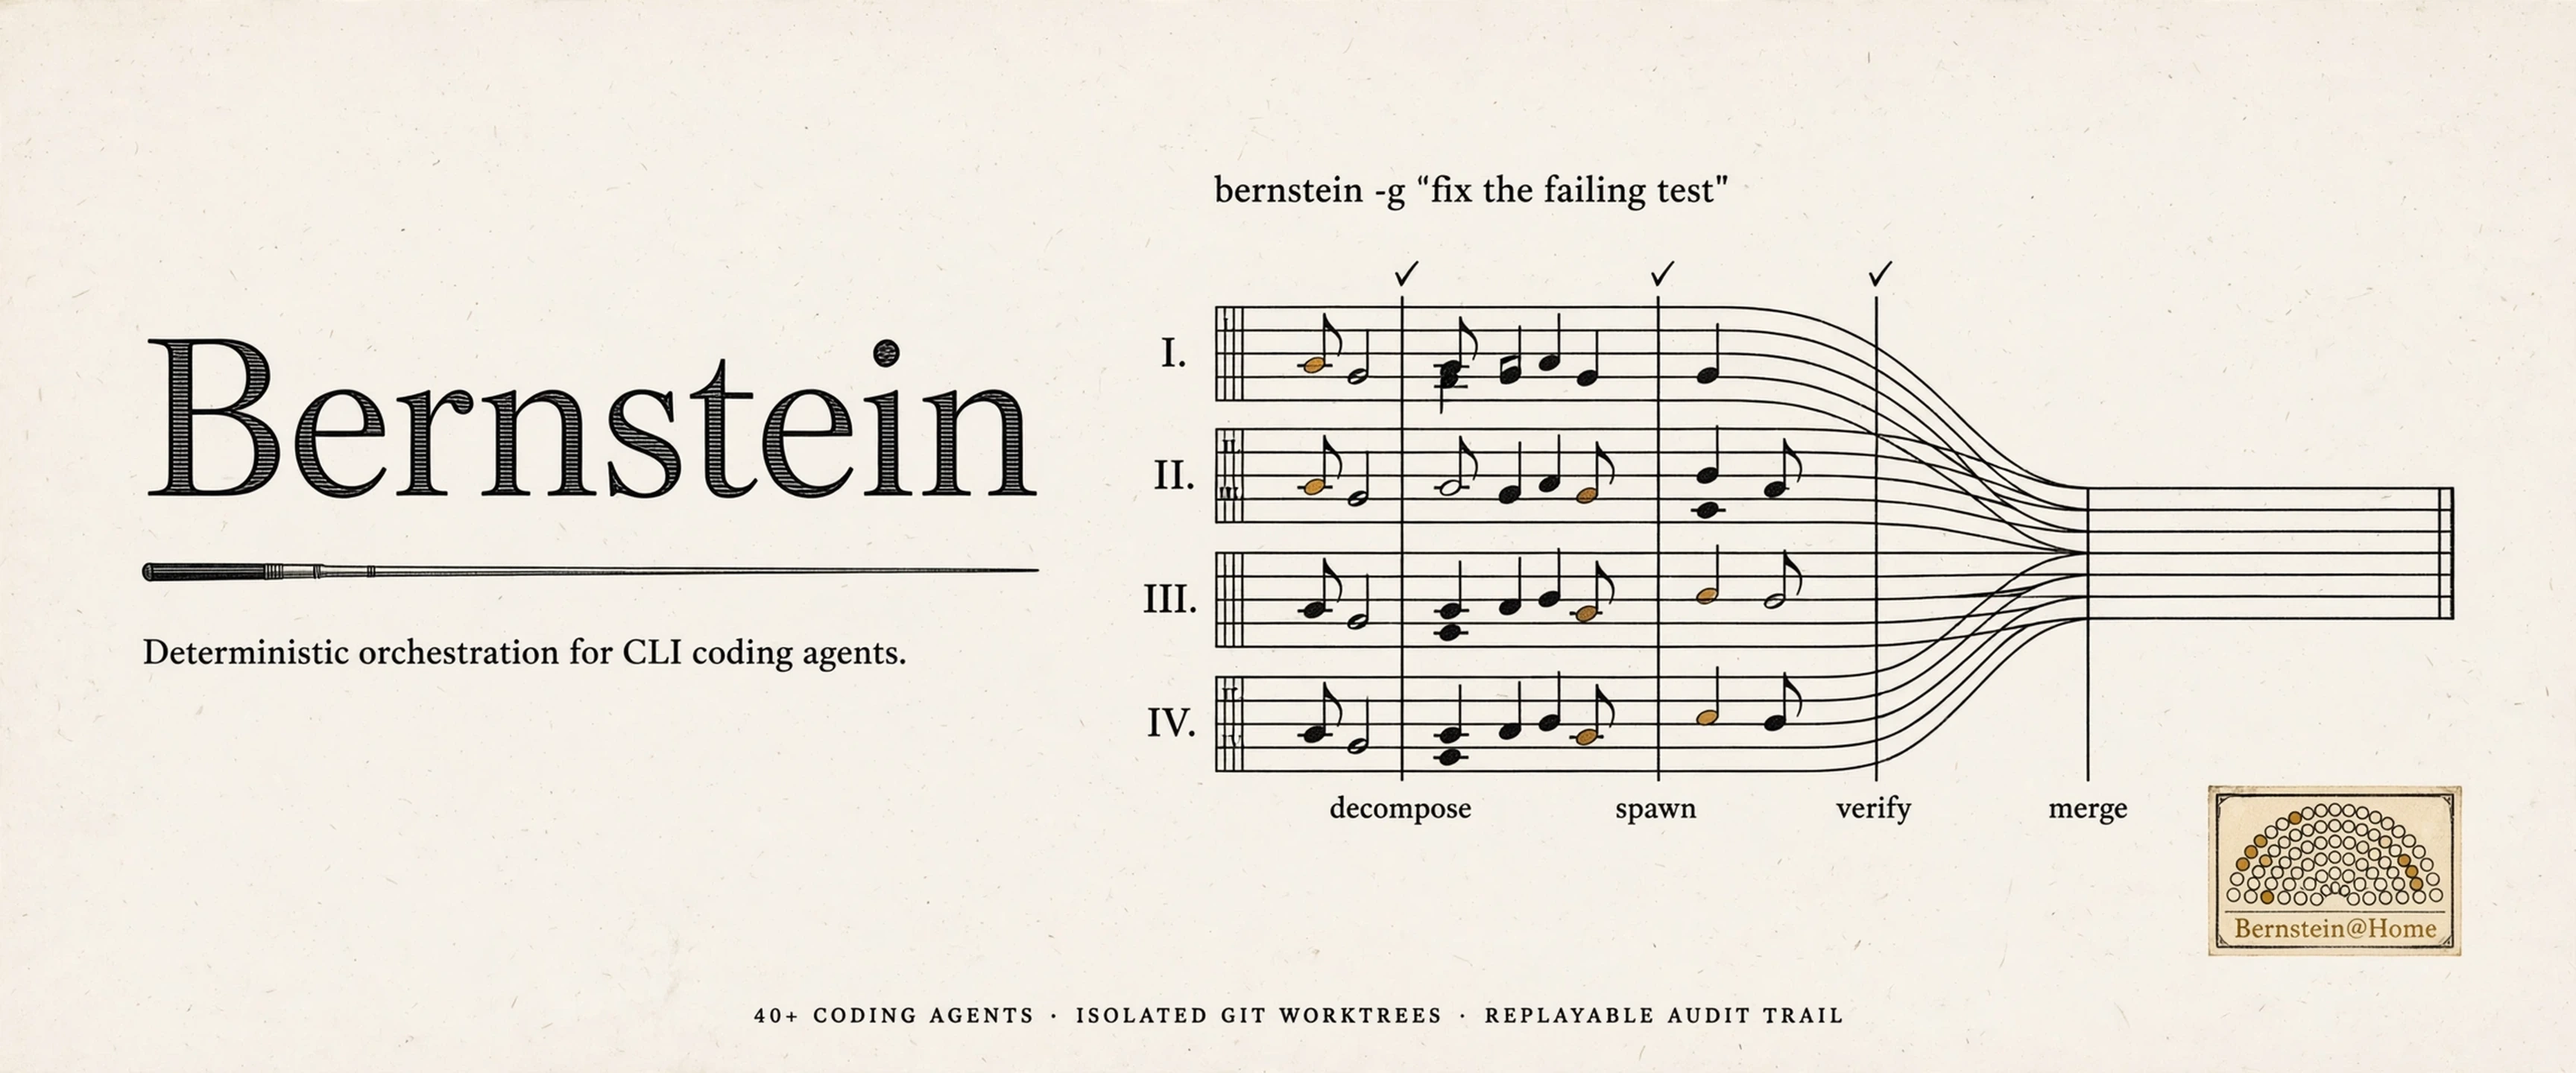
"To achieve great things, two things are needed: a plan and not quite enough time." - attributed to Leonard Bernstein
the open-source governance layer for AI agents




website · docs · install · first run · glossary · limitations · name policy · discord · sponsor
简体中文 · 繁體中文 · 日本語 · 한국어 · हिन्दी · বাংলা · Русский · Español · Português · Deutsch · Français · Italiano · Nederlands · Polski · Svenska · Suomi · Українська · Türkçe · العربية · עברית · Bahasa Indonesia · Tiếng Việt · ไทย
Status: beta. Solo-maintained, under active development. The version number counts releases, not maturity - minor versions may change interfaces. Pin the version for anything you depend on; regressions get fixed fast, file them.
Bernstein is the open-source governance layer for AI agents. It runs on policy as code: you write the policy - who may do what, what needs approval, what must be recorded - and Bernstein enforces it and produces the verifiable record. A deterministic scheduler - no model in the coordination loop - runs agents in parallel, gates what they produce, and records every step, so a run can be verified after the fact, offline, from the artifacts alone. CLI coding agents work out of the box (Claude Code, Codex, Gemini CLI, and 50+ more), and the same layer governs any agent workload: the deliverable can be a diff, a research report, a dataset, or an audit evidence pack. Air-gap install profile included. Apache-2.0.
at a glance
Five things set it apart; everything after is detail.
- No LLM in the coordination loop. Scheduling is plain Python, so a run is reproducible end to end. Replay yesterday's plan and get yesterday's task graph.
- Hardware key evidence. Offline PIV custody and FIDO2 approval verifiers share the receipt protocol, with pinned trust and explicit time. Token custody does not raise TRACE trust levels. See hardware key evidence.
- Checkable after the fact. The replay journal records every run, and the always-on lineage spine records every lineage-bearing step; the opt-in HMAC-chained audit log (
BERNSTEIN_AUDIT=1) adds receipts you verify offline. Non-determinism surfaces as a hash mismatch at the exact step, not a flaky re-run. Non-code deliverables get the same treatment: a task can declare an artifact contract (report, dataset, action log, ops result) and completes on a signed lineage receipt rather than a git commit. - Isolated by construction. Each coding task gets its own git worktree behind merge gates; artifact-mode tasks get a working directory under
.sdd/workspaces/. Agents share no mutable workspace by default; the only shared state is the task backlog, which is claimed atomically. Stricter filesystem enforcement is opt-in, from the sandbox backends. Disable worktrees and every task runs in the shared checkout. - Broad and local. More than 50 selectable CLI agent adapters plus a generic
--promptwrapper, file-based state, no SaaS hop, no third-party data plane.
The full list is on the capabilities page; the feature matrix is the exhaustive index.
what a run looks like
One YAML file declares the run: phases, roles, dependencies, and the conditions under which a node runs at all. The scheduler executes it as plain Python - nothing in the file is a prompt, and no model decides what happens next. This graph produces an audit evidence pack; the full file ships at .bernstein/workflows/audit-evidence-pack.yaml.
name: audit-evidence-pack
version: "1.0.0"

phases:
  - name: scope
    allowed_roles: [manager, architect]
  - name: collect
  - name: validate
    allowed_roles: [qa, security]
  - name: deliver
    allowed_roles: [security, manager]

nodes:
  define-control-inventory:
    phase: scope
    role: architect

  collect-audit-logs:
    phase: collect
    role: security
    depends_on: [define-control-inventory]

  # three more evidence streams collect in parallel:
  # collect-sboms-and-attestations, collect-runbooks-and-policies,
  # collect-eval-results

  assemble-pack:
    phase: validate
    role: docs
    depends_on:
      - collect-audit-logs
      - collect-sboms-and-attestations
      - collect-runbooks-and-policies
      - collect-eval-results

  mock-auditor-pass:
    phase: validate
    role: qa
    depends_on: [assemble-pack]

  remediate-findings:
    phase: collect
    role: docs
    depends_on:
      - source: mock-auditor-pass
        condition: "status == 'failed'"
    retry:
      max_attempts: 3
      until: "status == 'done'"

  sign-and-deliver:
    phase: deliver
    role: security
    depends_on:
      - source: mock-auditor-pass
        condition: "status == 'done'"
flowchart LR
    inv[define-control-inventory] --> logs[collect-audit-logs]
    inv --> sbom[collect-sboms-and-attestations]
    inv --> rb[collect-runbooks-and-policies]
    inv --> ev[collect-eval-results]
    logs --> pack[assemble-pack]
    sbom --> pack
    rb --> pack
    ev --> pack
    pack --> gate{mock-auditor-pass}
    gate -->|failed| fix["remediate-findings (retry x3)"]
    gate -->|done| sign[sign-and-deliver]
Each node is claimed by an agent whose role the phase allows; role fences and approval gates hold no matter what the agent does inside the task. A coding node completes behind merge gates in its own git worktree. The nodes above complete differently: an artifact contract names the deliverable (report, dataset, scan, action log), and the node finishes on a signed lineage receipt instead of a commit. Same scheduler, same journal, same offline verification - whether the graph ships code, research, an ops change, or a mix of all three. Ready-made graphs for software, research, docs, enterprise, and contributor workflows live in .bernstein/scenarios/.
install in 30 seconds
uv tool install bernstein    # or: pipx install bernstein
bernstein init
bernstein doctor             # checks a CLI agent is installed and authenticated
bernstein -g "fix the failing test in tests/test_foo.py"
bernstein doctor --json also exposes audit-contract findings, identical to
bernstein govern audit --only INS --json for the same installation observations.
The normal doctor report keeps its existing display. See the
doctor operations guide for stable check IDs.
Stats
1,206
Stars
186
Forks
Active
Maintenance
Python
Language
Apache-2.0
License
Last commit
Created

Ships withbernstein
1.2k26 skills1 agent1 MCP
Stars on GitHub
Momentum
- stars in total
- 1.2k
More MCP servers from other plugins.

paperclip
MCPShips with paperclip: Open-source orchestration for teams of AI agents. If OpenClaw is an employee, Paperclip is the company.…
 @paperclipaiInstall MCP

t
MCPShips with oh-my-claudecode: For Codex users: Check out oh-my-codex — the same orchestration experience for OpenAI Codex CLI.…
 @yeachan-heoInstall MCP
Questions about bernstein.
- Which coding agents can use bernstein?
- bernstein works in any agent that reads an MCP config file: Claude Code, Codex, Cursor, Gemini CLI, GitHub Copilot, OpenCode and Windsurf. Each agent reads it from its own file; this page names the file for each one.