
Security
MCP
prowler
Scans cloud accounts against security best practices and compliance benchmarks such as CIS.
Claude Code
> /plugin marketplace add prowler-cloud/prowler> /plugin install prowler@prowler-plugins
Codex
$ pip install prowler
Cursor
{
  "mcpServers": {
    "prowler": {
      "url": "https://mcp.prowler.com/mcp",
      "headers": {
        "Authorization": "Bearer YOUR_TOKEN"
      }
    }
  }
}
Add it to mcp.json.
Gemini CLI
{
  "mcpServers": {
    "prowler": {
      "httpUrl": "https://mcp.prowler.com/mcp",
      "headers": {
        "Authorization": "Bearer YOUR_TOKEN"
      }
    }
  }
}
Add it to settings.json.
GitHub Copilot
$ copilot mcp add --transport http prowler https://mcp.prowler.com/mcp --header "Authorization: Bearer YOUR_TOKEN"
OpenCode
{
  "mcp": {
    "prowler": {
      "type": "remote",
      "url": "https://mcp.prowler.com/mcp",
      "headers": {
        "Authorization": "Bearer YOUR_TOKEN"
      }
    }
  }
}
Add it to opencode.json.
Windsurf
{
  "mcpServers": {
    "prowler": {
      "serverUrl": "https://mcp.prowler.com/mcp",
      "headers": {
        "Authorization": "Bearer YOUR_TOKEN"
      }
    }
  }
}
Add it to mcp_config.json.
Security report
Found
Low risk
Known flaws
Not published
Signed build
Not published
Maintained
Nov 10, 2026
Last push
Licence
Apache-2.0
Runs as
Remote
mcp.prowler.com
Deprecated
Not published
Signals from public registries, not an audit. Checked Nov 11, 2026.
prowler README


Prowler is the Open Cloud Security Platform trusted by thousands to automate security and compliance in any cloud environment. With thousands of ready-to-use checks and compliance frameworks, Prowler delivers real-time, customizable monitoring and seamless integrations, making cloud security simple, scalable, and cost-effective for organizations of any size.
The Agentic Cloud Defender
Try Prowler Cloud
Join our Prowler community!




Description
Prowler is the world’s most widely used Open-Source Cloud Security Platform that automates security and compliance across any cloud environment. With thousands of ready-to-use security checks, remediation guidance, and compliance frameworks, Prowler is built to “Secure ANY Cloud at AI Speed”. Prowler delivers AI-driven, customizable, and easy-to-use assessments, dashboards, reports, and integrations, making cloud security simple, scalable, and cost-effective for organizations of any size.
Prowler includes hundreds of built-in controls to ensure compliance with standards and frameworks, including:
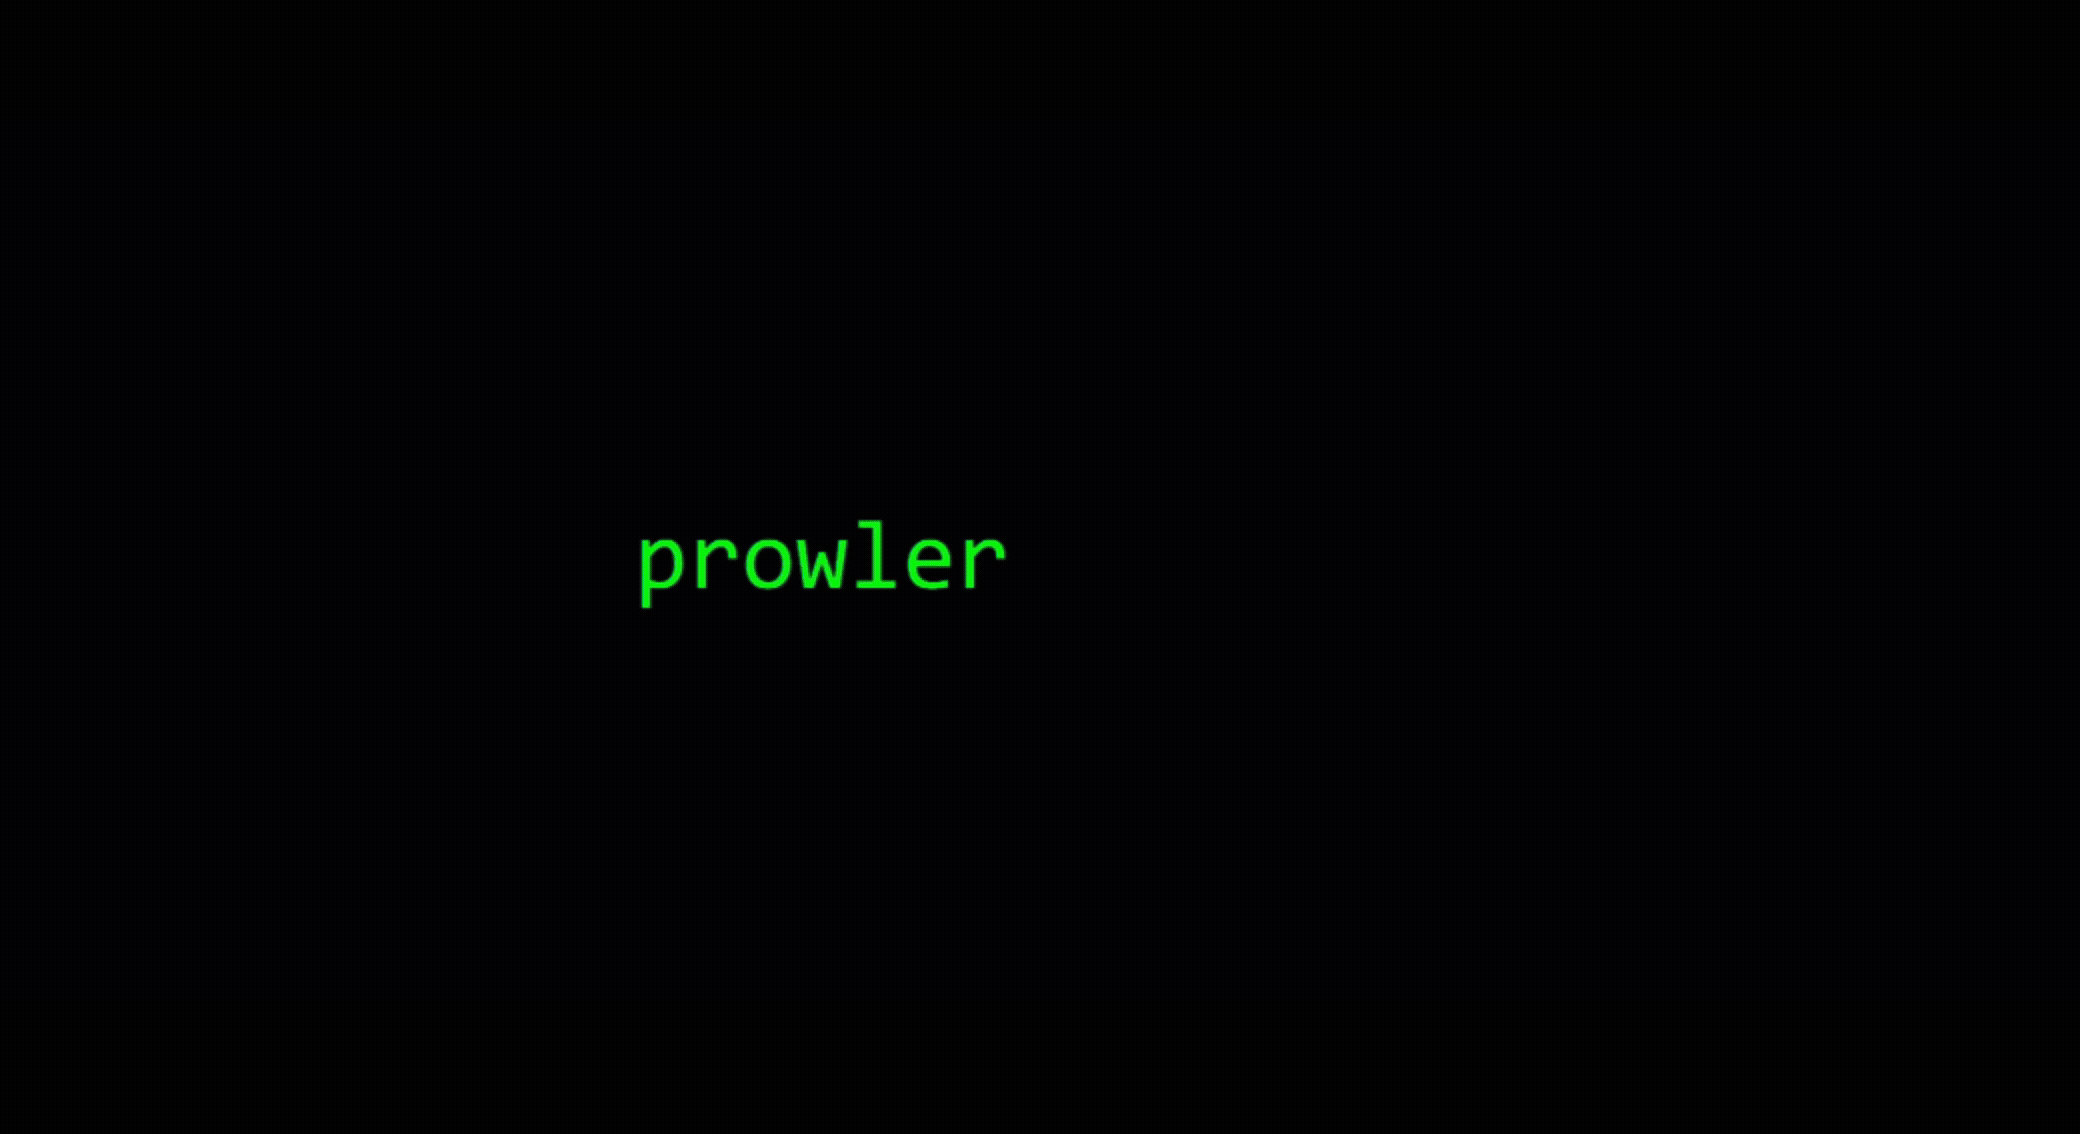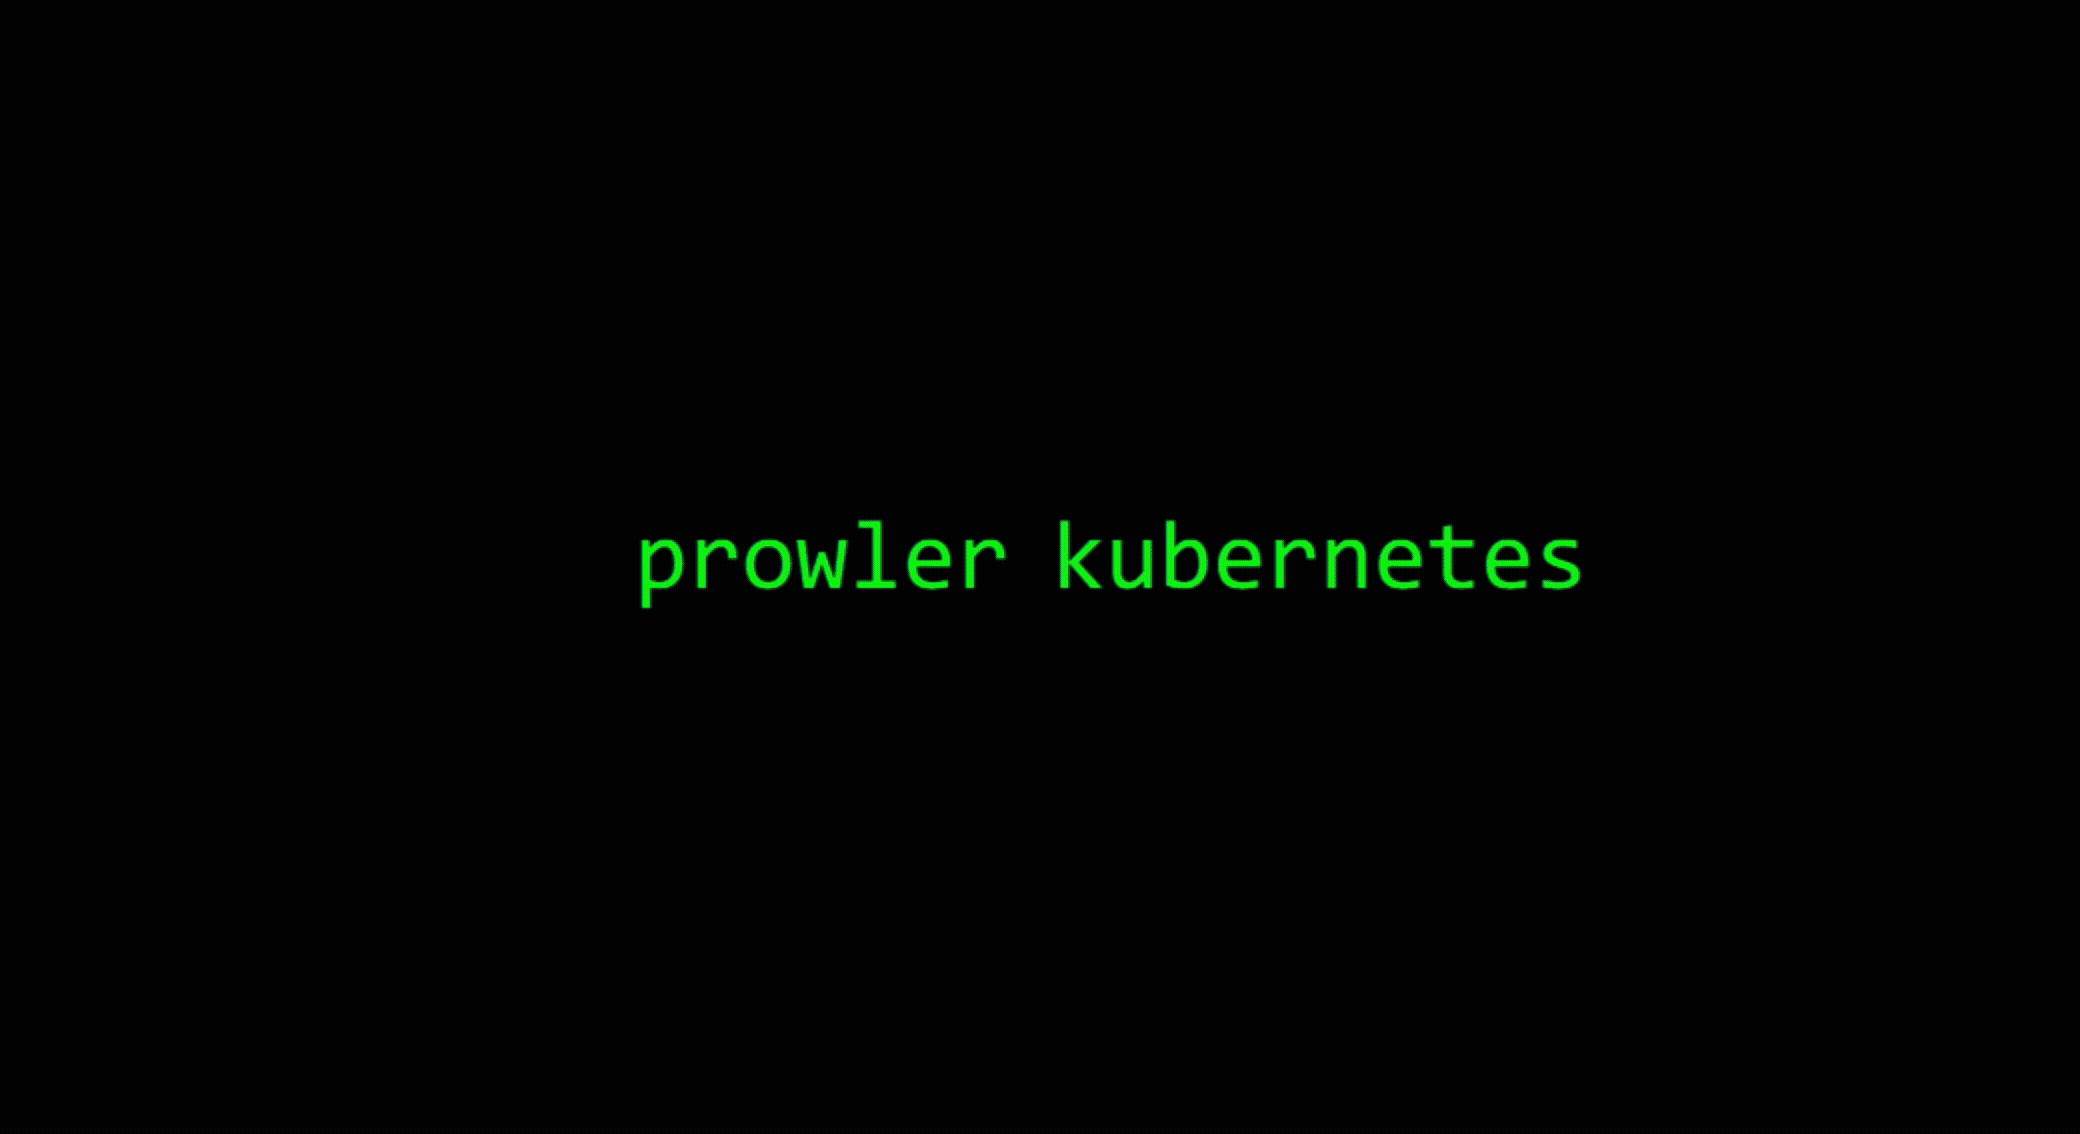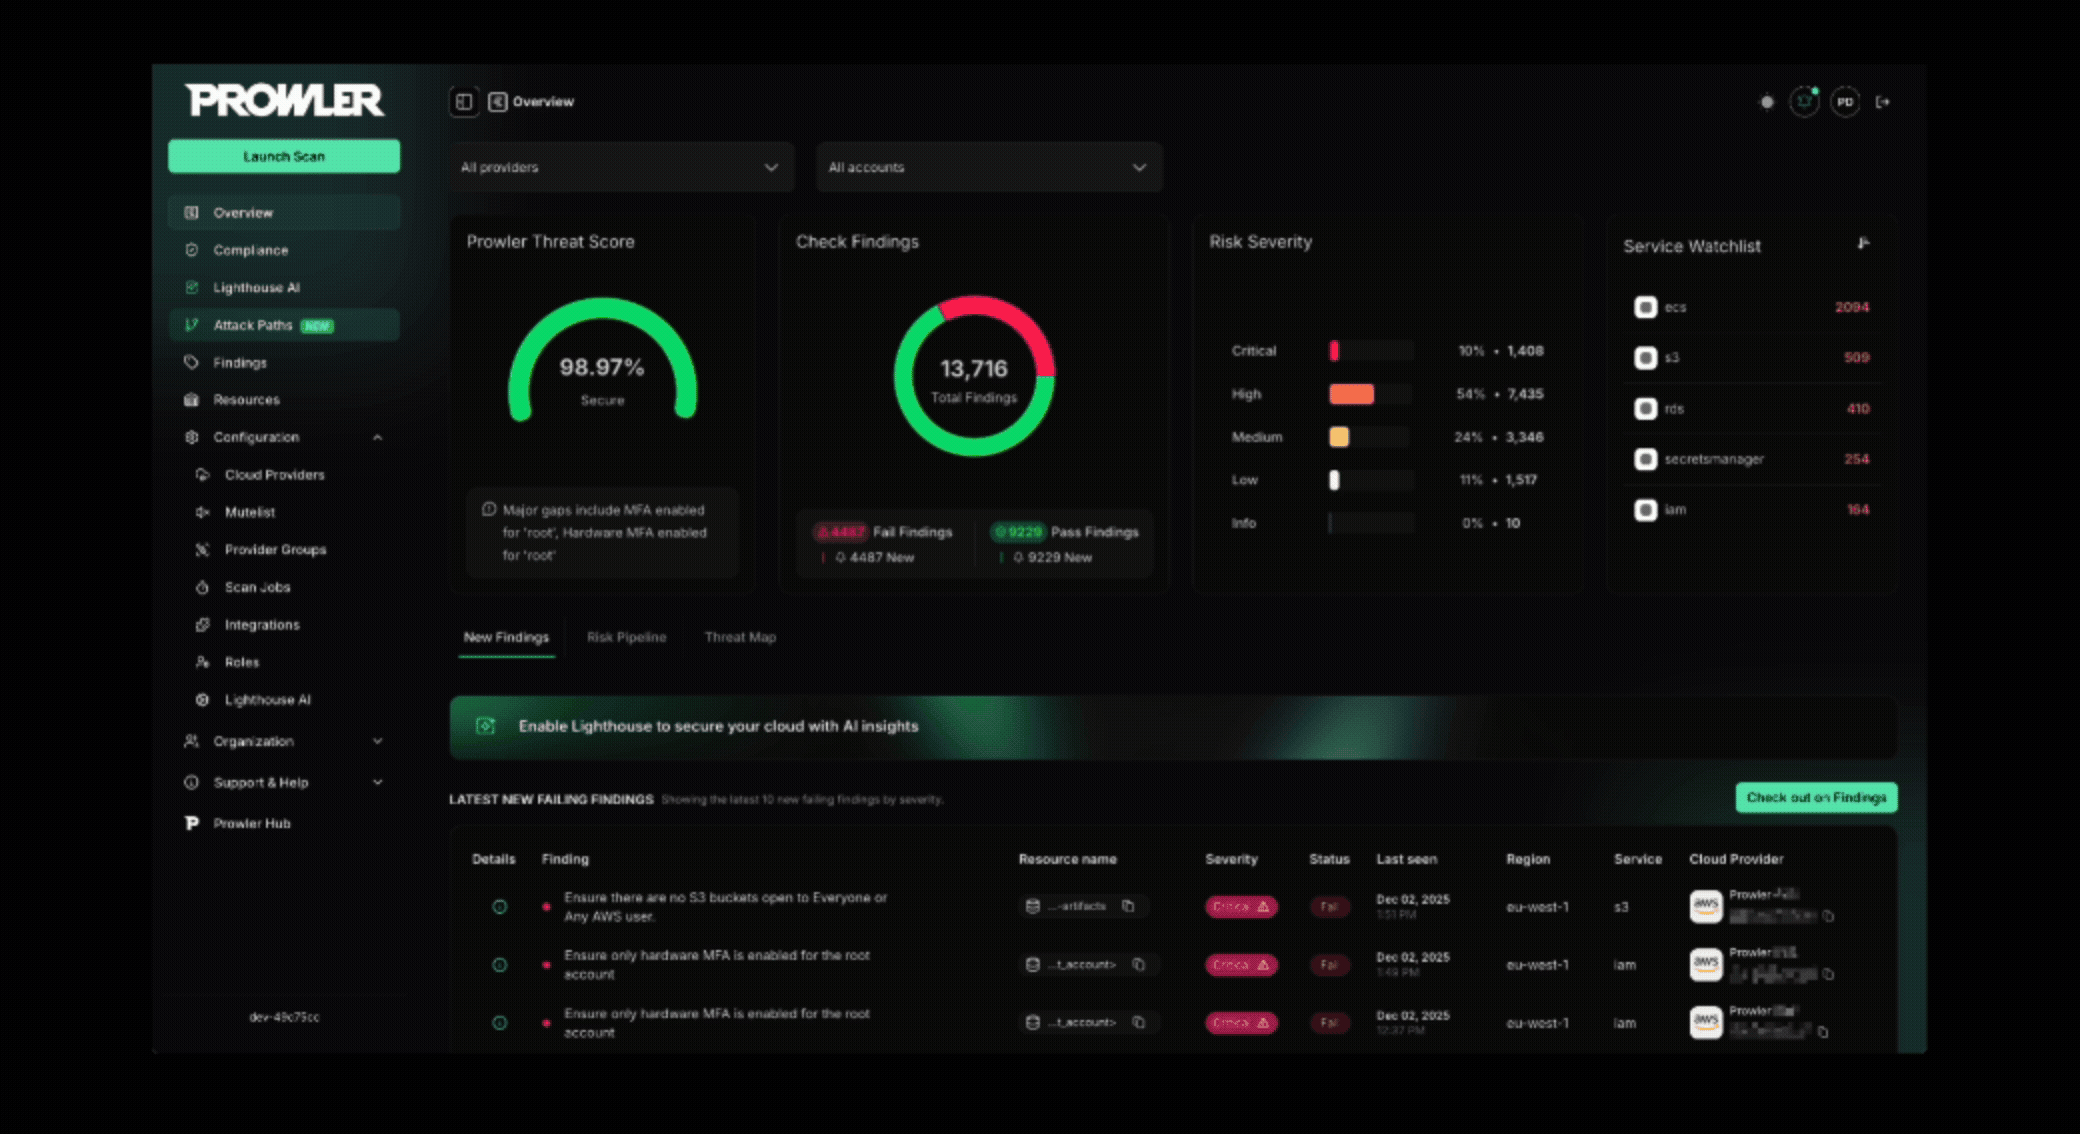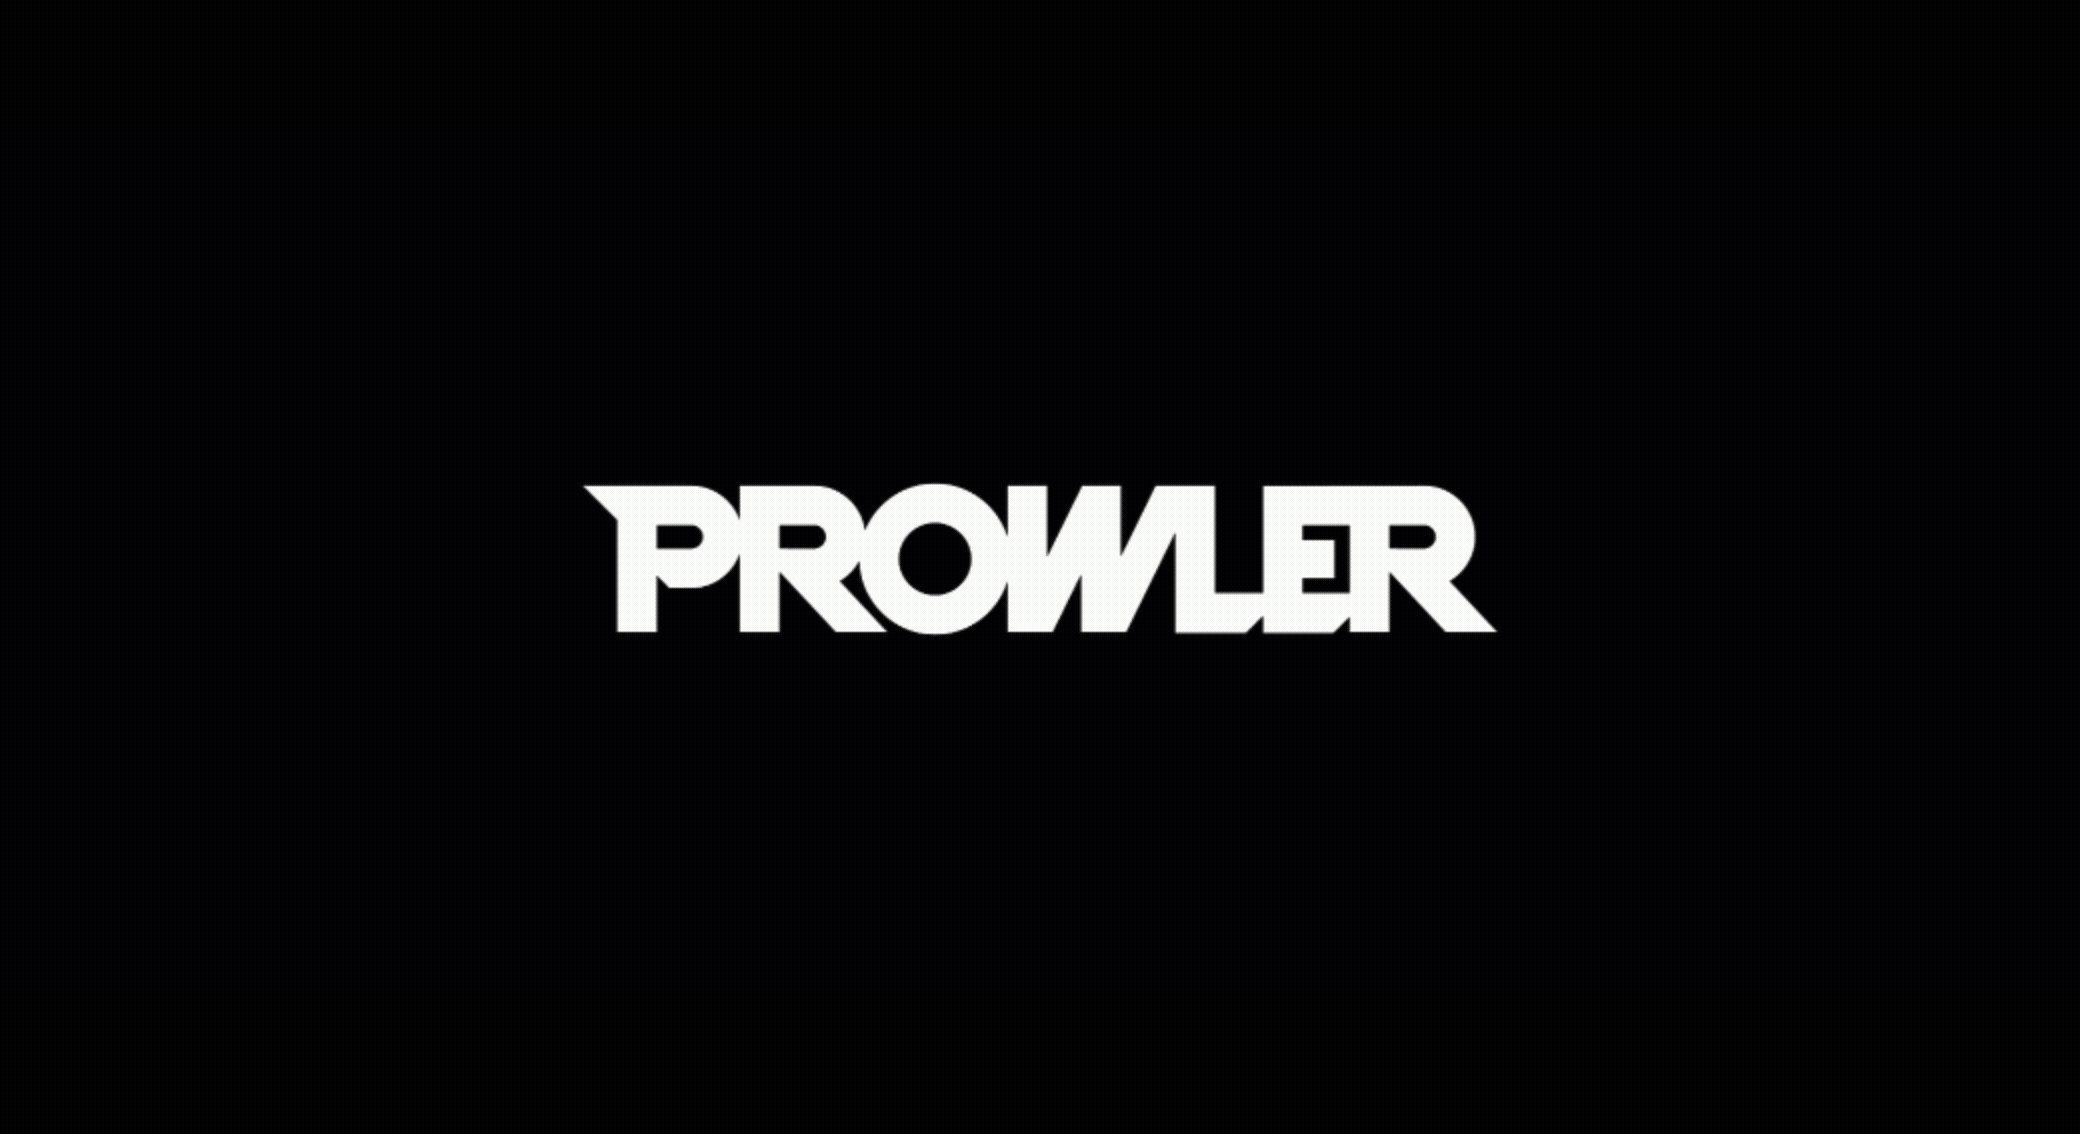
- Prowler ThreatScore: Weighted risk prioritization scoring that helps you focus on the most critical security findings first
- Industry Standards: CIS, NIST 800, NIST CSF, CISA, and MITRE ATT&CK
- Regulatory Compliance and Governance: RBI, FedRAMP, PCI-DSS, and NIS2
- Frameworks for Sensitive Data and Privacy: GDPR, HIPAA, and FFIEC
- Frameworks for Organizational Governance and Quality Control: SOC2, GXP, and ISO 27001
- Cloud-Specific Frameworks: AWS Foundational Technical Review (FTR), AWS Well-Architected Framework, and BSI C5
- National Security Standards: ENS (Spanish National Security Scheme) and KISA ISMS-P (Korean)
- Custom Security Frameworks: Tailored to your needs
Prowler Cloud & Prowler Local Server
Prowler Cloud and Prowler Local Server, its self-hosted open-source version, are web applications that simplify running Prowler across your cloud provider accounts. They provide a user-friendly interface to visualize the results and streamline your security assessments.
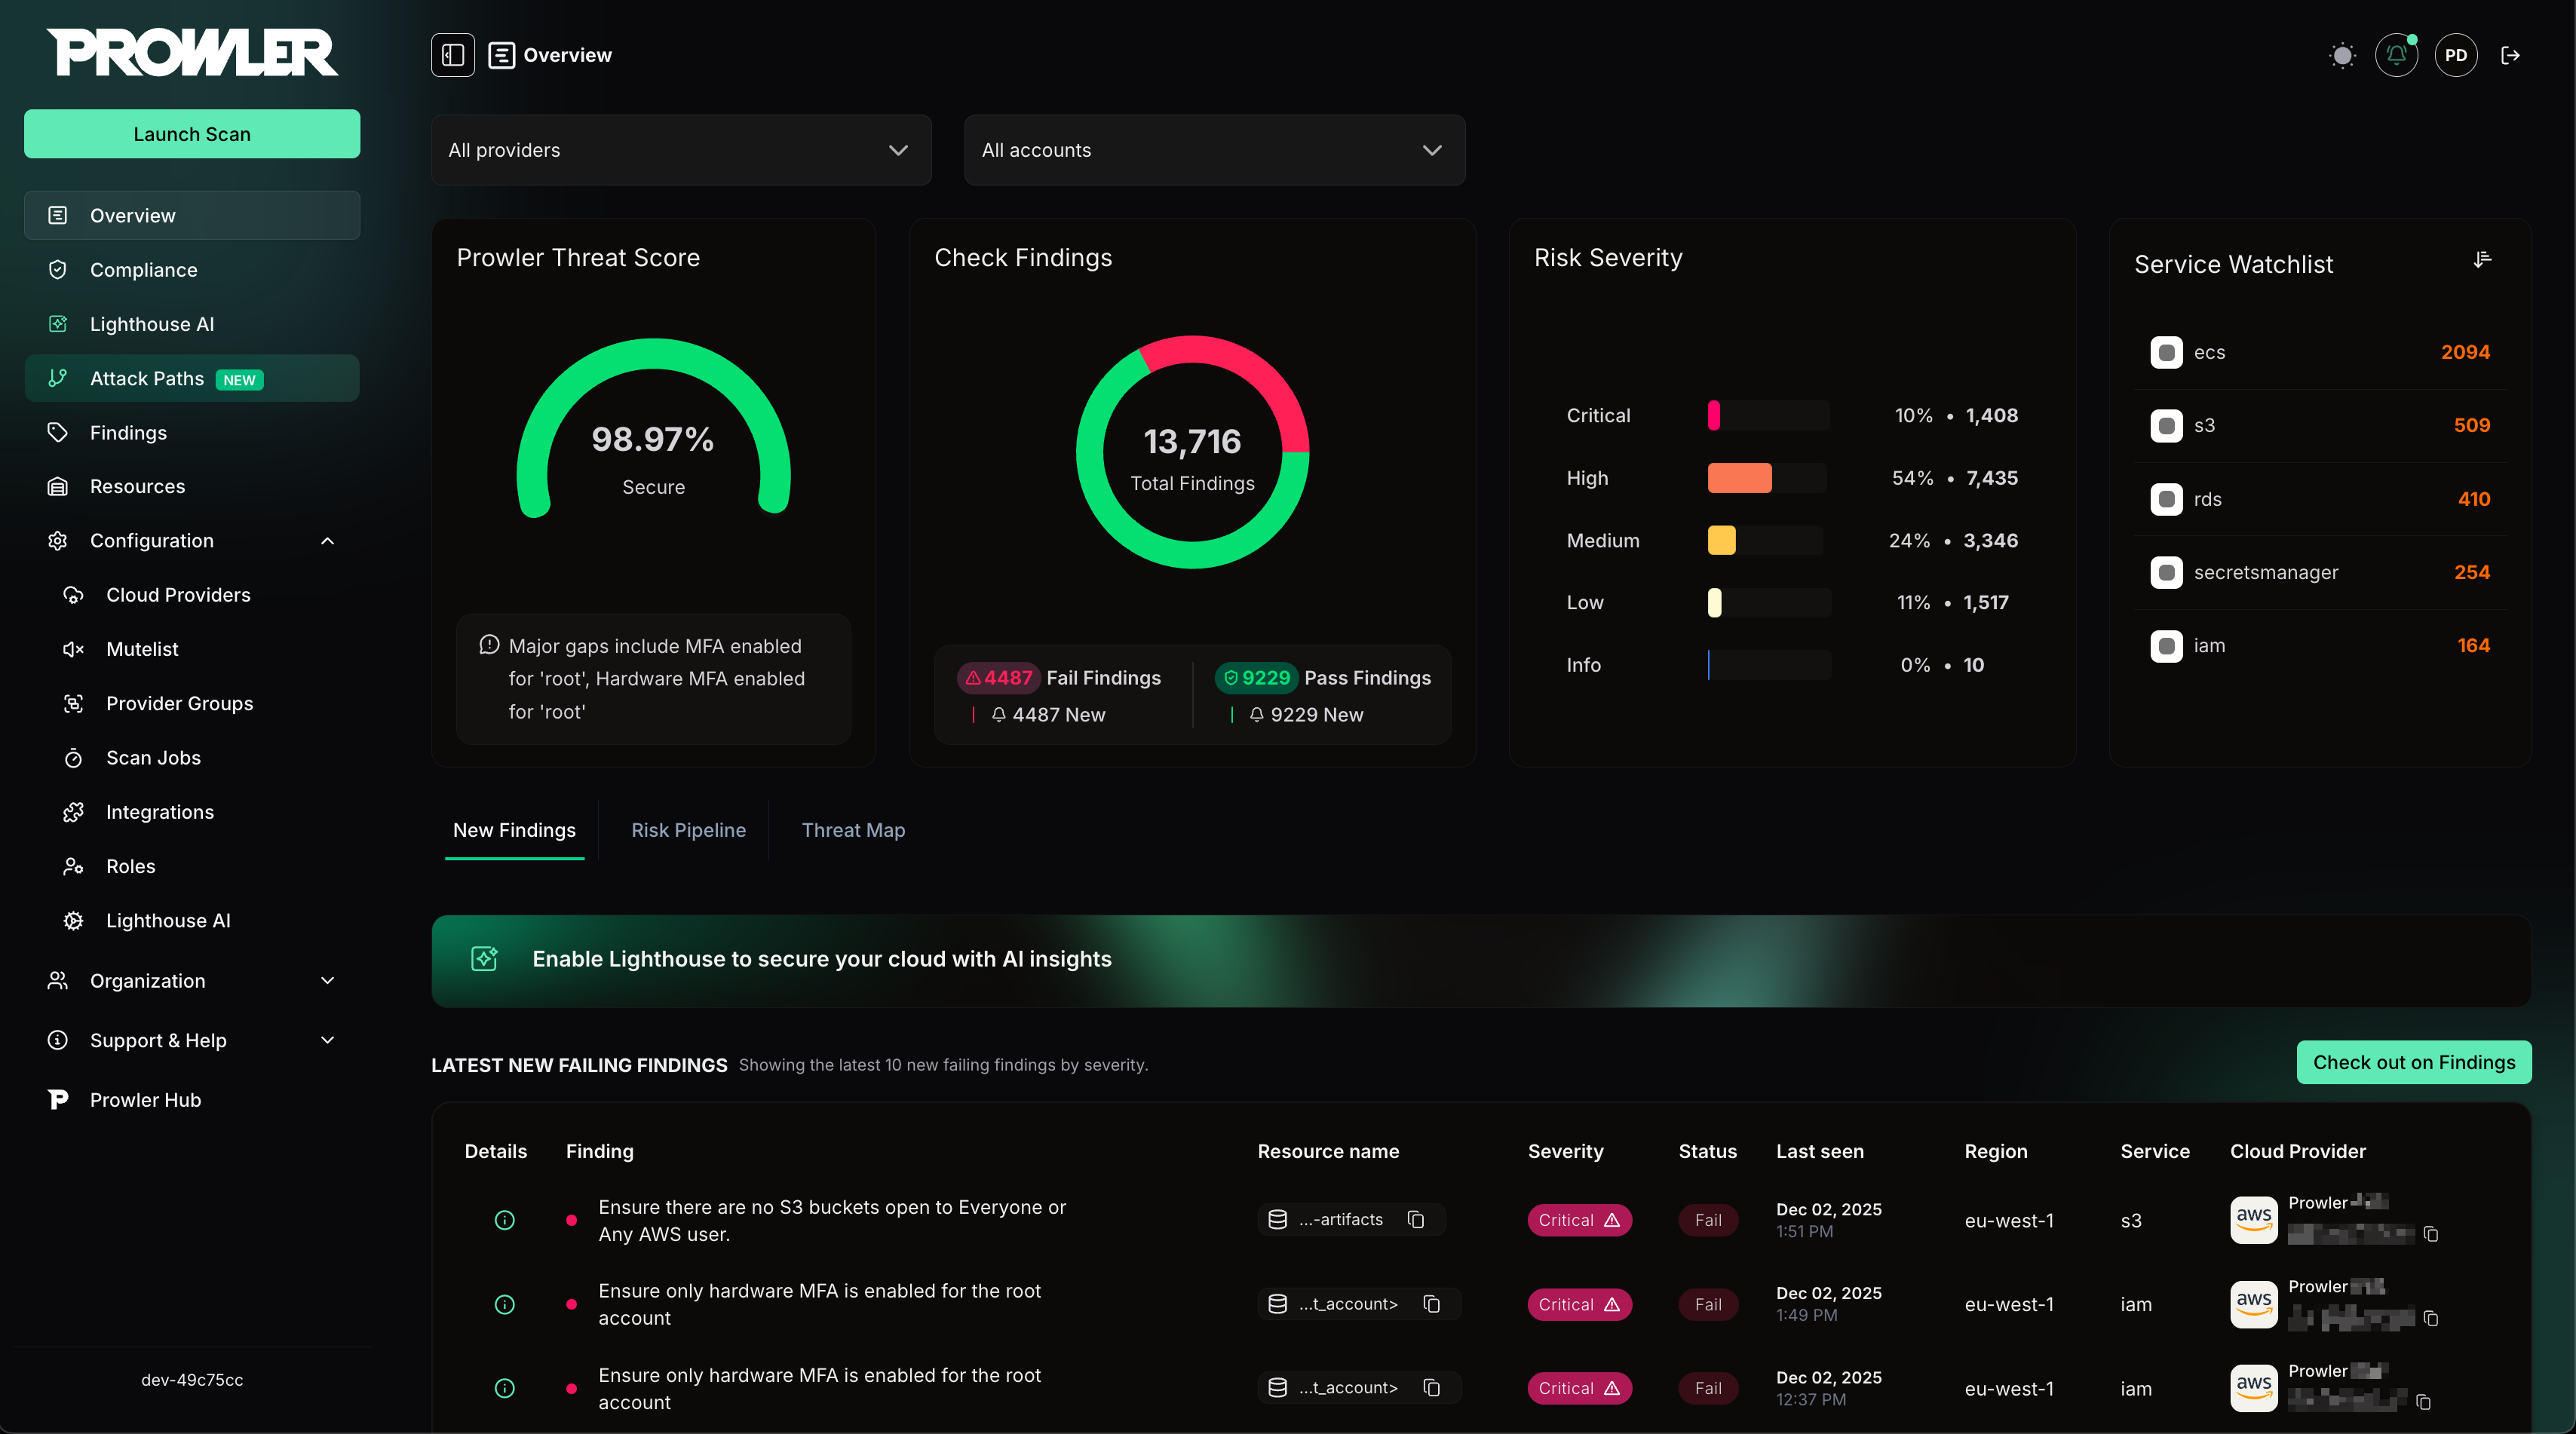
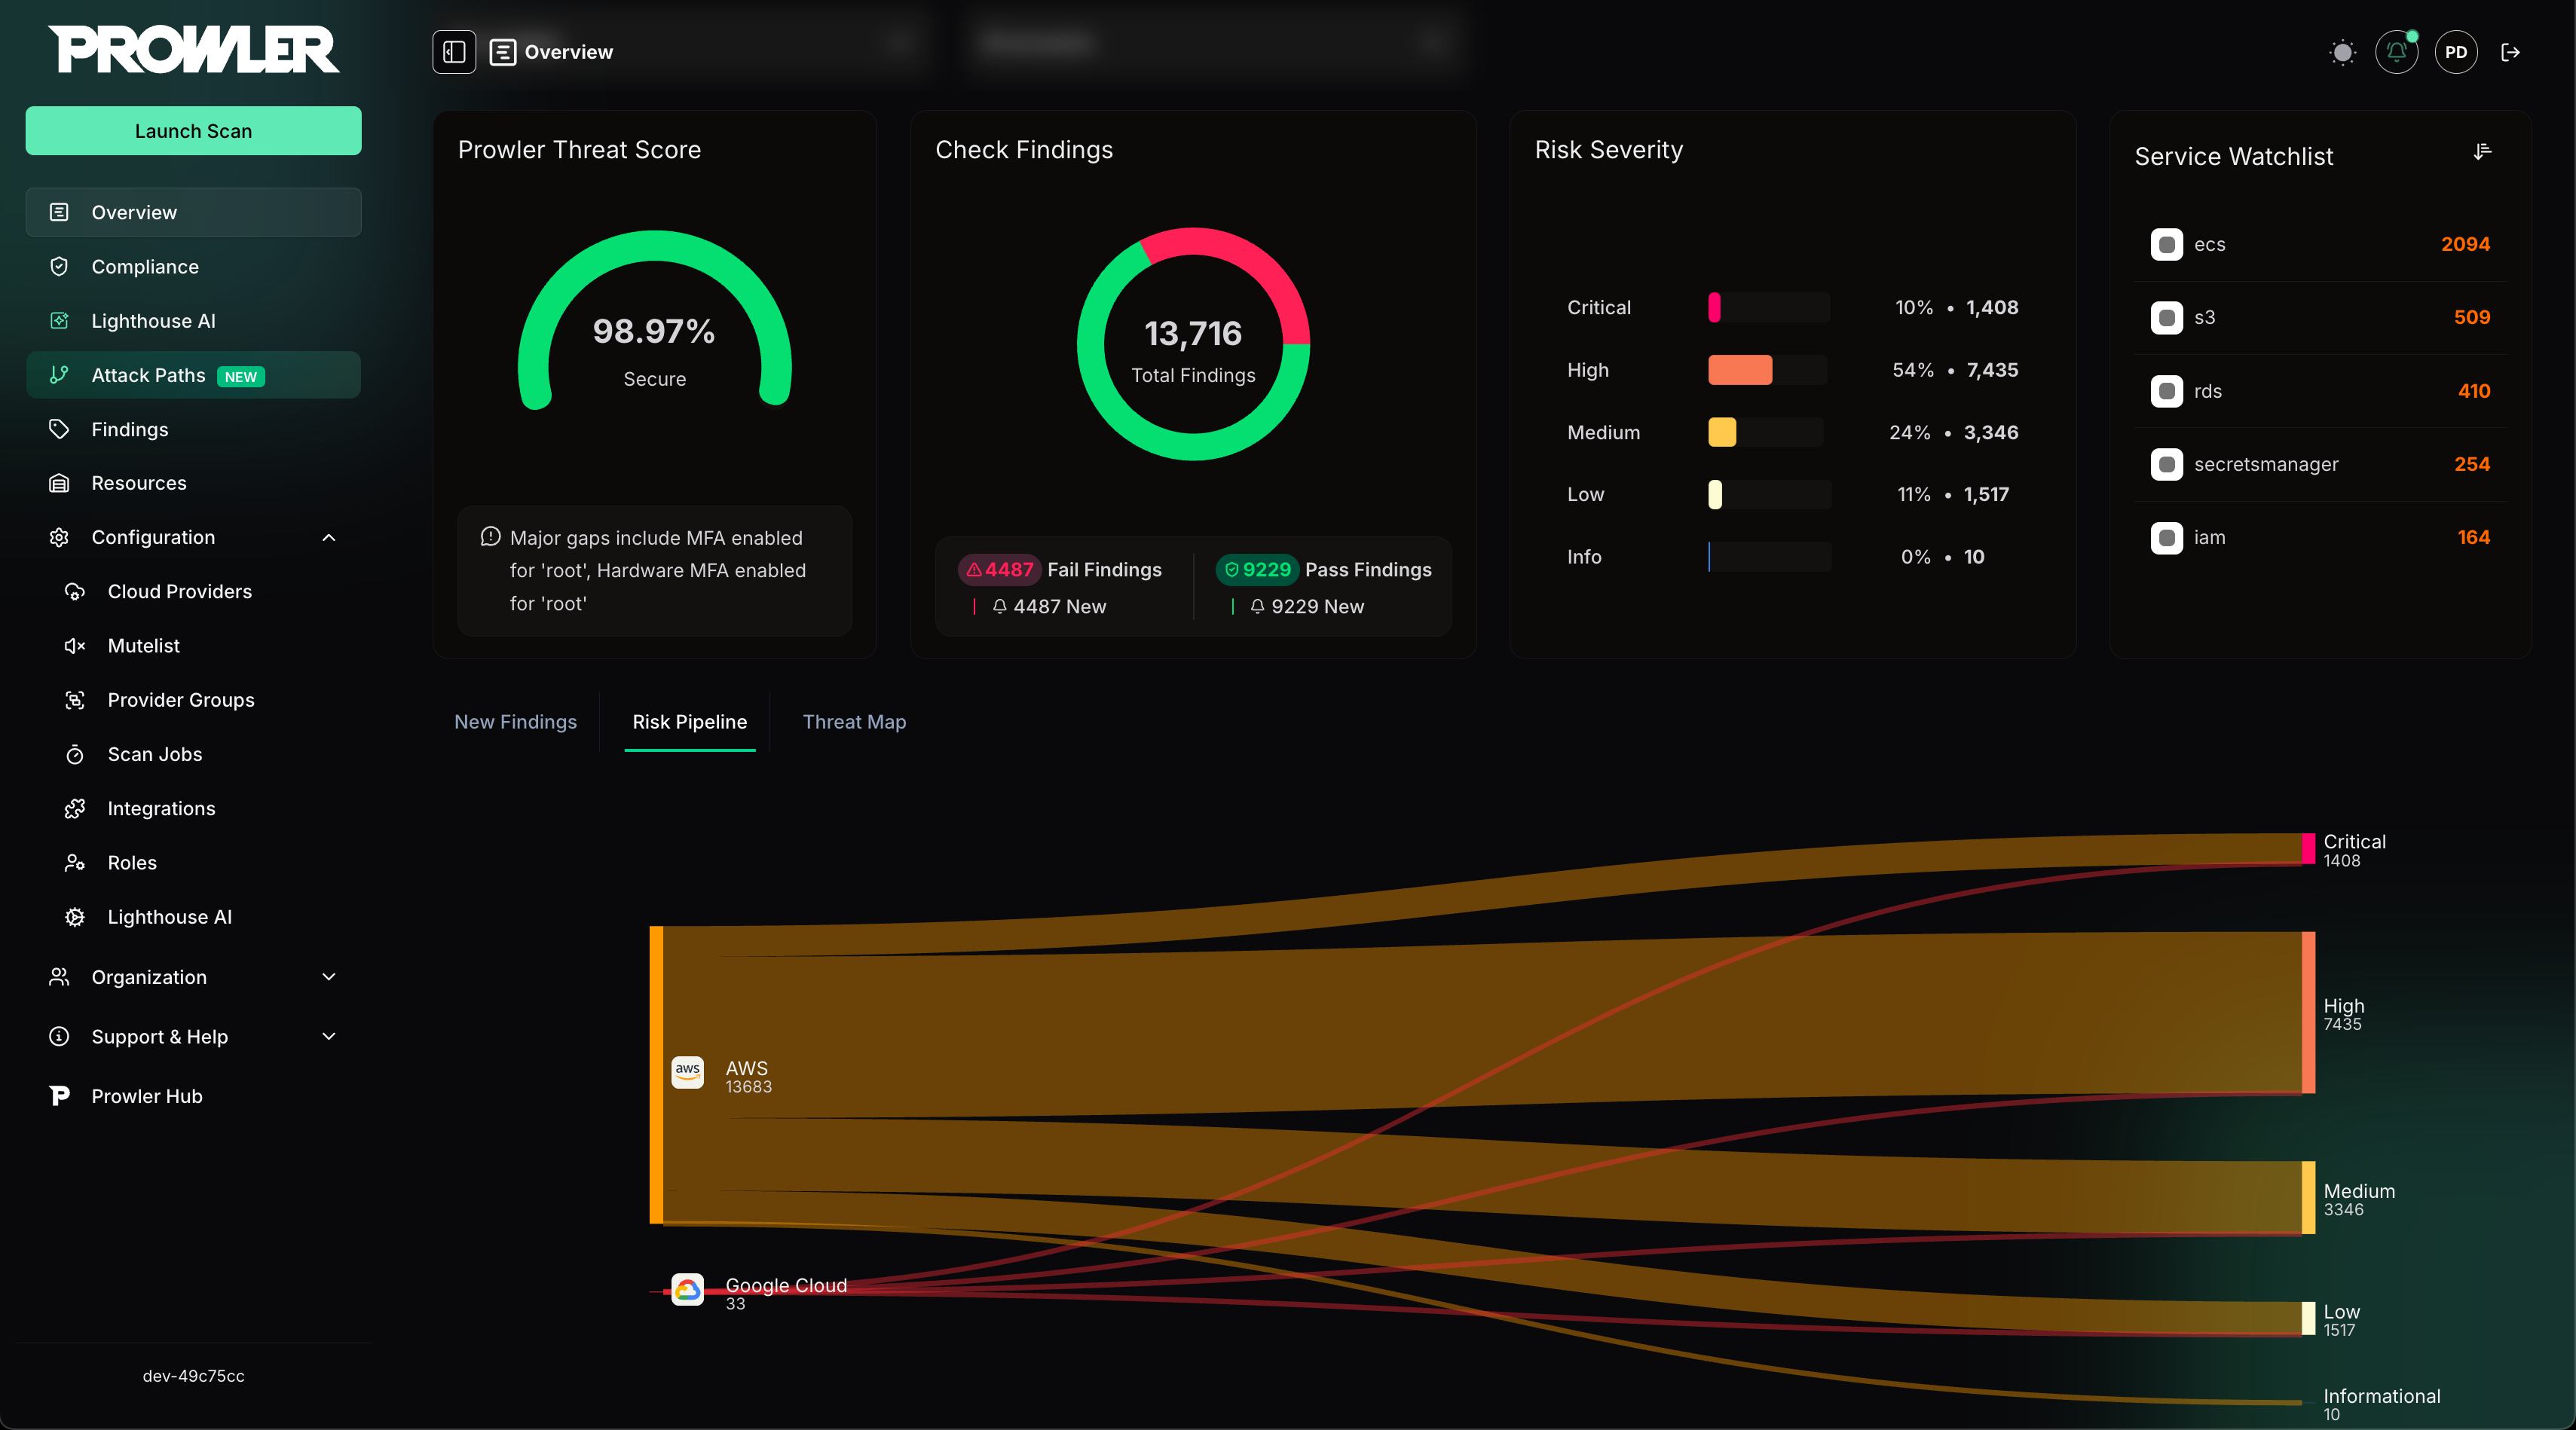
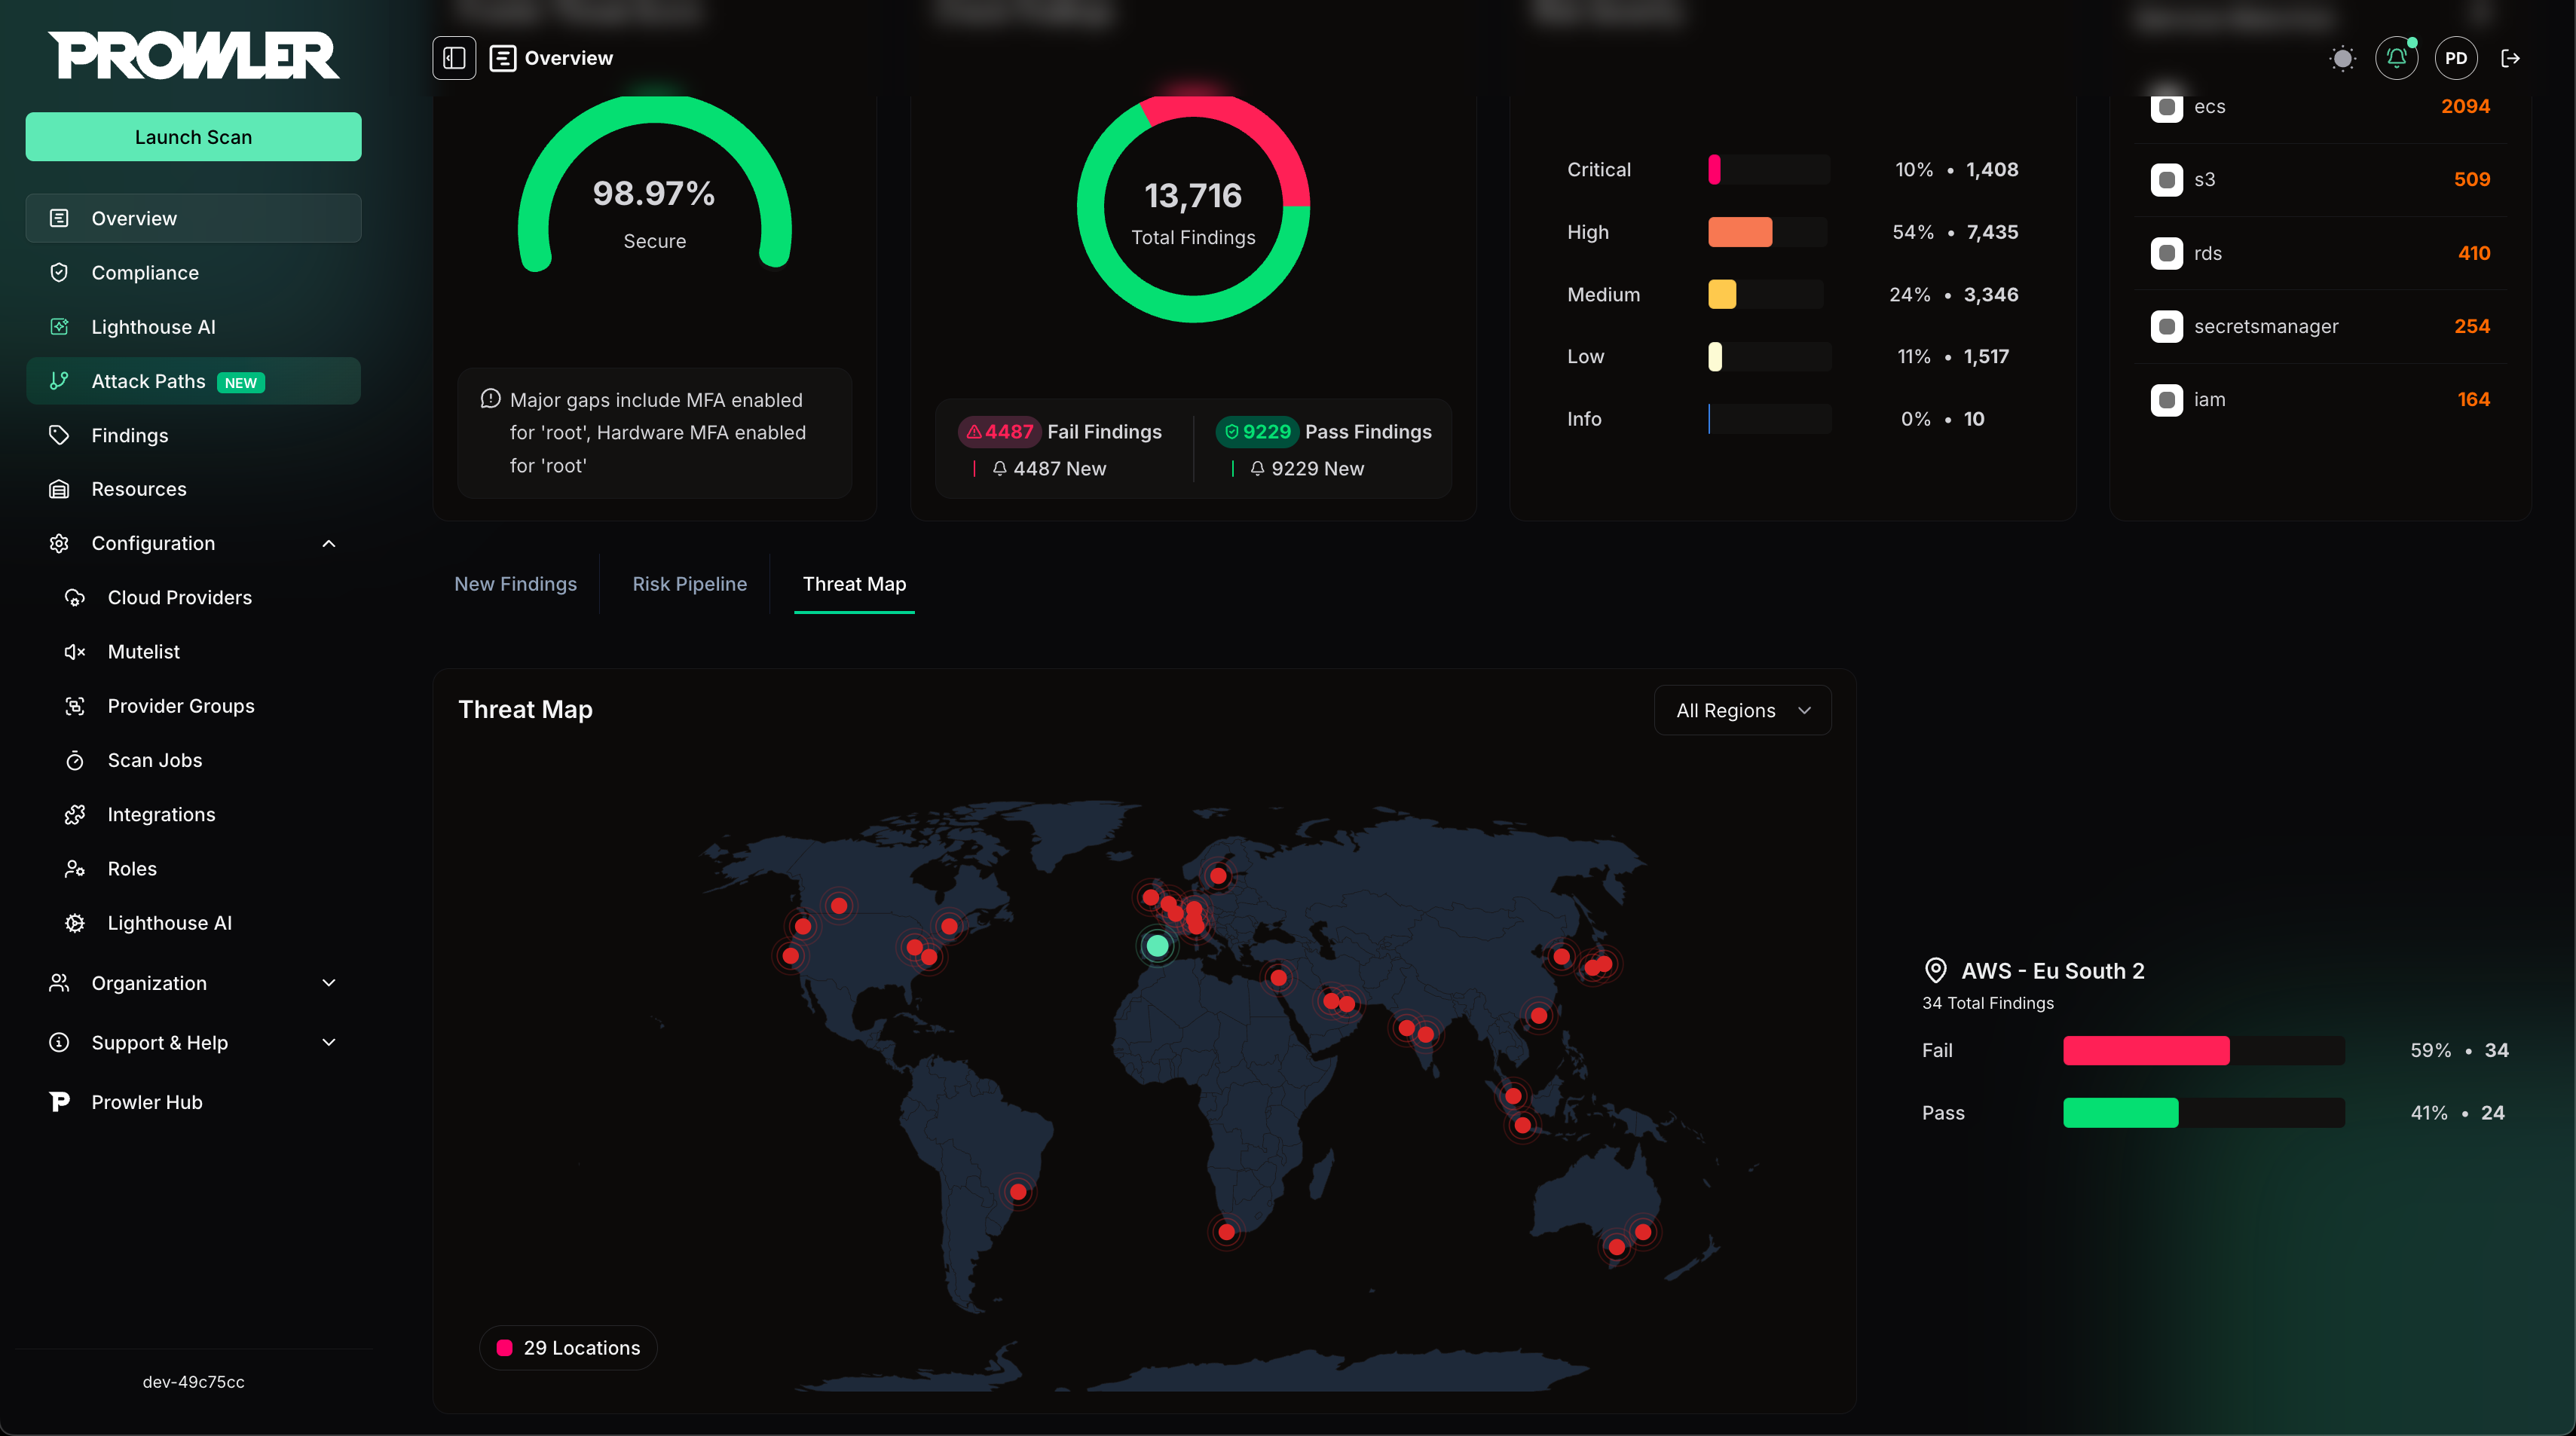
For more details, refer to the Prowler Local Server documentation
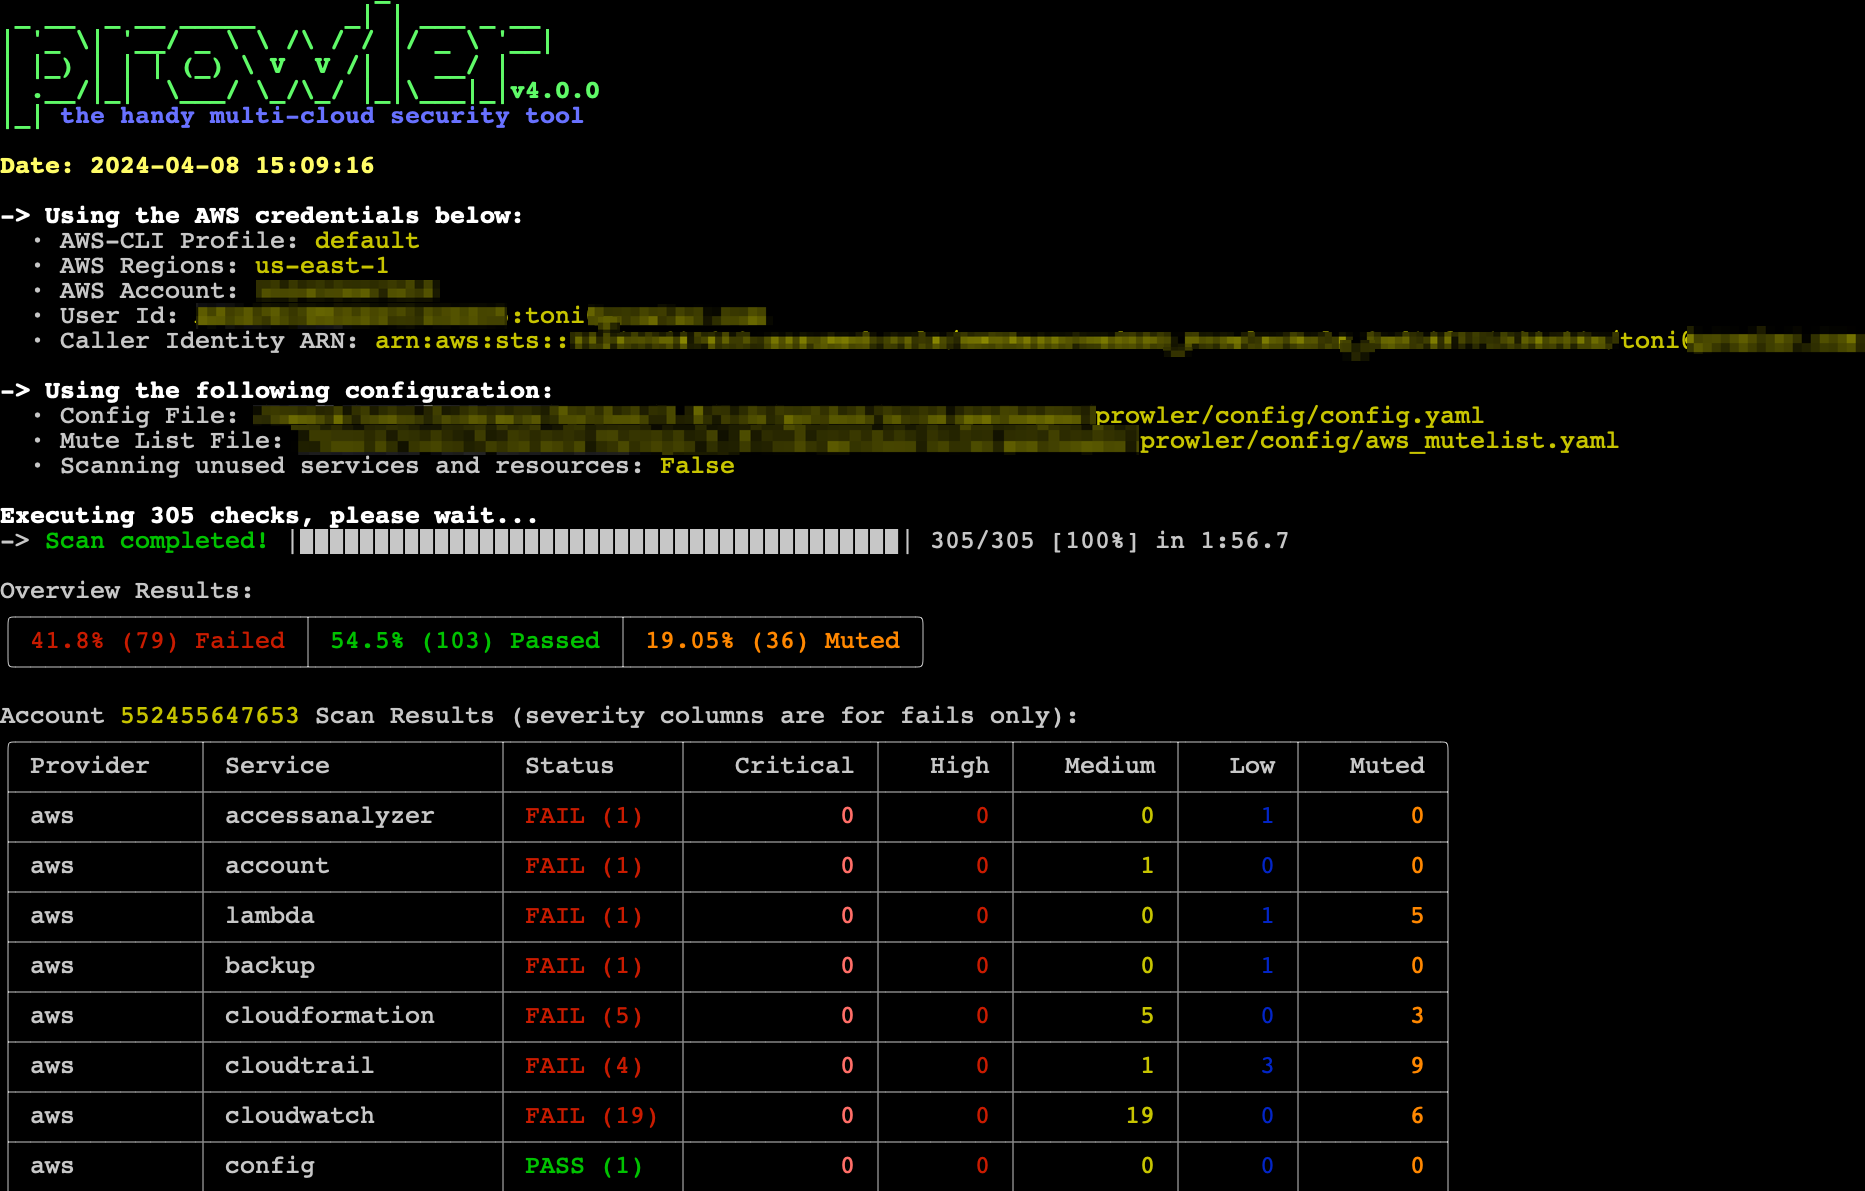
Prowler CLI
prowler <provider>
Prowler Local Dashboard
prowler dashboard
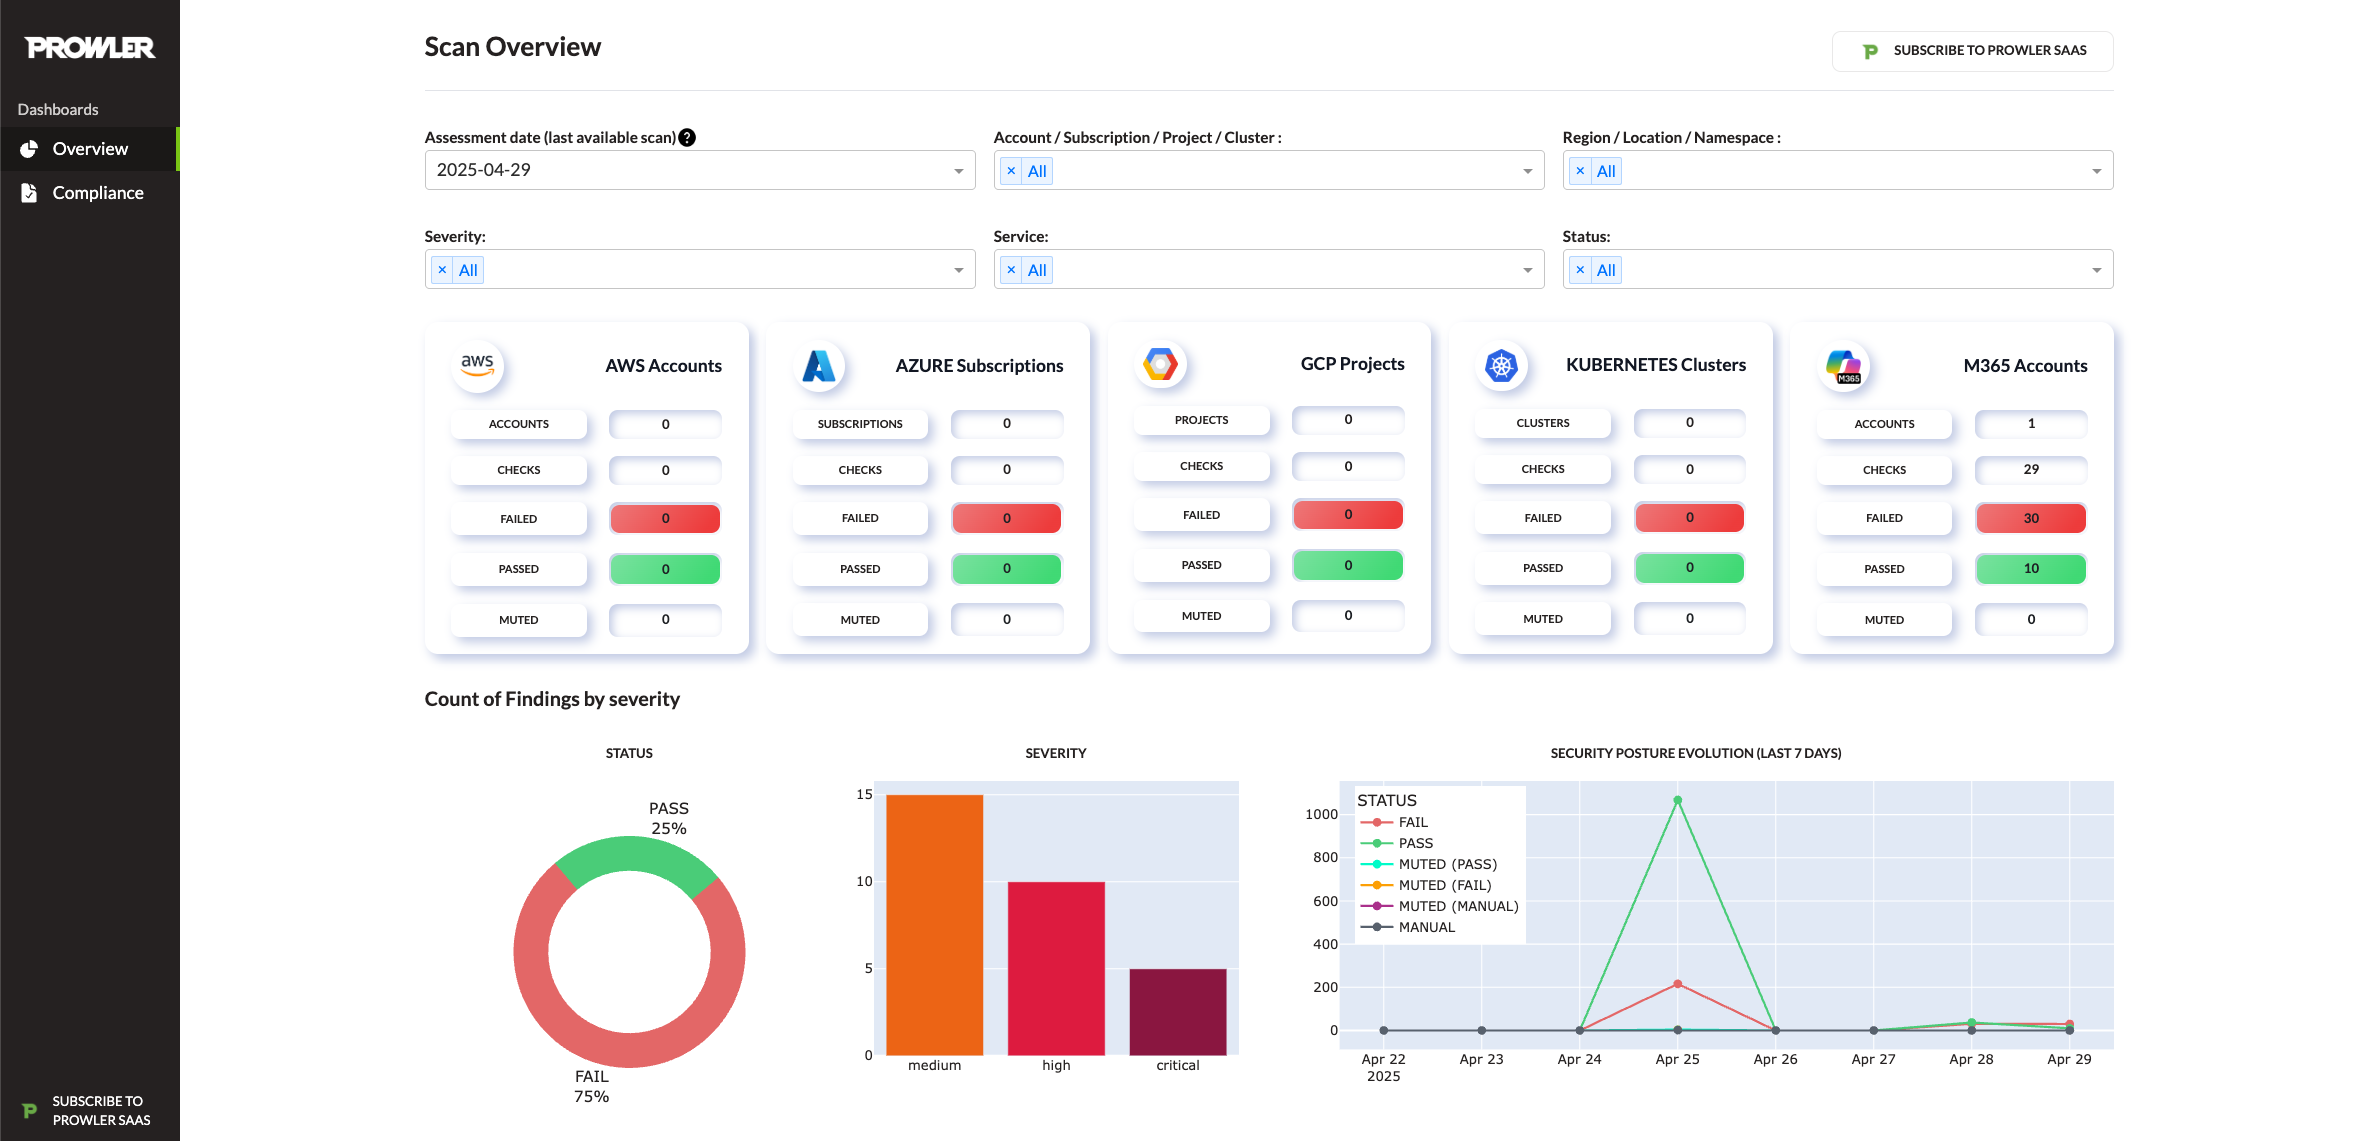
Attack Paths
Attack Paths automatically extends every completed AWS scan with a graph that combines Cartography's cloud inventory with Prowler findings. The feature runs in the API worker after each scan.
Two graph backends are supported as the long-lived sink:
- Neo4j (default; the Docker Compose files already ship a
neo4jservice). - Amazon Neptune (cloud-managed; opt-in).
Select the sink with ATTACK_PATHS_SINK_DATABASE (neo4j or neptune; default neo4j).
Note: Cartography ingestion always uses a temporary Neo4j database, regardless of the configured sink. The
NEO4J_*variables below must remain set even whenATTACK_PATHS_SINK_DATABASE=neptune.
Neo4j sink
| Variable | Description | Default |
|---|---|---|
NEO4J_HOST | Hostname used by the API containers. | neo4j |
NEO4J_PORT | Bolt port exposed by Neo4j. | 7687 |
NEO4J_USER / NEO4J_PASSWORD | Credentials with rights to create per-tenant databases. | neo4j / neo4j_password |
Neptune sink
| Variable | Description | Default |
|---|---|---|
NEPTUNE_WRITER_ENDPOINT | Bolt host for the Neptune writer instance. Required when sink is neptune. | empty |
NEPTUNE_READER_ENDPOINT | Optional reader endpoint for read-only queries. Falls back to the writer when unset. | empty |
NEPTUNE_PORT | Bolt port exposed by Neptune. | 8182 |
AWS_REGION | Region the Neptune cluster lives in. Required when sink is neptune. | empty |
Neptune authenticates with SigV4 using the standard boto3 credential chain. The worker's IAM role (or AWS_ACCESS_KEY_ID / AWS_SECRET_ACCESS_KEY) supplies the credentials. There is no Neptune password variable.
Every AWS provider scan will enqueue an Attack Paths ingestion job automatically. Other cloud providers will be added in future iterations.
Prowler at a Glance
[!Tip] For the most accurate and up-to-date information about checks, services, frameworks, and categories, visit Prowler Hub.
| Provider | Checks | Services | Compliance Frameworks | Categories | Support | Interface |
|---|---|---|---|---|---|---|
| AWS | 662 | 86 | 50 | 19 | Official | UI, API, CLI |
| Azure | 191 | 22 | 25 | 16 | Official | UI, API, CLI |
| GCP | 110 | 20 | 22 | 12 | Official | UI, API, CLI |
| Kubernetes | 92 | 7 | 11 | 11 | Official | UI, API, CLI |
| GitHub | 24 | 3 | 2 | 5 | Official | UI, API, CLI |
| M365 | 144 | 10 | 9 | 10 | Official | UI, API, CLI |
| OCI | 52 | 14 | 5 | 10 | Official | UI, API, CLI |
| Alibaba Cloud | 63 | 9 | 6 | 9 | Official | UI, API, CLI |
| Cloudflare | 43 | 5 | 3 | 9 | Official | UI, API, CLI |
| IaC | See trivy docs. | N/A | N/A | N/A | Official | UI, API, CLI |
| MongoDB Atlas | 10 | 3 | 1 | 8 | Official | UI, API, CLI |
| LLM | See promptfoo docs. | N/A | N/A | N/A | Official | CLI |
| Image | N/A | N/A | N/A | N/A | Official | UI, API, CLI |
| Google Workspace | 65 | 11 | 4 | 6 | Official | UI, API, CLI |
| OpenStack | 34 | 5 | 1 | 9 | Official | UI, API, CLI |
| Vercel | 26 | 6 | 1 | 8 | Official | UI, API, CLI |
| Okta | 29 | 8 | 2 | 2 | Official | UI, API, CLI |
| Linode Contact us | 10 | 3 | 1 | 4 | Unofficial | CLI |
| Huawei Cloud Contact us | 25 | 10 | 1 | 6 | Unofficial | CLI |
| E2E Networks Contact us | 27 | 6 | 0 | 2 | Unofficial | CLI |
| Scaleway Contact us | 1 | 1 | 1 | 1 | Unofficial | CLI |
| StackIT Contact us | 8 | 2 | 1 | 3 | Unofficial | CLI |
| NHN | 6 | 2 | 2 | 0 | Unofficial | CLI |
[!Note] The numbers in the table are updated periodically.
[!Note] Use the following commands to list Prowler's available checks, services, compliance frameworks, and categories:
prowler <provider> --list-checksprowler <provider> --list-servicesprowler <provider> --list-complianceprowler <provider> --list-categories
💻 Installation
Prowler Local Server
Prowler Local Server offers flexible installation methods tailored to various environments:
For detailed instructions on using Prowler Local Server, refer to the usage guide.
Docker Compose
Requirements
Docker Composeinstalled: https://docs.docker.com/compose/install/.
Commands
macOS/Linux:
VERSION=$(curl -s https://api.github.com/repos/prowler-cloud/prowler/releases/latest | jq -r .tag_name)
curl -sLO "https://raw.githubusercontent.com/prowler-cloud/prowler/refs/tags/${VERSION}/docker-compose.yml"
# Environment variables can be customized in the .env file. Using default values in production environments is not recommended.
curl -sLO "https://raw.githubusercontent.com/prowler-cloud/prowler/refs/tags/${VERSION}/.env"
docker compose up -d
Windows PowerShell:
$VERSION = (Invoke-RestMethod -Uri "https://api.github.com/repos/prowler-cloud/prowler/releases/latest").tag_name
Invoke-WebRequest -Uri "https://raw.githubusercontent.com/prowler-cloud/prowler/refs/tags/$VERSION/docker-compose.yml" -OutFile "docker-compose.yml"
# Environment variables can be customized in the .env file. Using default values in production environments is not recommended.
Invoke-WebRequest -Uri "https://raw.githubusercontent.com/prowler-cloud/prowler/refs/tags/$VERSION/.env" -OutFile ".env"
docker compose up -d
Warning
Stats
15,220
Stars
2,491
Forks
Active
Maintenance
Python
Language
Apache-2.0
License
Last commit
Created

Ships withprowler
Prowler is the world’s most widely used Open-Source Cloud Security Platform that automates security and compliance across any cloud environment.
15k39 skills1 MCP
Stars on GitHub
Momentum
- stars in total
- 15.2k
More MCP servers from other plugins.

serena
MCPGives coding agents semantic code search and editing through language server integration, IDE style codebase navigation.
 @trailofbitsInstall MCP
agt_governance
MCPShips with agent-governance-toolkit: AI Agent Governance Toolkit — Policy enforcement, zero-trust identity, execution sandboxing,…
 @microsoftInstall MCP
bounty-platforms
MCPShips with pentest-agents: Bug bounty agent framework for Claude Code, Codex, Gemini, Cursor, Windsurf, Copilot, and OpenClaw —…
 @h-mmerInstall MCP
Questions about prowler.
- Which coding agents can use prowler?
- prowler works in any agent that reads an MCP config file: Claude Code, Codex, Cursor, Gemini CLI, GitHub Copilot, OpenCode and Windsurf. Each agent reads it from its own file; this page names the file for each one.
- How do I add prowler to Claude Code?
- Run these in order, one at a time. 1. In Claude Code: /plugin marketplace add prowler-cloud/prowler 2. In Claude Code: /plugin install prowler@prowler-plugins
- Is prowler safe to install?
- Low risk. Signals from public registries, not an audit.