


rea
Reverse engineer anything with agents, from app behavior down to native binaries.
420k
 @morluto
Prowler is an open-source cloud security platform for scanning cloud accounts and automating security and compliance checks. It includes skills for framework compliance triage, Django REST and Vercel AI SDK patterns, and GitHub agentic workflows.
Claude Code
> /plugin marketplace add prowler-cloud/prowler> /plugin install prowler@prowler-plugins
Codex
$ npx skills add prowler-cloud/prowler -a codex
Cursor
$ npx skills add prowler-cloud/prowler -a cursor
Gemini CLI
$ npx skills add prowler-cloud/prowler -a gemini-cli
GitHub Copilot
$ copilot plugin marketplace add prowler-cloud/prowler$ copilot plugin install prowler@prowler-plugins
OpenCode
$ npx skills add prowler-cloud/prowler -a opencode
Windsurf
$ npx skills add prowler-cloud/prowler -a windsurf
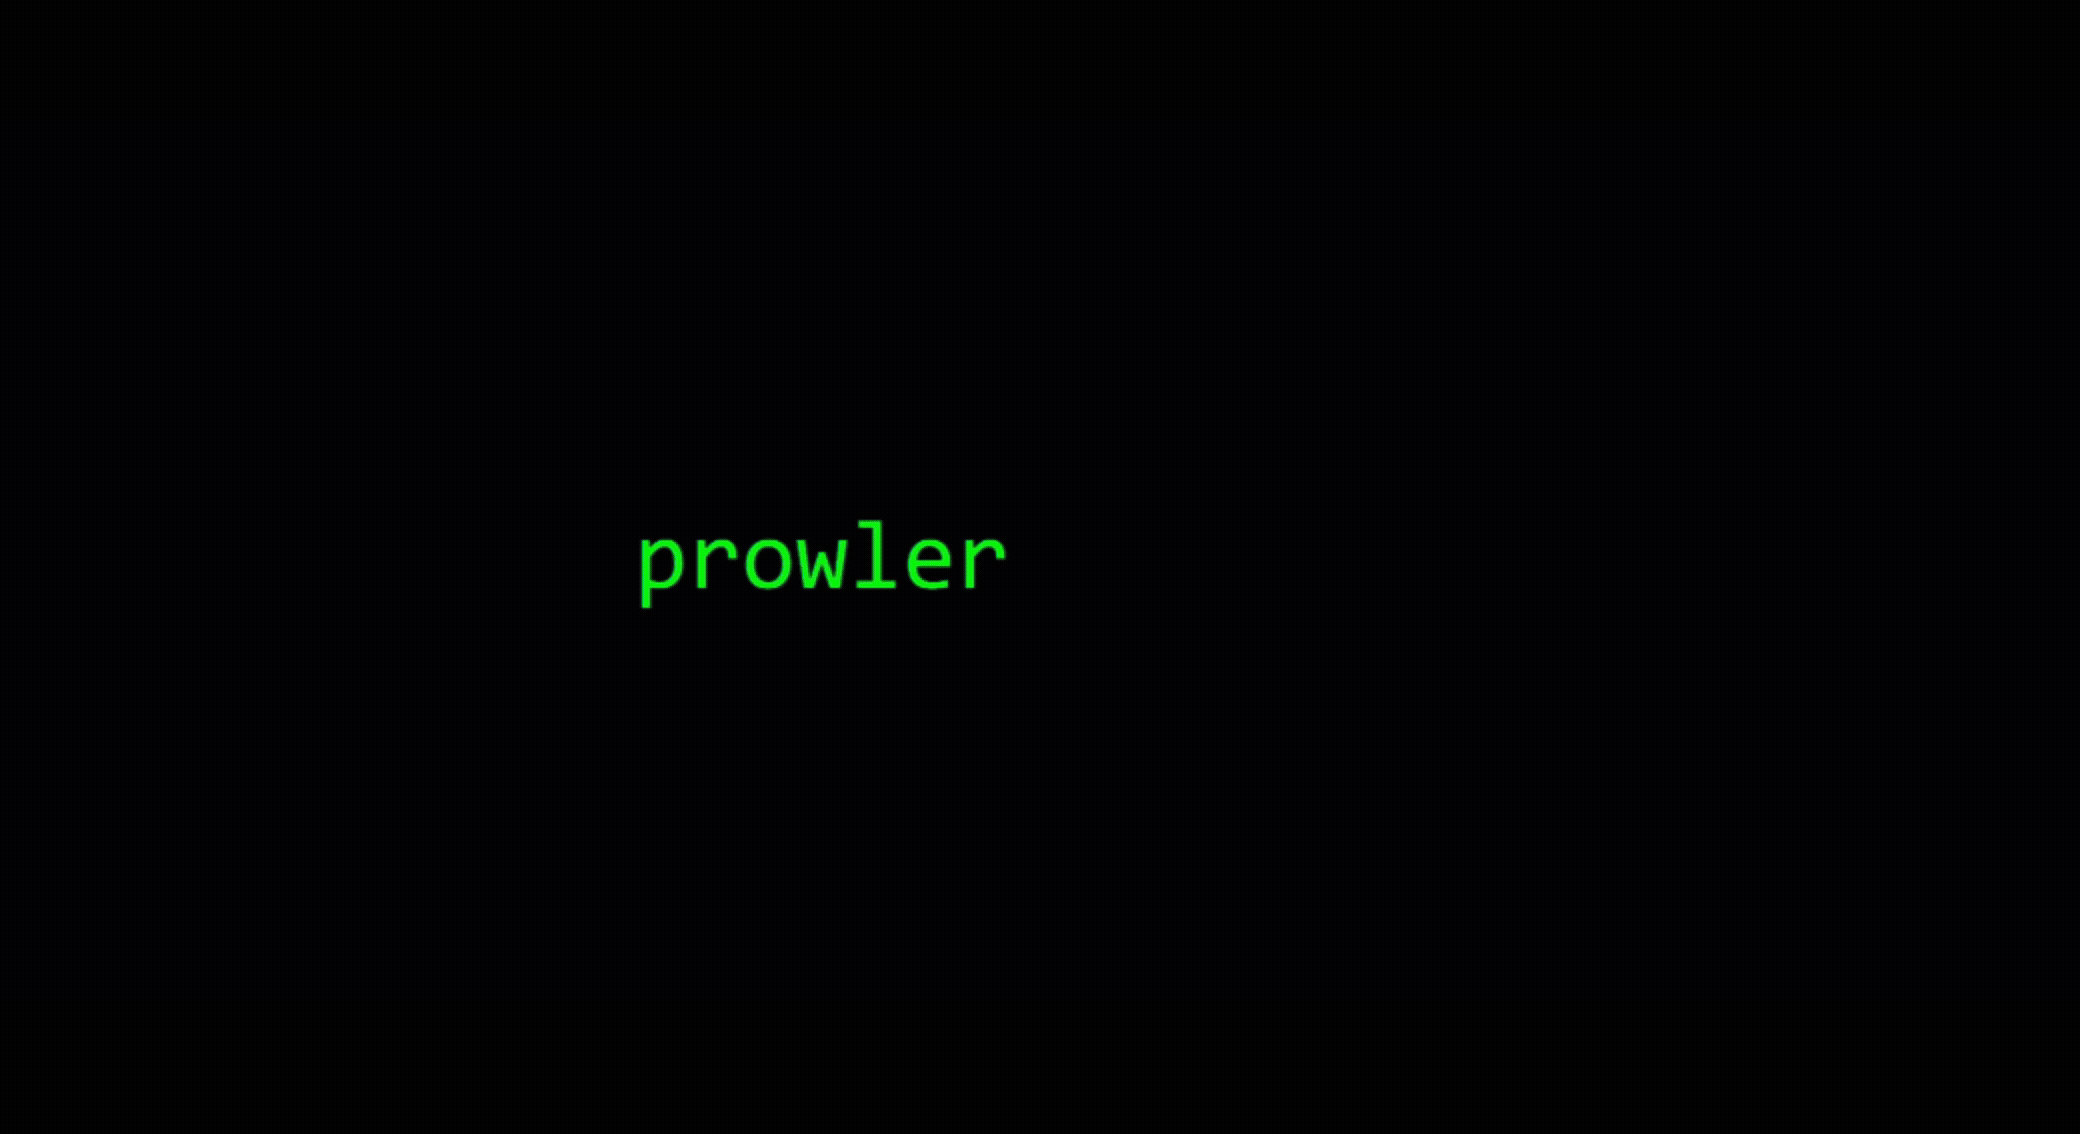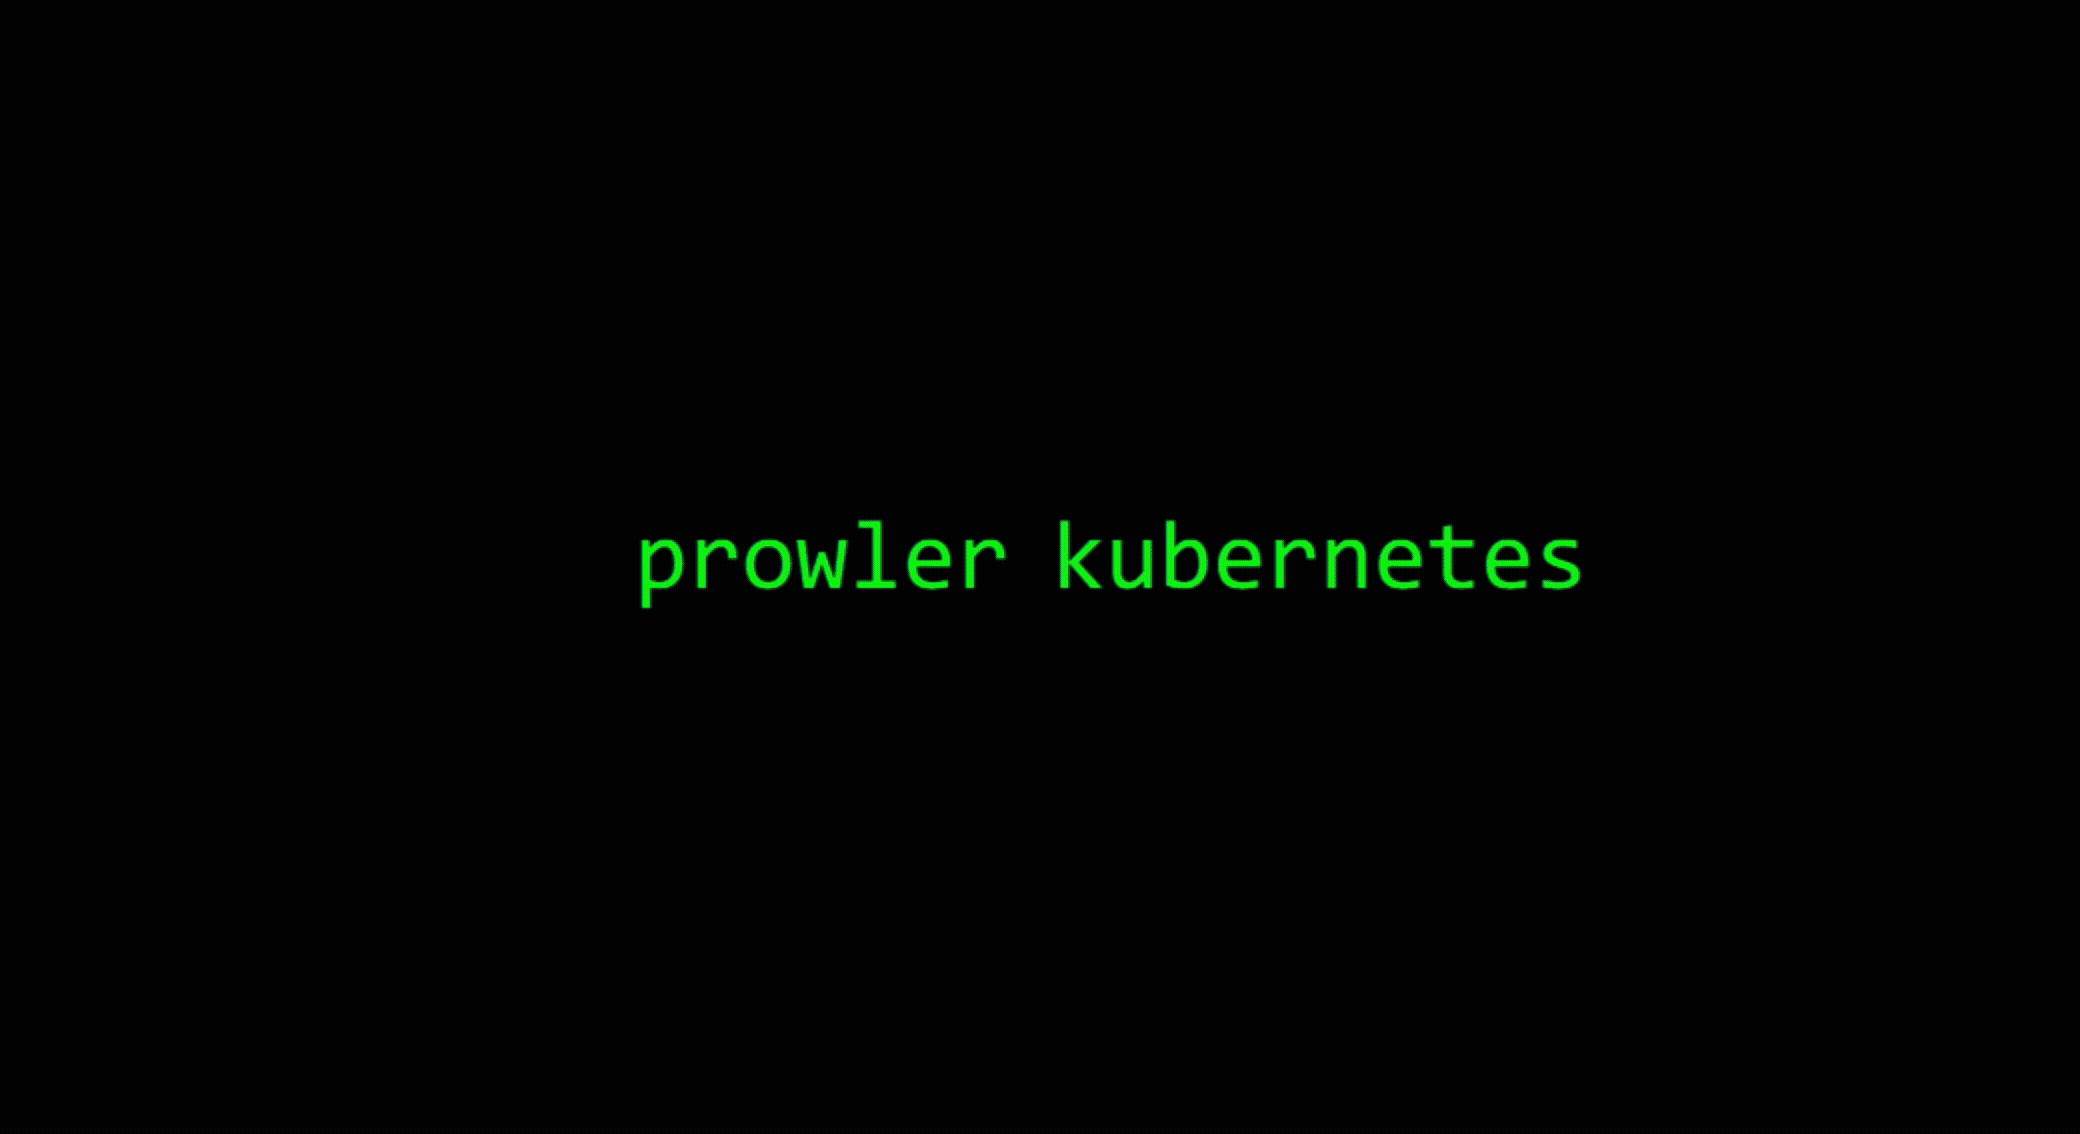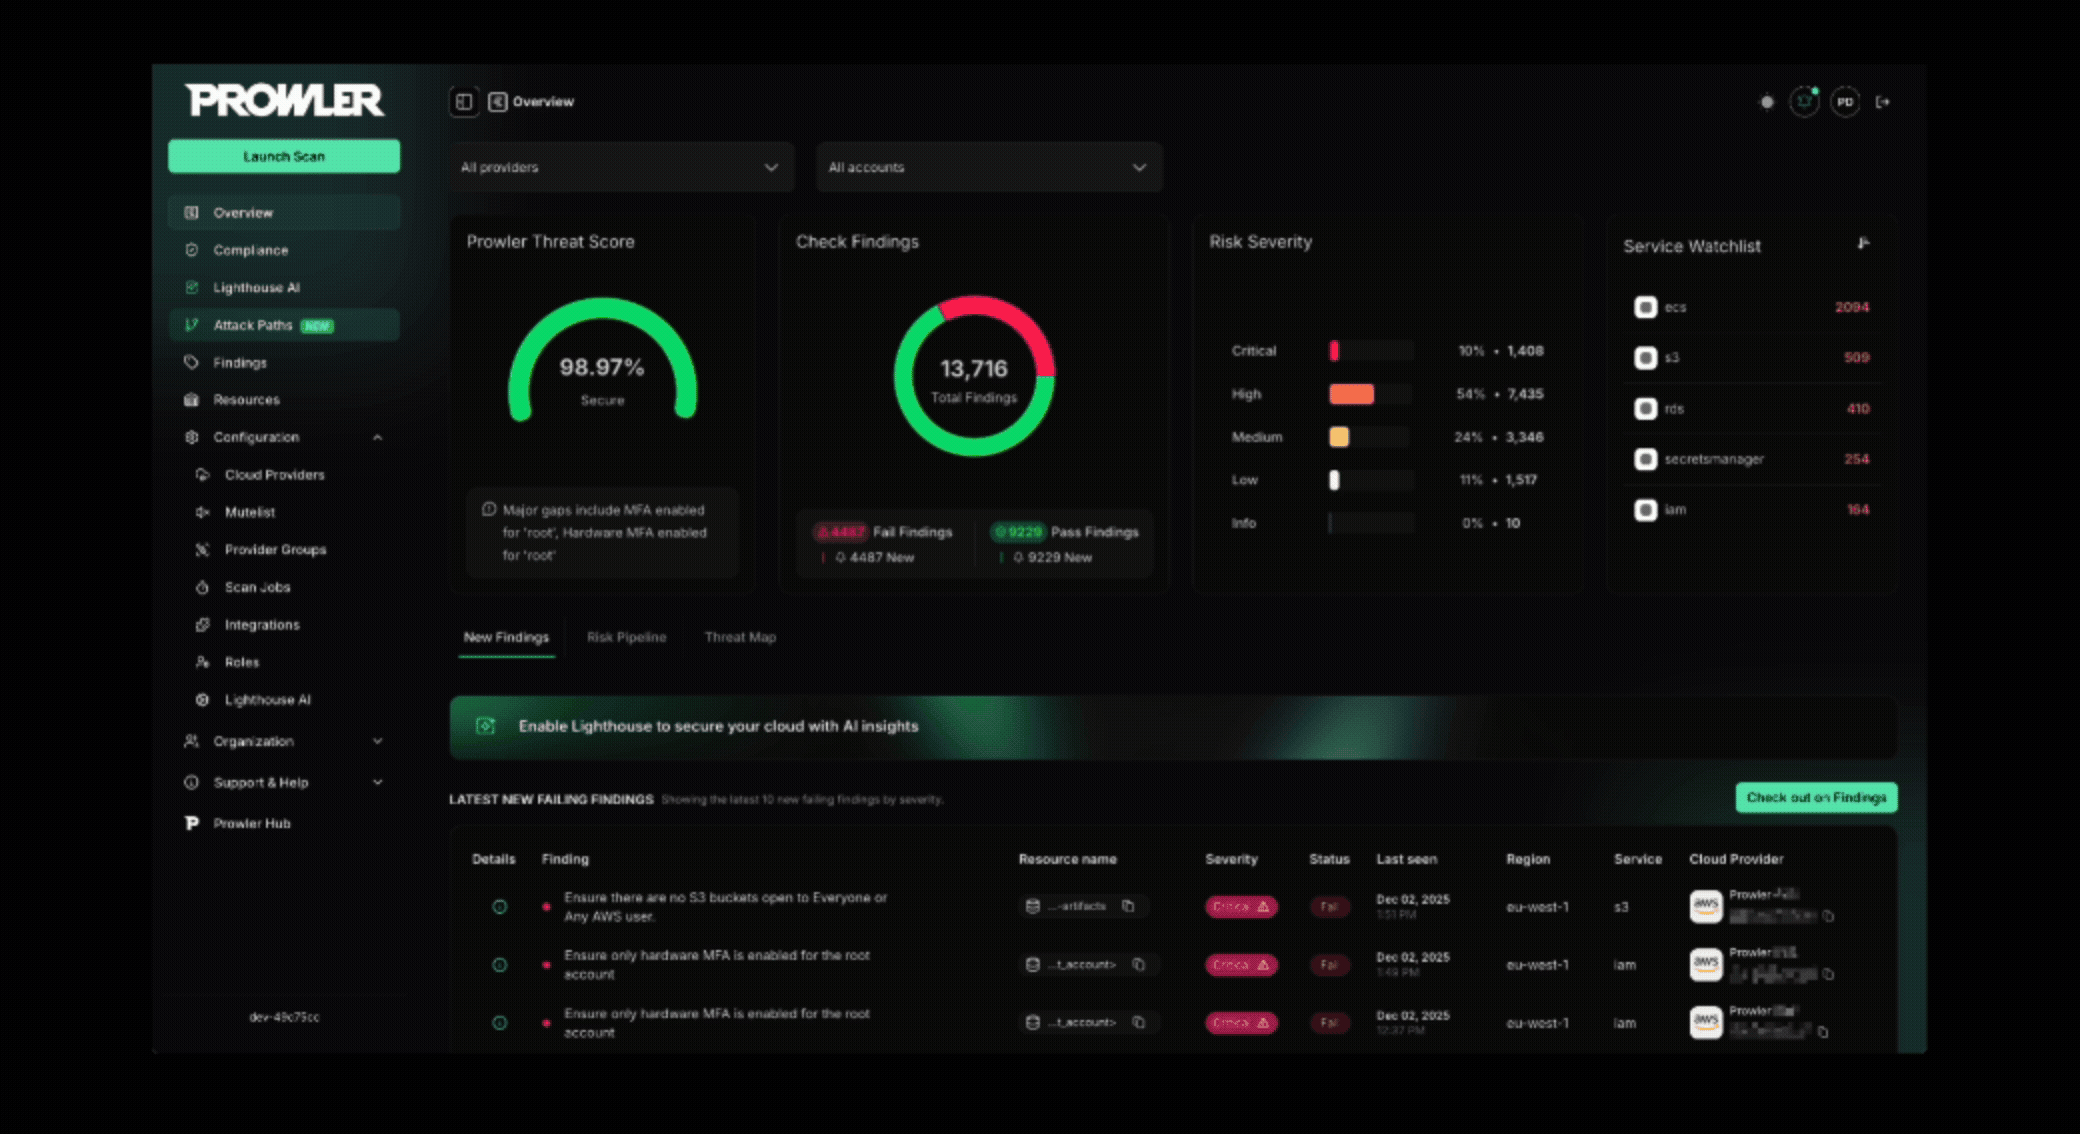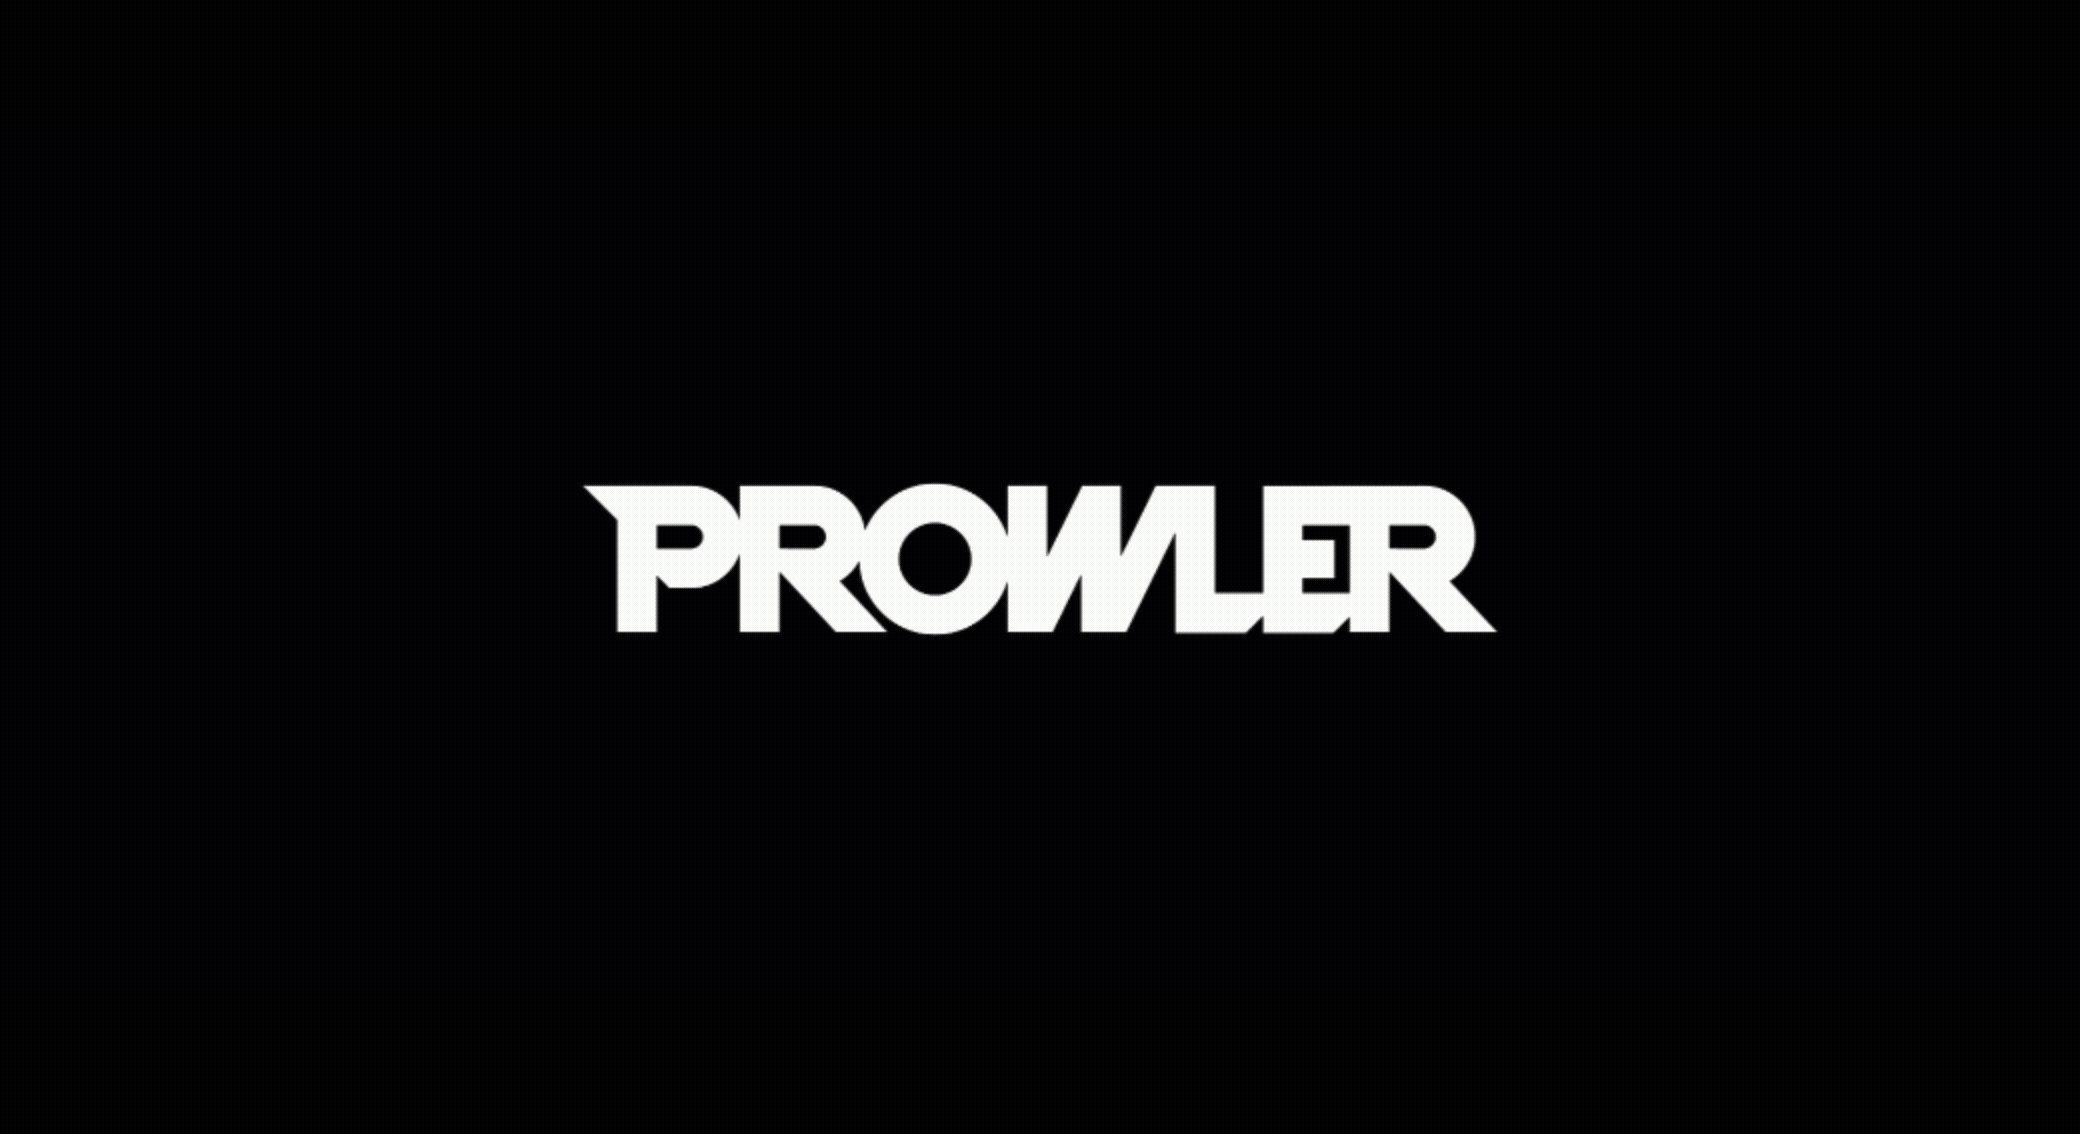
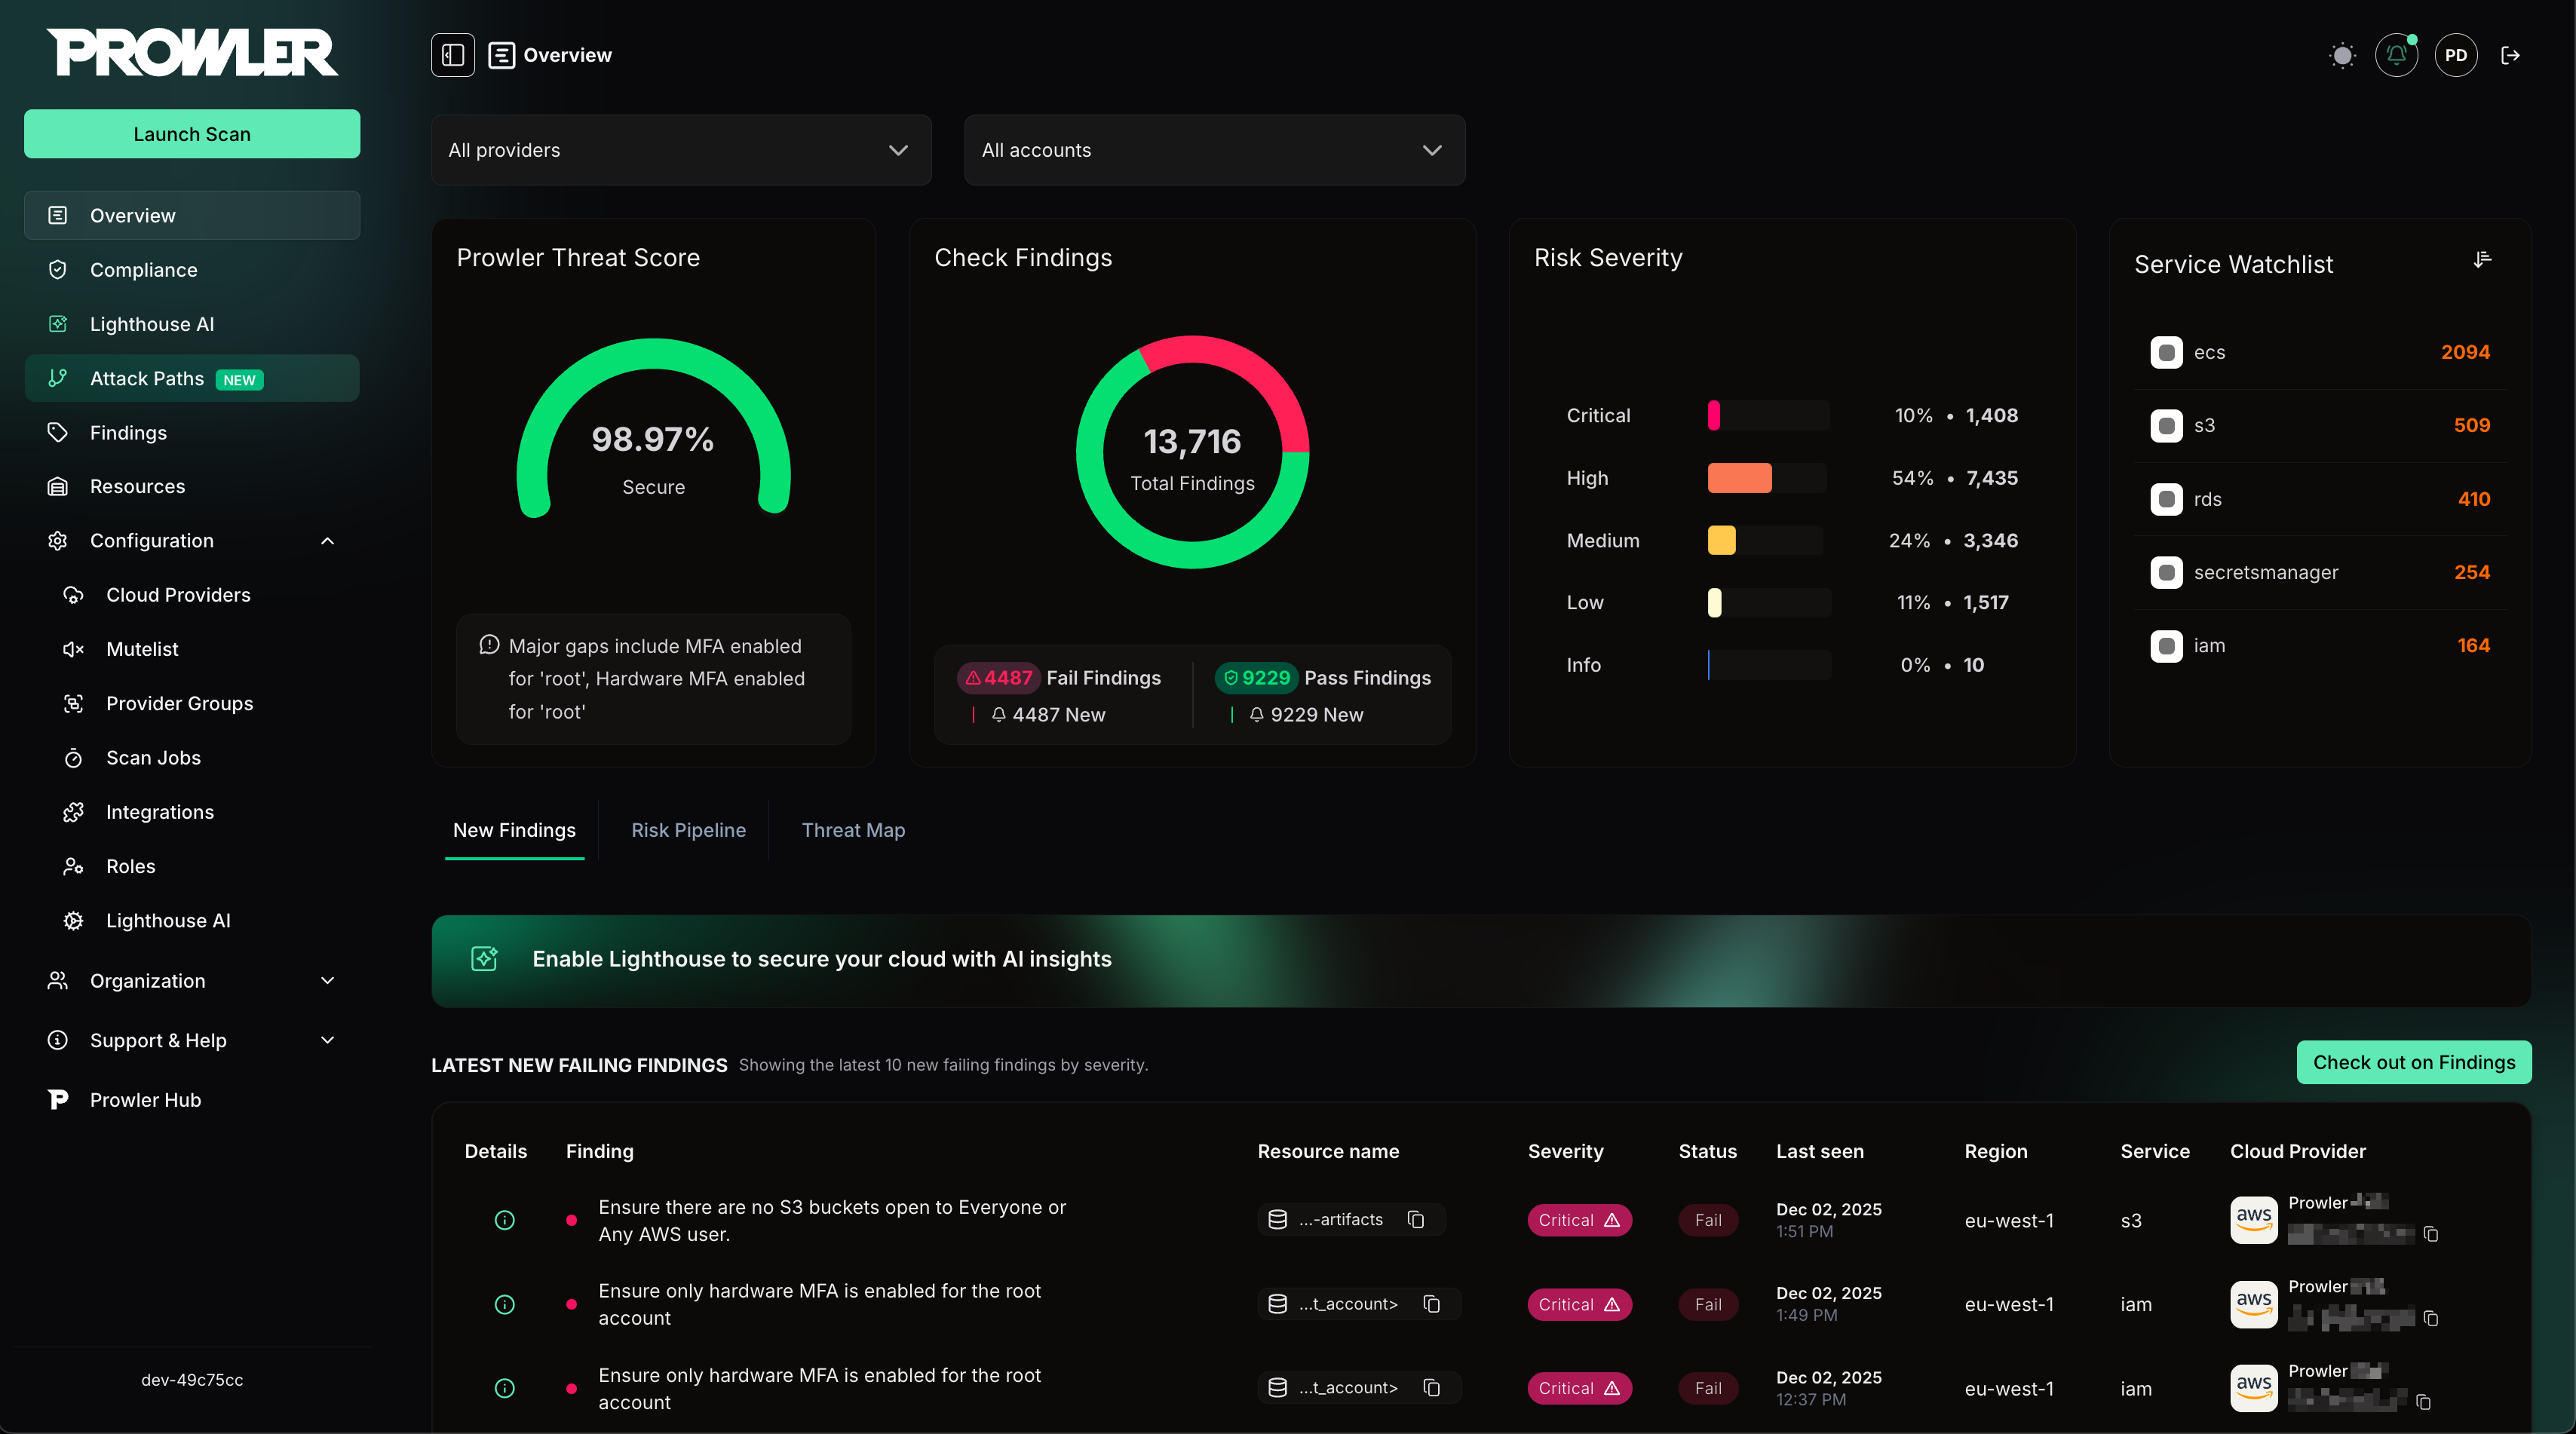
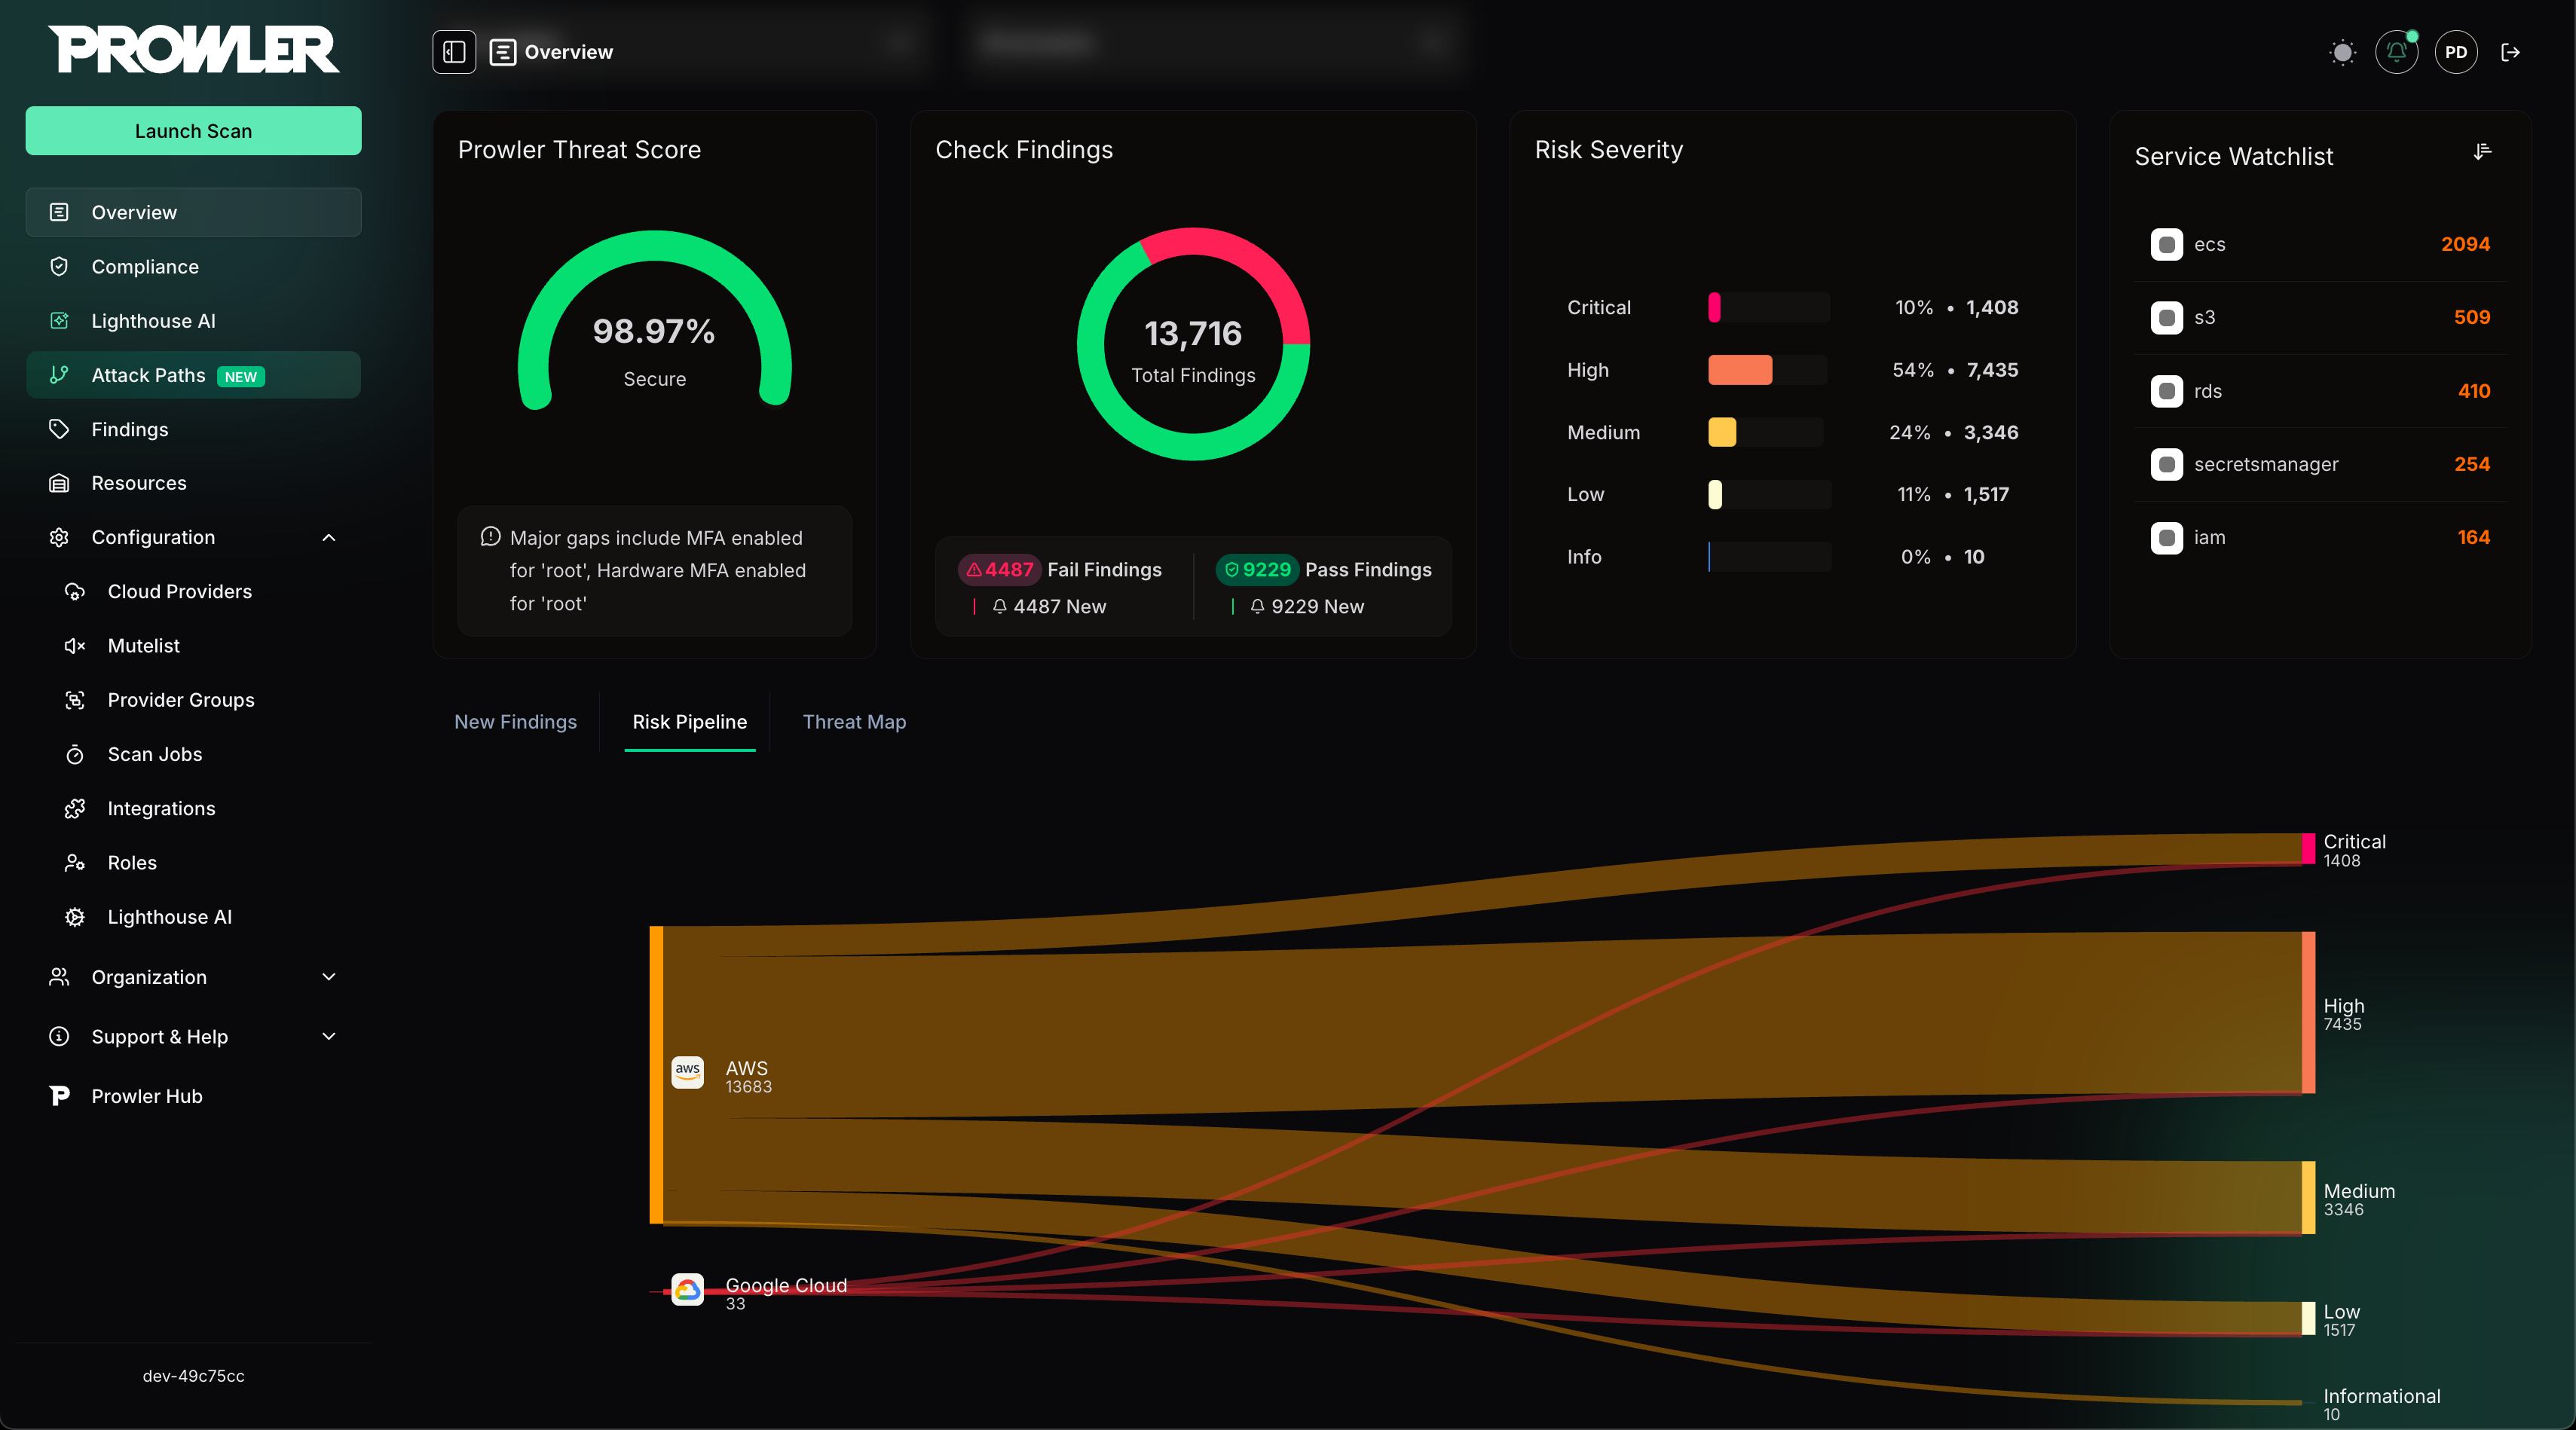


Prowler is the Open Cloud Security Platform trusted by thousands to automate security and compliance in any cloud environment. With thousands of ready-to-use checks and compliance frameworks, Prowler delivers real-time, customizable monitoring and seamless integrations, making cloud security simple, scalable, and cost-effective for organizations of any size.
The Agentic Cloud Defender
Try Prowler Cloud
Join our Prowler community!



Prowler is the world’s most widely used Open-Source Cloud Security Platform that automates security and compliance across any cloud environment. With thousands of ready-to-use security checks, remediation guidance, and compliance frameworks, Prowler is built to “Secure ANY Cloud at AI Speed”. Prowler delivers AI-driven, customizable, and easy-to-use assessments, dashboards, reports, and integrations, making cloud security simple, scalable, and cost-effective for organizations of any size.
Prowler includes hundreds of built-in controls to ensure compliance with standards and frameworks, including:
Prowler Cloud and Prowler Local Server, its self-hosted open-source version, are web applications that simplify running Prowler across your cloud provider accounts. They provide a user-friendly interface to visualize the results and streamline your security assessments.
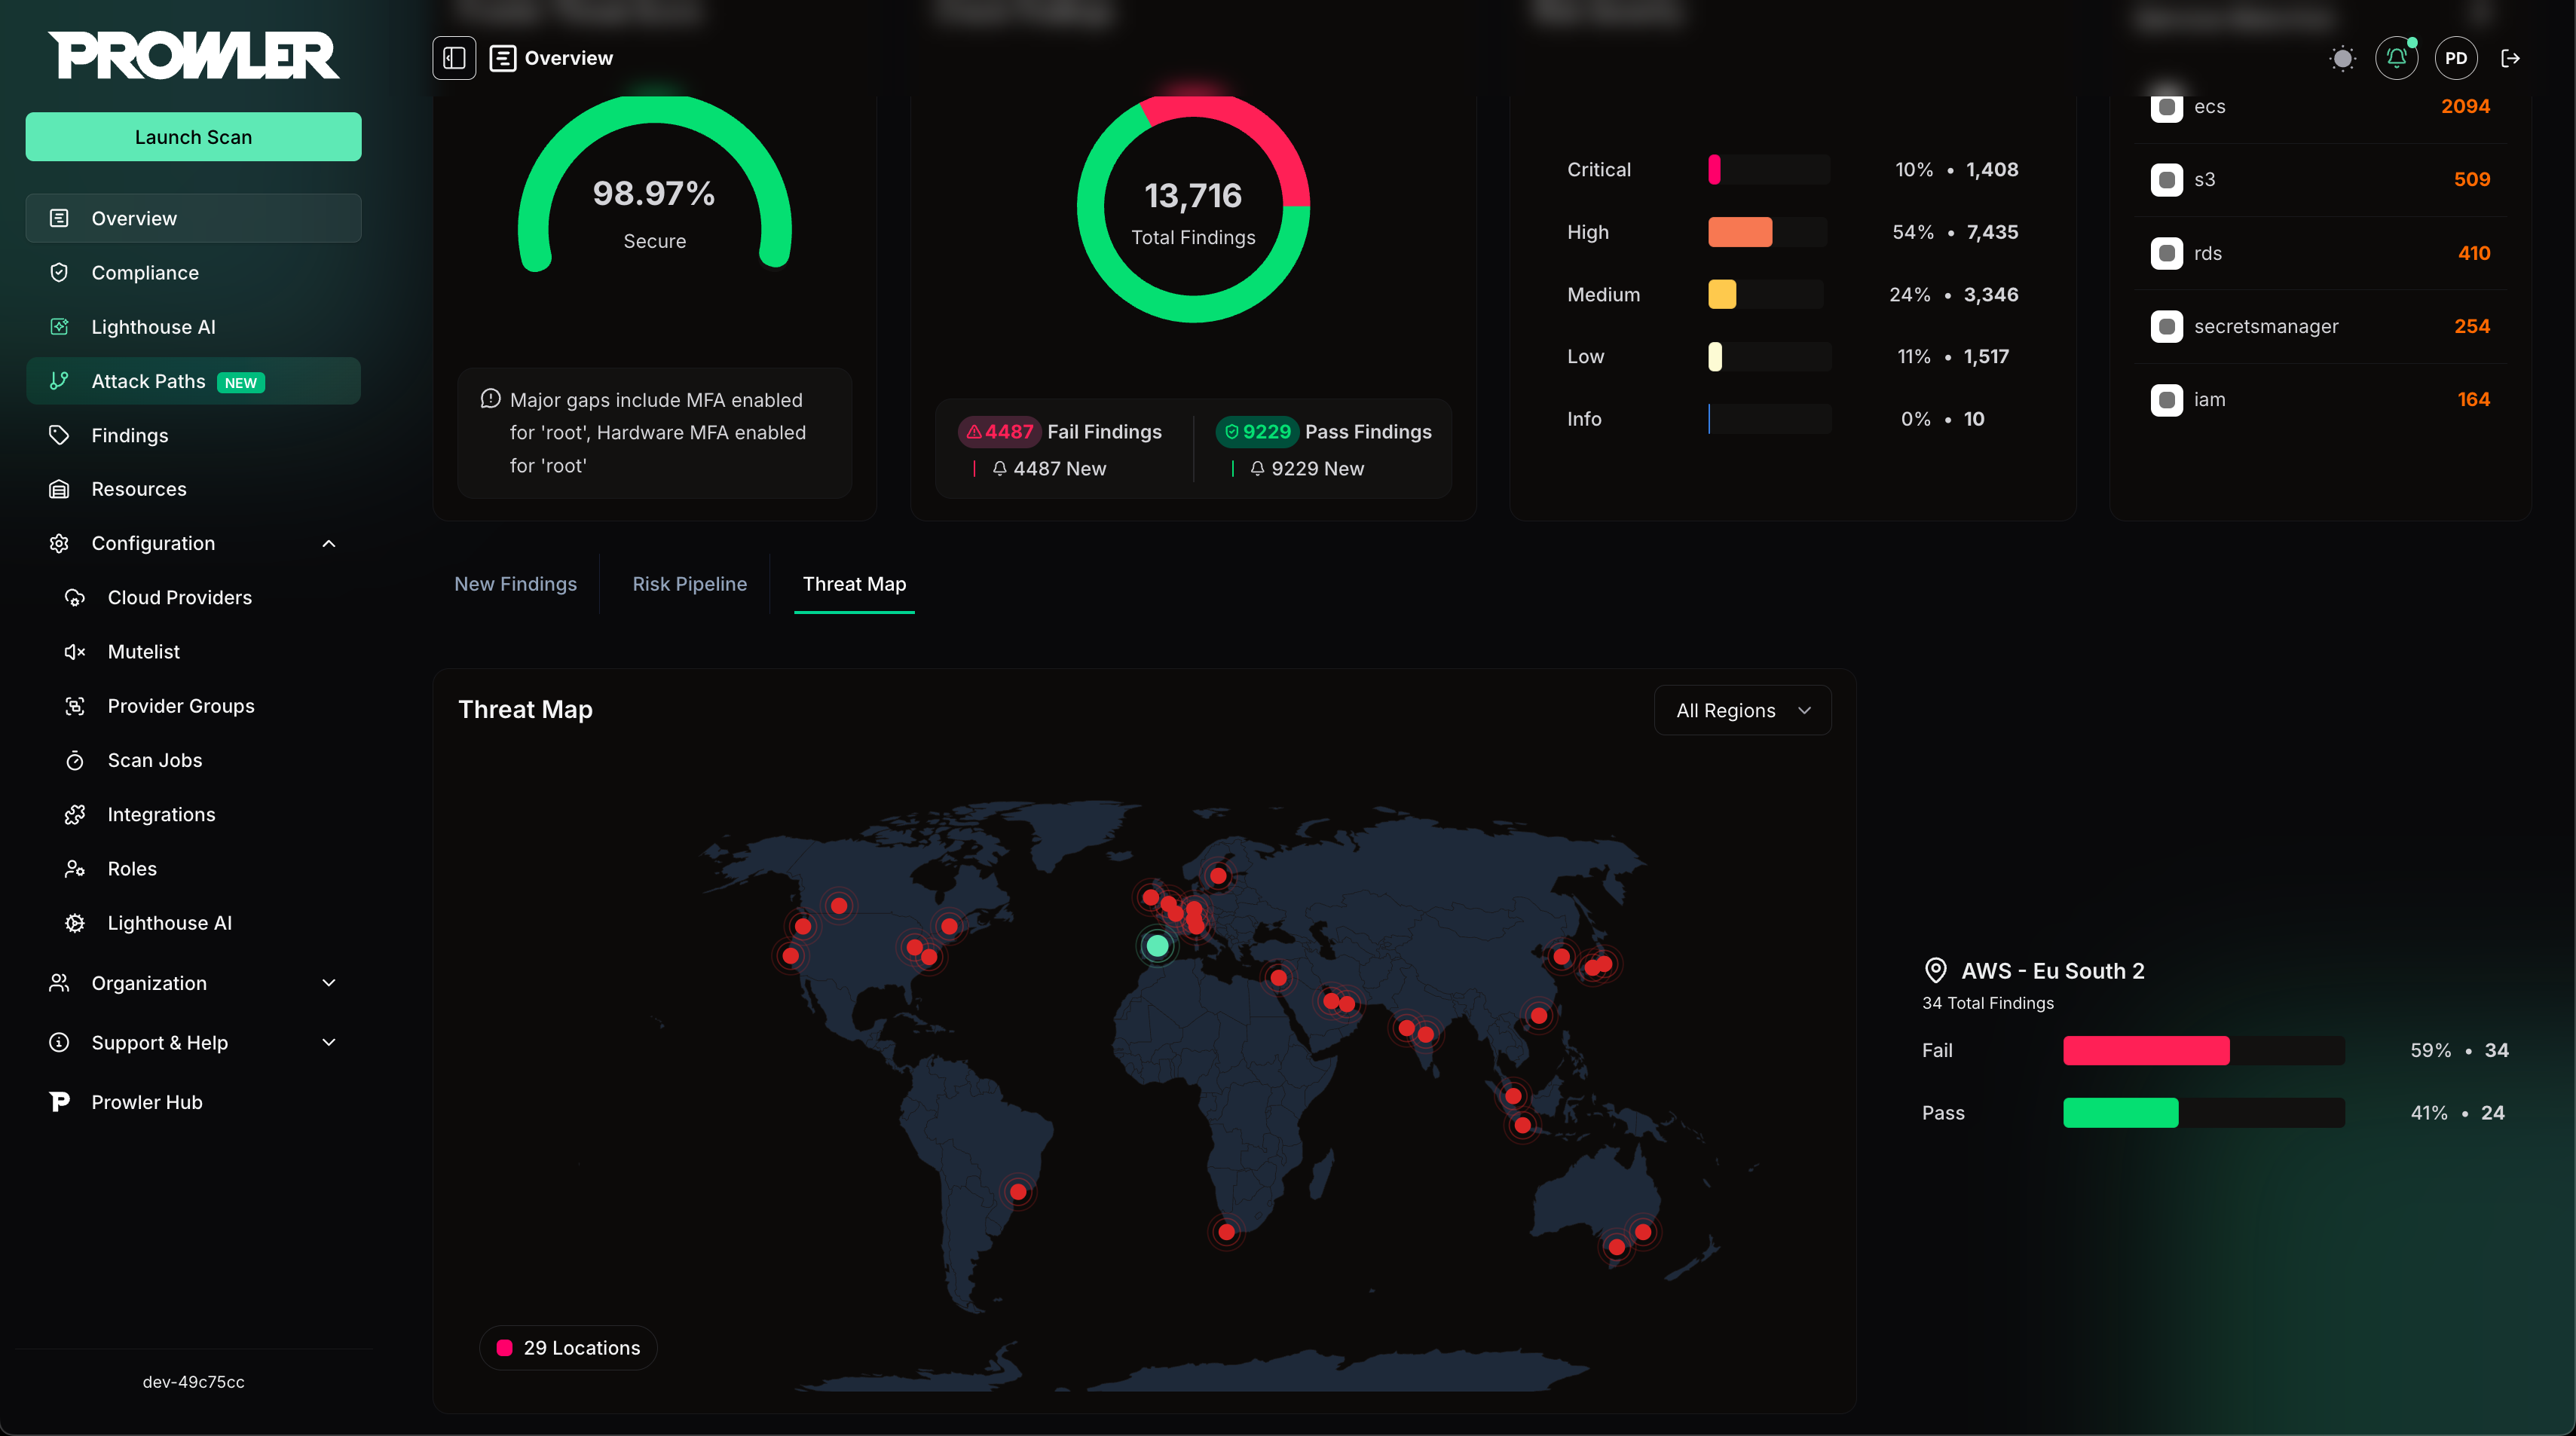
For more details, refer to the Prowler Local Server documentation
prowler <provider>
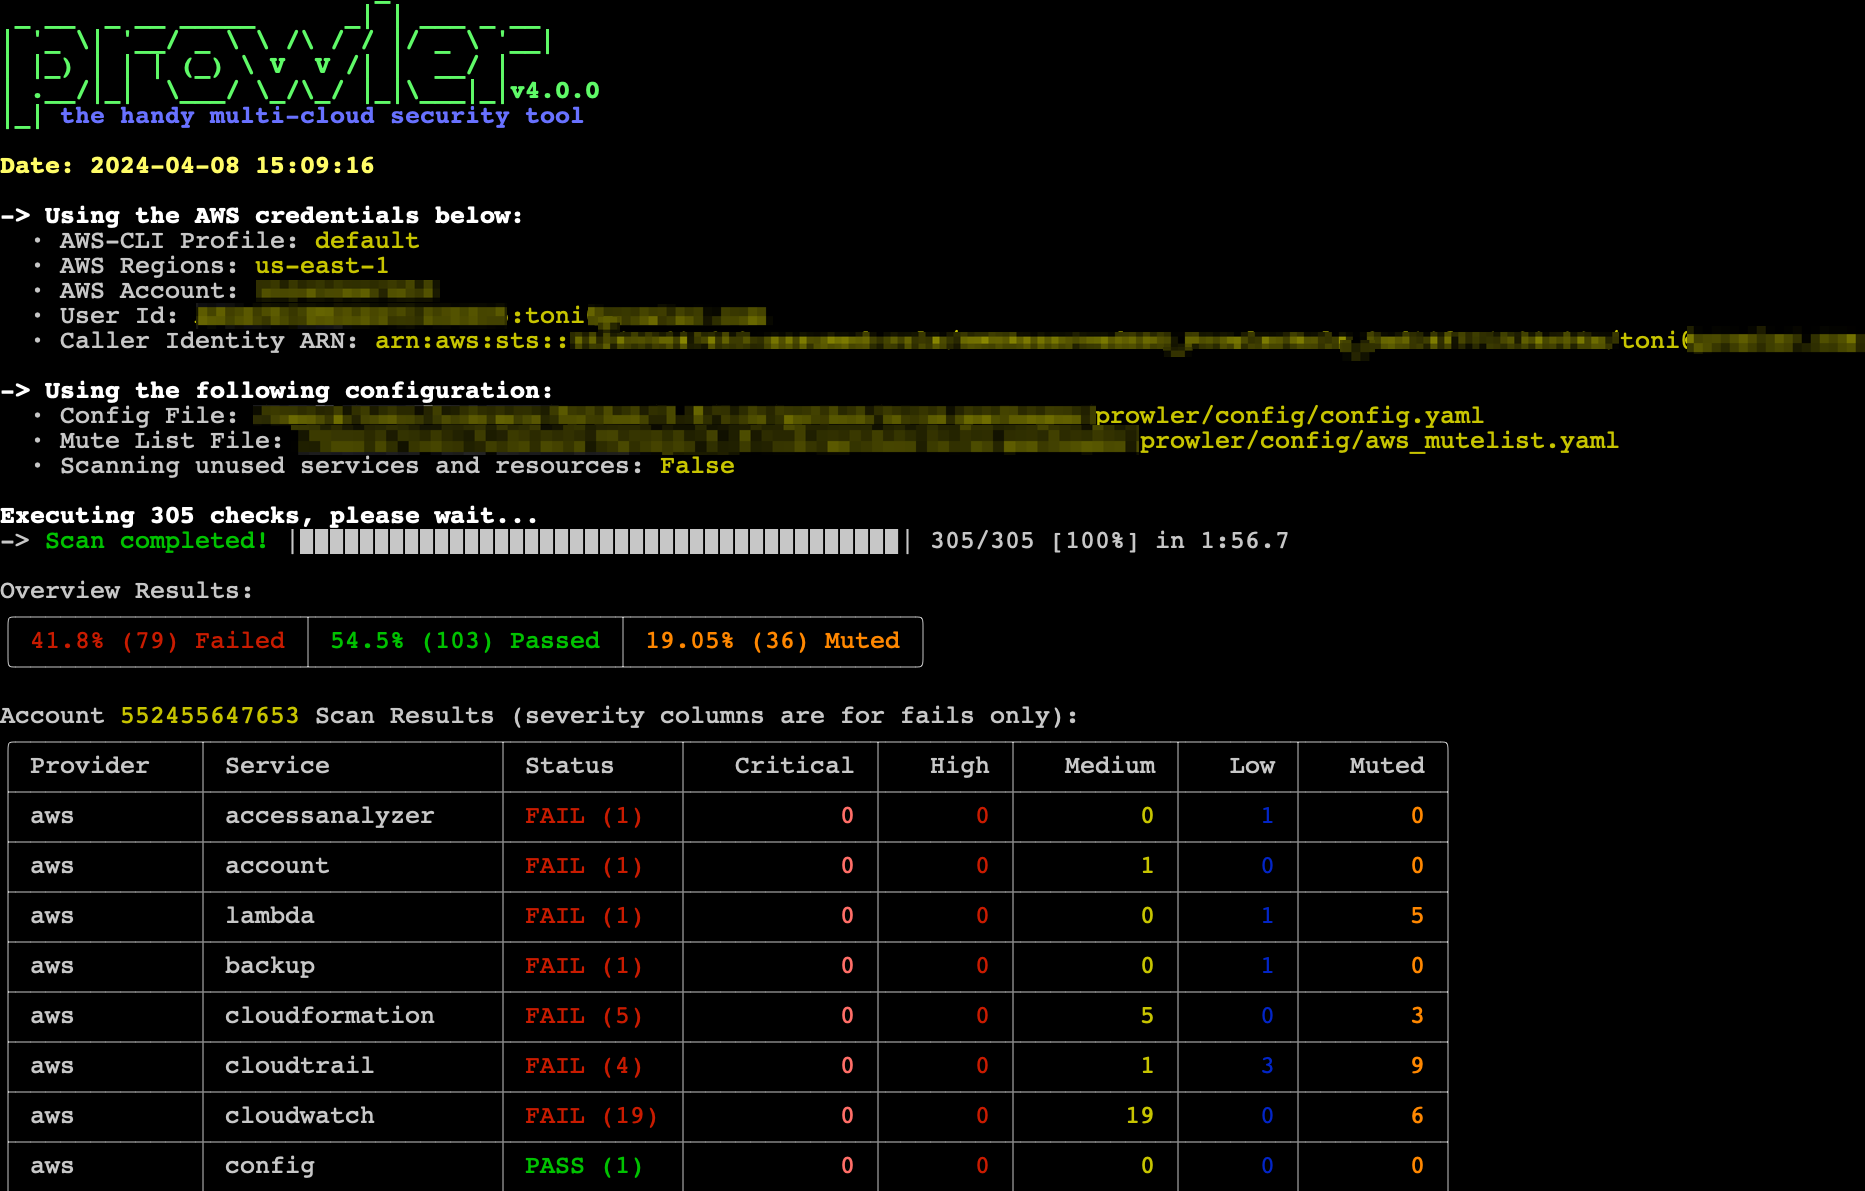
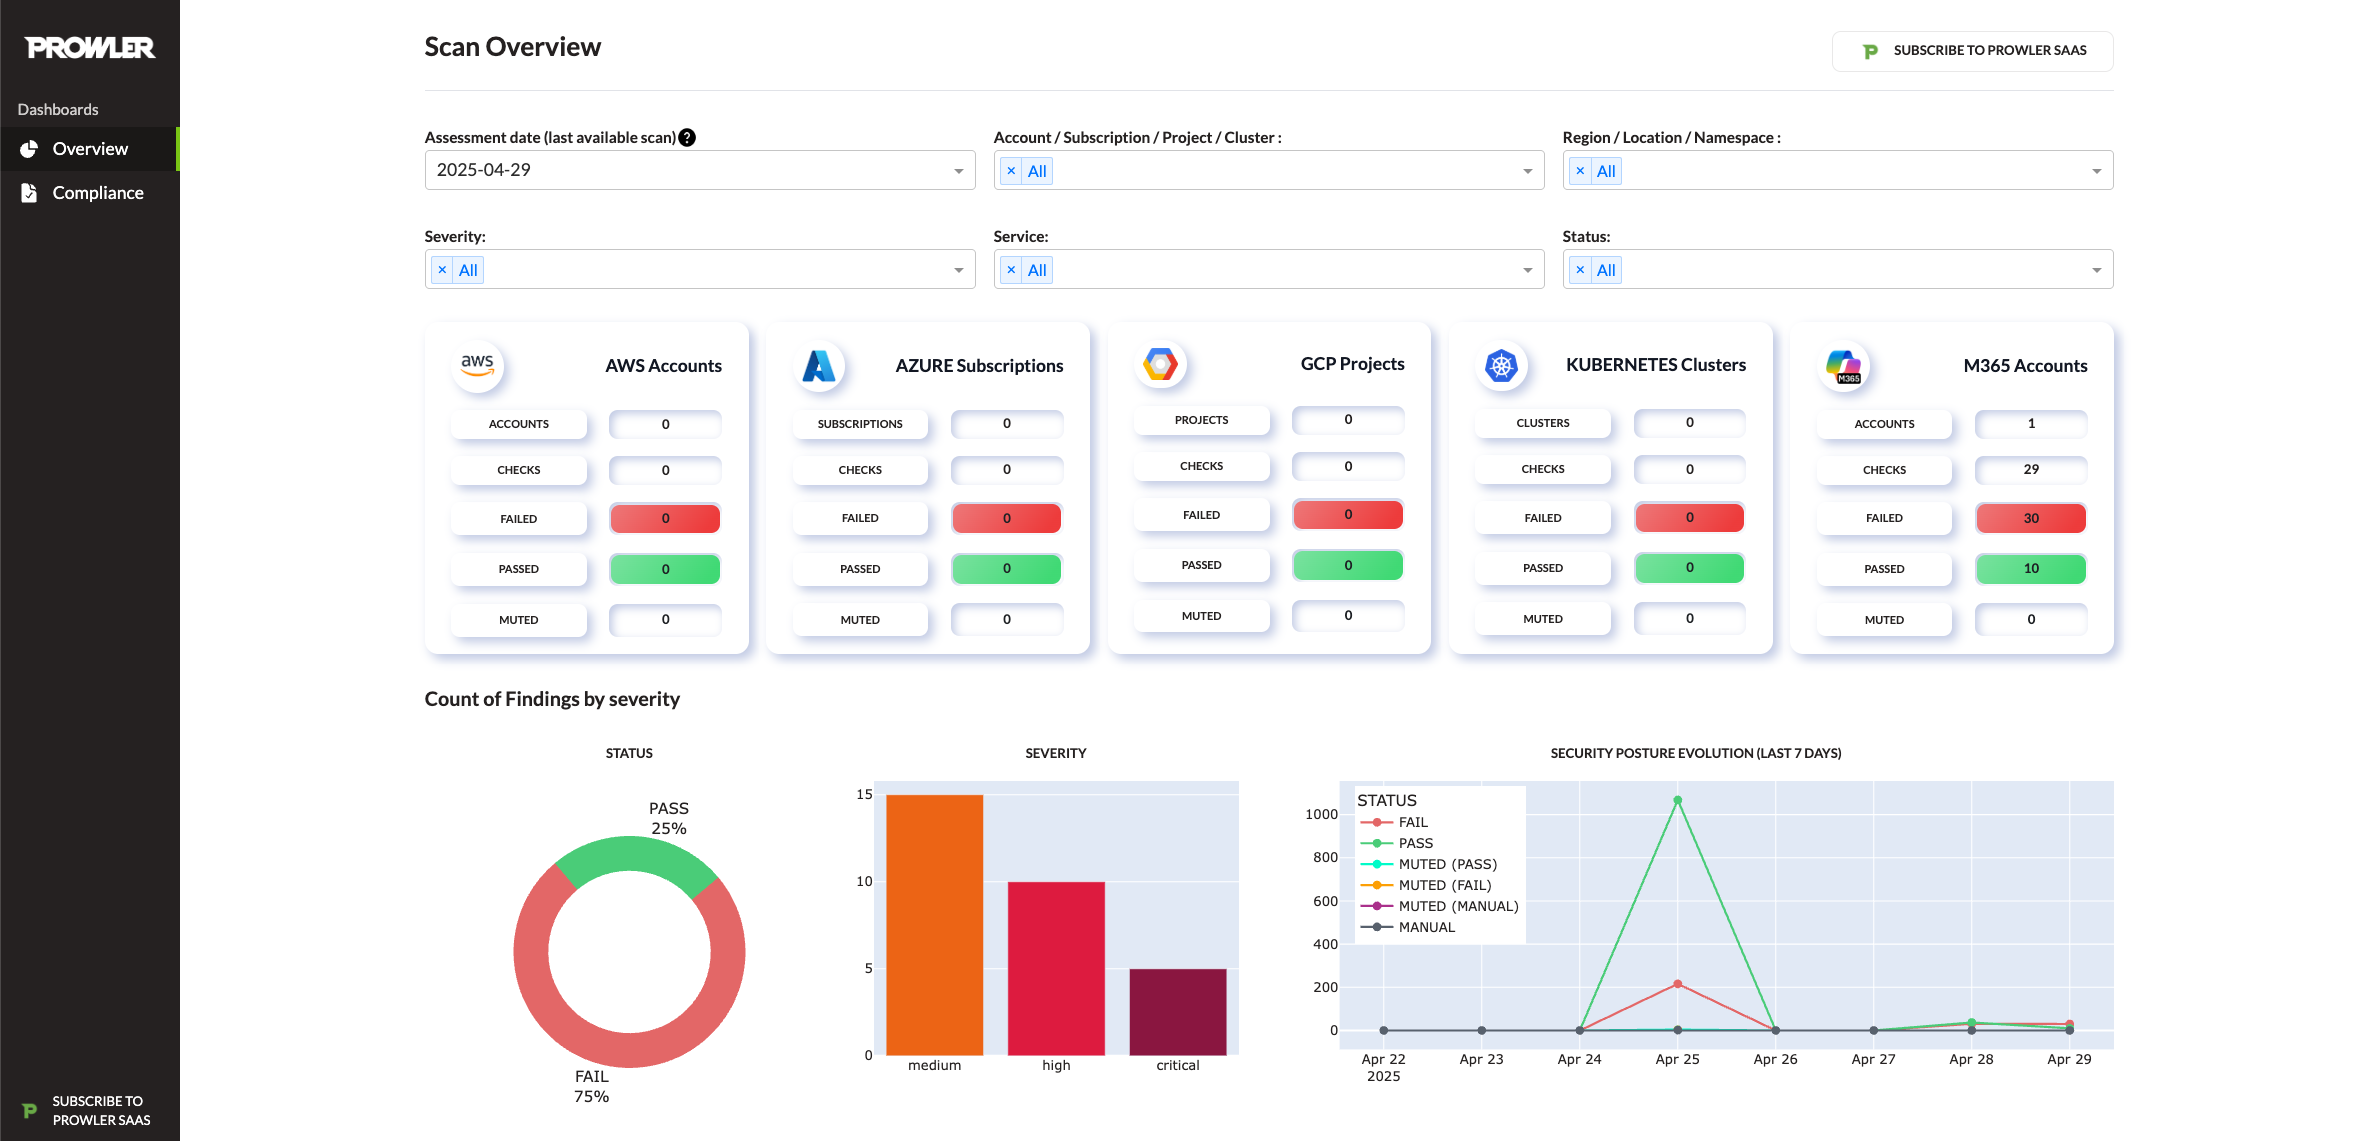
prowler dashboard
Attack Paths automatically extends every completed AWS scan with a graph that combines Cartography's cloud inventory with Prowler findings. The feature runs in the API worker after each scan.
Two graph backends are supported as the long-lived sink:
neo4j service).Select the sink with ATTACK_PATHS_SINK_DATABASE (neo4j or neptune; default neo4j).
Note: Cartography ingestion always uses a temporary Neo4j database, regardless of the configured sink. The
NEO4J_*variables below must remain set even whenATTACK_PATHS_SINK_DATABASE=neptune.
| Variable | Description | Default |
|---|---|---|
NEO4J_HOST | Hostname used by the API containers. | neo4j |
NEO4J_PORT | Bolt port exposed by Neo4j. | 7687 |
NEO4J_USER / NEO4J_PASSWORD | Credentials with rights to create per-tenant databases. | neo4j / neo4j_password |
| Variable | Description | Default |
|---|---|---|
NEPTUNE_WRITER_ENDPOINT | Bolt host for the Neptune writer instance. Required when sink is neptune. | empty |
NEPTUNE_READER_ENDPOINT | Optional reader endpoint for read-only queries. Falls back to the writer when unset. | empty |
NEPTUNE_PORT | Bolt port exposed by Neptune. | 8182 |
AWS_REGION | Region the Neptune cluster lives in. Required when sink is neptune. | empty |
Neptune authenticates with SigV4 using the standard boto3 credential chain. The worker's IAM role (or AWS_ACCESS_KEY_ID / AWS_SECRET_ACCESS_KEY) supplies the credentials. There is no Neptune password variable.
Every AWS provider scan will enqueue an Attack Paths ingestion job automatically. Other cloud providers will be added in future iterations.
[!Tip] For the most accurate and up-to-date information about checks, services, frameworks, and categories, visit Prowler Hub.
| Provider | Checks | Services | Compliance Frameworks | Categories | Support | Interface |
|---|---|---|---|---|---|---|
| AWS | 662 | 86 | 50 | 19 | Official | UI, API, CLI |
| Azure | 191 | 22 | 25 | 16 | Official | UI, API, CLI |
| GCP | 110 | 20 | 22 | 12 | Official | UI, API, CLI |
| Kubernetes | 92 | 7 | 11 | 11 | Official | UI, API, CLI |
| GitHub | 24 | 3 | 2 | 5 | Official | UI, API, CLI |
| M365 | 144 | 10 | 9 | 10 | Official | UI, API, CLI |
| OCI | 52 | 14 | 5 | 10 | Official | UI, API, CLI |
| Alibaba Cloud | 63 | 9 | 6 | 9 | Official | UI, API, CLI |
| Cloudflare | 43 | 5 | 3 | 9 | Official | UI, API, CLI |
| IaC | See trivy docs. | N/A | N/A | N/A | Official | UI, API, CLI |
| MongoDB Atlas | 10 | 3 | 1 | 8 | Official | UI, API, CLI |
| LLM | See promptfoo docs. | N/A | N/A | N/A | Official | CLI |
| Image | N/A | N/A | N/A | N/A | Official | UI, API, CLI |
| Google Workspace | 65 | 11 | 4 | 6 | Official | UI, API, CLI |
| OpenStack | 34 | 5 | 1 | 9 | Official | UI, API, CLI |
| Vercel | 26 | 6 | 1 | 8 | Official | UI, API, CLI |
| Okta | 29 | 8 | 2 | 2 | Official | UI, API, CLI |
| Linode Contact us | 10 | 3 | 1 | 4 | Unofficial | CLI |
| Huawei Cloud Contact us | 25 | 10 | 1 | 6 | Unofficial | CLI |
| E2E Networks Contact us | 27 | 6 | 0 | 2 | Unofficial | CLI |
| Scaleway Contact us | 1 | 1 | 1 | 1 | Unofficial | CLI |
| StackIT Contact us | 8 | 2 | 1 | 3 | Unofficial | CLI |
| NHN | 6 | 2 | 2 | 0 | Unofficial | CLI |
[!Note] The numbers in the table are updated periodically.
[!Note] Use the following commands to list Prowler's available checks, services, compliance frameworks, and categories:
prowler <provider> --list-checksprowler <provider> --list-servicesprowler <provider> --list-complianceprowler <provider> --list-categories
Prowler Local Server offers flexible installation methods tailored to various environments:
For detailed instructions on using Prowler Local Server, refer to the usage guide.
Docker Compose installed: https://docs.docker.com/compose/install/.macOS/Linux:
VERSION=$(curl -s https://api.github.com/repos/prowler-cloud/prowler/releases/latest | jq -r .tag_name)
curl -sLO "https://raw.githubusercontent.com/prowler-cloud/prowler/refs/tags/${VERSION}/docker-compose.yml"
# Environment variables can be customized in the .env file. Using default values in production environments is not recommended.
curl -sLO "https://raw.githubusercontent.com/prowler-cloud/prowler/refs/tags/${VERSION}/.env"
docker compose up -d
Windows PowerShell:
$VERSION = (Invoke-RestMethod -Uri "https://api.github.com/repos/prowler-cloud/prowler/releases/latest").tag_name
Invoke-WebRequest -Uri "https://raw.githubusercontent.com/prowler-cloud/prowler/refs/tags/$VERSION/docker-compose.yml" -OutFile "docker-compose.yml"
# Environment variables can be customized in the .env file. Using default values in production environments is not recommended.
Invoke-WebRequest -Uri "https://raw.githubusercontent.com/prowler-cloud/prowler/refs/tags/$VERSION/.env" -OutFile ".env"
docker compose up -d
Warning
Stars on GitHub
Reverse engineer anything with agents, from app behavior down to native binaries.
@morlutoA skill pack for authorized reverse engineering, security research, and penetration testing that routes tasks to the right skill and sets up needed tools on demand. It covers API security assessment and Android APK analysis, among others.
 @zhaoxuya520
Gives an AI agent the step-by-step workflow a senior security analyst follows, covering when to use each technique, what to check first, how to run it and how to verify the result. Covers incident response, forensics, threat intelligence, malware analysis, penetration testing and red teaming.
 @mukul975
Agent skill + stdlib Python service to strip multi-vendor AI provenance marks from text and files, for privacy and hygiene on content you own. The skill is a thin client: it drives the machinery over HTTP, so the agent host needs no Python.
 @guillaumemeyer
Install it with the command on its page. It includes framework-compliance-triage, ai-sdk-5, django-drf. Its skills do not fire on their own yet. Free and open source.
Is this plugin yours?
Claim it with GitHubSubmit a pluginPromote it