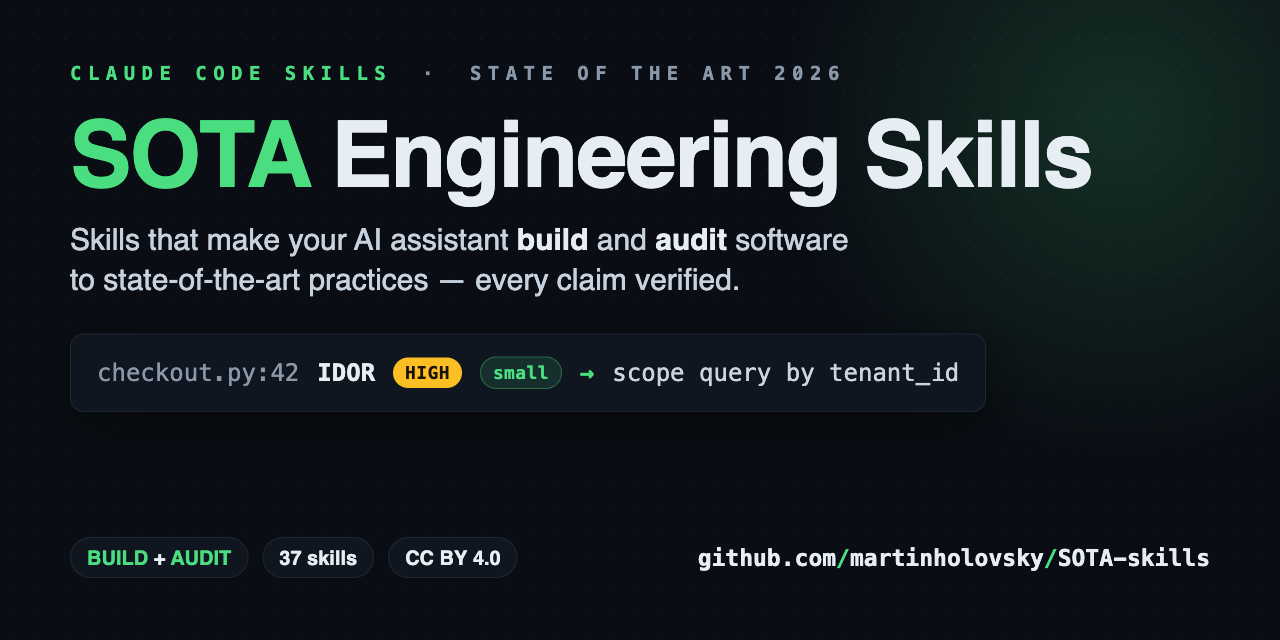
SOTA Engineering Skills


Make your AI coding assistant build and audit like your most senior engineer.
Your assistant is brilliant — it just doesn't know your standards, and it forgets the
ones it does know as the task grows long. SOTA-skills fixes both, and the fix is
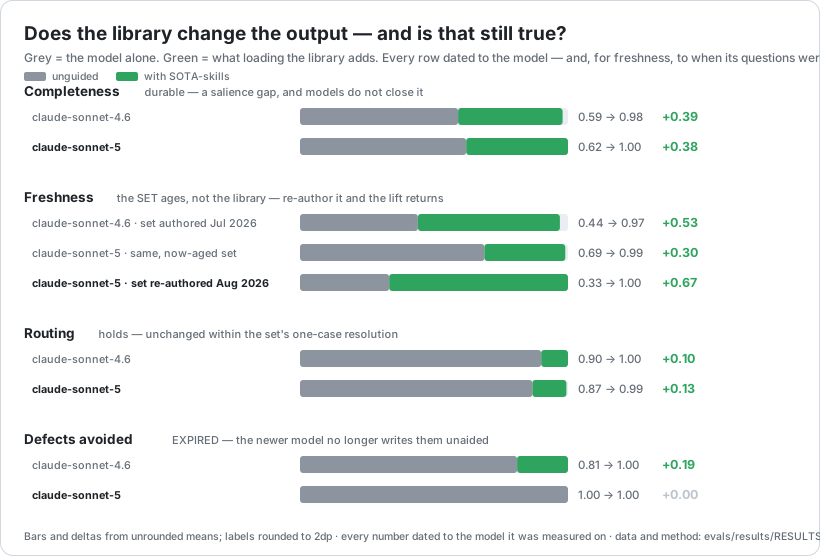
measured: from a bare "build X" prompt, best-practice coverage climbs from ~59%
to ~98% (+0.39) — the model stops silently dropping tests, rate limiting, structured
logging, and TLS (see every number →).
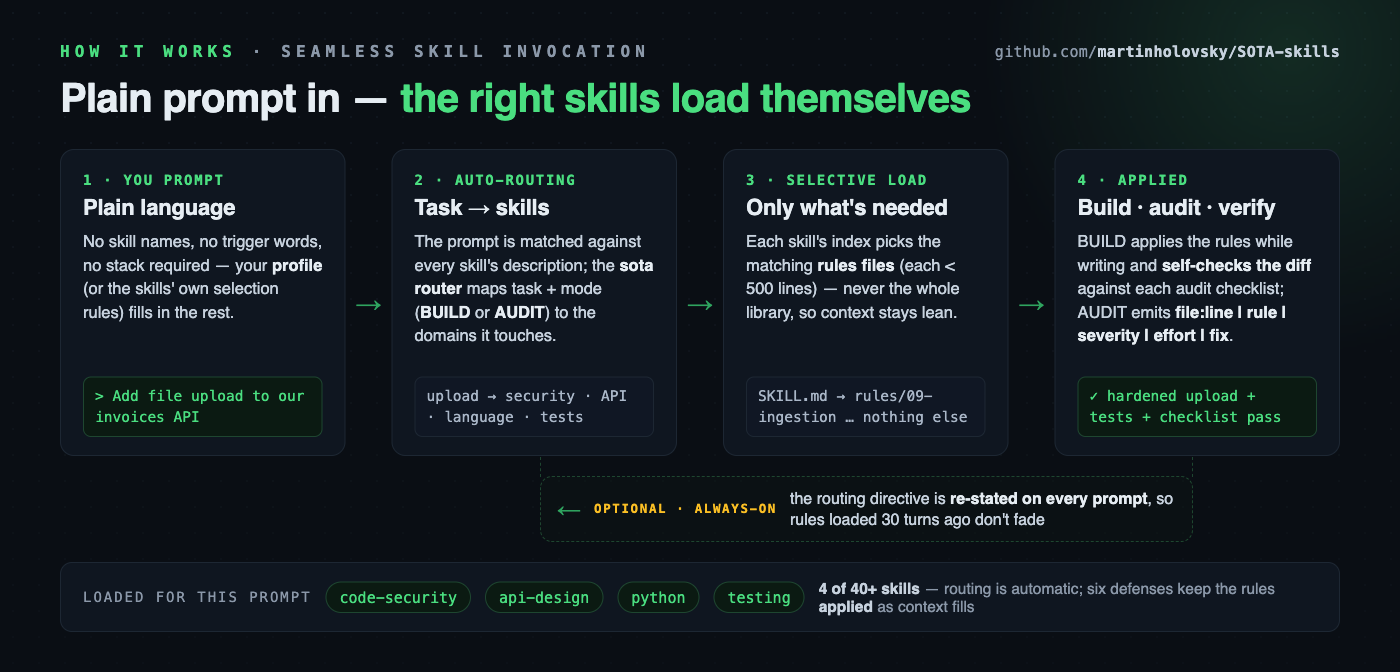
It works by being a loop, not a prompt dump: route in only the rules a task needs,
re-state them every turn, and re-check them last before shipping — so the guidance
survives a long context instead of fading into it. That's why it beats a bigger prompt
instead of becoming one. Native on Claude Code; works with Antigravity CLI, Codex, and any
agent that reads AGENTS.md. Those agents get the skills and an always-on directive, but not
the per-turn re-statement, which is a Claude Code hook
(per-agent detail), and no lift has yet been measured through them.
Under the hood: 43 skills (349 files, ~94k lines) of state-of-the-art 2026
practice, each instruction file under 500 lines so only the matching rules load —
the cap applies to skills/** alone, never to README/CHANGELOG/docs/ — every fast-moving
claim web-verified against a primary source as of the last full sweep (the root
LAST-VERIFIED stamp). Between sweeps an upstream can still move under a claim, so the
router's own operating principle 1 stands: re-verify anything version- or CVE-sensitive at
use time.
Two commands to install:
/plugin marketplace add martinholovsky/SOTA-skills
/plugin install sota-skills@sota-skills
Or clone + link (best if you want a local checkout to read, hack on, or pin).
Skills are discovered from .claude/skills/ (per project) or ~/.claude/skills/
(personal, all projects). Clone the repo, then run the installer — it symlinks
every skill (and your profile, if you have one):
git clone https://github.com/martinholovsky/SOTA-skills && cd SOTA-skills
./scripts/install.sh                 # personal: ~/.claude/skills (all projects)
./scripts/install.sh --project DIR   # one project: DIR/.claude/skills
./scripts/install.sh --target all    # also ~/.agents/skills (Copilot, Codex, Cursor, Gemini CLI) + Antigravity's own dirs
./scripts/install.sh --copy          # copy instead of symlink (pin a snapshot)
./scripts/install.sh --mcp           # optional: register the read-only MCP server for other agents
The installer colour-codes what it did (✓ done · ↻ changed or act on this ·
· no-op) and drops to plain ASCII when the output is not a terminal, on a
non-UTF-8 locale, on TERM=dumb, or with NO_COLOR set — --color=always|never|auto
(or --no-color) overrides the detection either way.
Then describe the task in plain language — routing loads the right skills; the
stack comes from your profile or the skills' defaults (naming one is optional):
Design a multi-tenant invoicing service.
Run a full audit of this repo — severity, effort, and fix on every finding.
More install options: Installation · more prompts: Using it.
Five slash commands ship with the library — four bracket a working session, the fifth is
the heavy escalation. scripts/install.sh links them into ~/.claude/commands/, so they work
in any project, not just this one:
| When | What it does |
|---|
/sota-resume | start of a session | Finds the open work — every tracker, checkbox and TODO marker, swept with a controlled search — classifies it (ready · needs a decision · deferred · not an item · already done and never ticked off, or made unnecessary by a control that already covers the gap), shows you the table, then executes what you agree to against the project's own CI. |
/sota-close | end of a session | The closure pass: retract first, record open items where the next session will trip over them, update what the session made false, re-derive every number from its source, say what is not done and blocked on whom, then commit the evidence. |
/sota-audit | work finished, or a codebase you did not write | Audits what is in front of you against the library: agrees and pins the scope (a diff's callers included), maps the trust boundaries, runs the scanners that are installed, maps every surface to its owning skills and says which rules files nobody opened, walks each Audit checklist item by item, then fixes what you agree to. |
/sota-deep-audit | a milestone, an inheritance, a go/no-go | The heavy pass, and expensive: the same standard as /sota-audit, run so you can trust the result without trusting the auditor — the full threat model reconstructed from the code (DFD, tested assumptions, a control-presence matrix), then the audit fanned across independent agents, re-measures the numbers past decisions rest on, and hands every serious finding to a refuter that did not find it. |
/sota-report | end of a session | Writes a gitignored field report on where the guidance failed, was absent, was wrong — or was right and did not fire. Prints a gh issue create line; it never posts anything itself. |
They take free-text arguments (/sota-close focus on the migration branch). Full detail:
slash commands.
Contents
- Standards & practices baked in · What the audit hunts that a scanner can't · How the numbers are kept honest
- Skills · Coverage & non-goals
- Installation · From the Claude directory · Always-on routing · Updating
- Using it — slash commands (
/sota-resume · /sota-audit · /sota-deep-audit · /sota-close · /sota-report)
- Optional setup & integrations — badge, gates, other agents, status line, plugin extras
- Structure · How it works · Conventions
- Found a gap? Tell us · Contributing · License
Deeper docs: Find it fast (docs index) · Does it work? (measured results) · Why it works · Why some lifts expire and others don't · Keeping rules applied as context fills · Roadmap · Agent-loop evals — tools, hidden tests, no model judge (separate repo)
Standards & practices baked in
Findings name the control they violate — not just "this looks wrong":
- Security — OWASP Top 10 (2025), ASVS, API & LLM Top 10; findings cite CWE IDs.
Disabled TLS certificate and SSH host-key verification are each stated once, with a
detector per library read from that library's own source
- OWASP, item by item — 19 OWASP projects compared with the library one item at a time
(7,439 items, 2026-09-25); every one of the 847 gap themes was adopted, found covered, or
recorded with a reason (ADOPTION-LOG). New ground includes
anti-automation and abuse of value-granting flows,
browser response hardening (Fetch Metadata, HSTS rollout),
file uploads, SBOM content, dependency adoption,
vulnerability remediation beyond the score,
tag manager governance, the JVM web layer, and audit reports that
carry reproduction steps and a finding lifecycle. Where a rule is detectable in code or
config it ships an audit probe tested on a known-bad and a known-good fixture
- Languages — all 10 language skills (Rust → Swift, below) get the same rigor;
formal standards where they exist: SEI CERT (C, C++, Java), MISRA C/C++, ANSSI Rust.
The nine that existed on 2026-09-24 were each gap-checked against their ecosystem's own
scanner registry (LANGUAGE-TIER). Every language also says when an
unused suppression fails CI, which failures no catch/recover sees, and what silently
unfreezes a frozen install, each fact validated against a primary source (2026-10-25).
Each also says when formal verification applies and which mutation-testing tools fail the build;
protocol designs are model-checked before they are built (
sota-architecture rules/03 §12a)
- One rule, one place — 81 places where duplicated guidance had drifted between skills
were reconciled against primary sources (retry policy, severities, workload identity);
every numbered rule section and checklist item now cite each other, and every skill has
declared routing, so a rule cannot sit where no audit or task reaches it
- Supply chain — SLSA, Sigstore, in-toto, SBOM (CycloneDX/SPDX), NIST SSDF
- Cloud & identity — CIS Benchmarks, NIST 800-207 zero trust, NIST 800-63-4,
OAuth 2.1, FAPI 2.0, passkeys, SPIFFE
- Privacy & compliance — GDPR, CCPA/CPRA, HIPAA, PCI DSS 4.x, SOC 2,
ISO 27001, EU AI Act, NIS2, DORA
- Government & regulated — NIST CSF 2.0, 800-53, 800-171/CMMC, FedRAMP,
EU Cyber Resilience Act, IEC 62443, ISO/IEC 29147 & 30111 (vulnerability
disclosure and the handling process behind it)
- Threats, detection & AI/ML — STRIDE, LINDDUN, MITRE ATT&CK & ATLAS,
NIST 800-61, NIST AI RMF
- Frontend, mobile & testing — WCAG 2.2 AA, Core Web Vitals, OWASP MASVS & WSTG
Named standards are the floor. Most of the library is the practice layer no
regulation writes down: cancellation & backpressure, retries with jitter,
circuit breakers, outbox/saga, double-entry ledgers and the reconciliation
that proves an integration is complete rather than merely correct,
zero-downtime migrations, measure-first performance, API evolvability,
per-language idioms, SLOs, test-suite health — and the ones that only show up
once something is already running: triaging a vulnerability report a stranger
sent you (reproduce before you rate it, check the cited code even exists, and
decide the regulatory clock explicitly, because it starts at awareness), and
why a skill can stop triggering with nothing about it changed (a length cap is


 @mattpocock


