



rea
Reverse engineer anything with agents, from app behavior down to native binaries.
420k
 @morluto
Runtime security for AI coding agents that observes, asks for approval on, or blocks risky tool calls before they run, covering secret leaks, prompt injection, and supply chain risks through a local dashboard. Works across agents such as Claude and Codex.
Claude Code
> /plugin marketplace add PrismorSec/prismor> /plugin install prismor@prismor
Codex
$ npx skills add PrismorSec/prismor -a codex
Cursor
$ npx skills add PrismorSec/prismor -a cursor
Gemini CLI
$ npx skills add PrismorSec/prismor -a gemini-cli
GitHub Copilot
$ copilot plugin marketplace add PrismorSec/prismor$ copilot plugin install prismor@prismor
OpenCode
$ npx skills add PrismorSec/prismor -a opencode
Windsurf
$ npx skills add PrismorSec/prismor -a windsurf
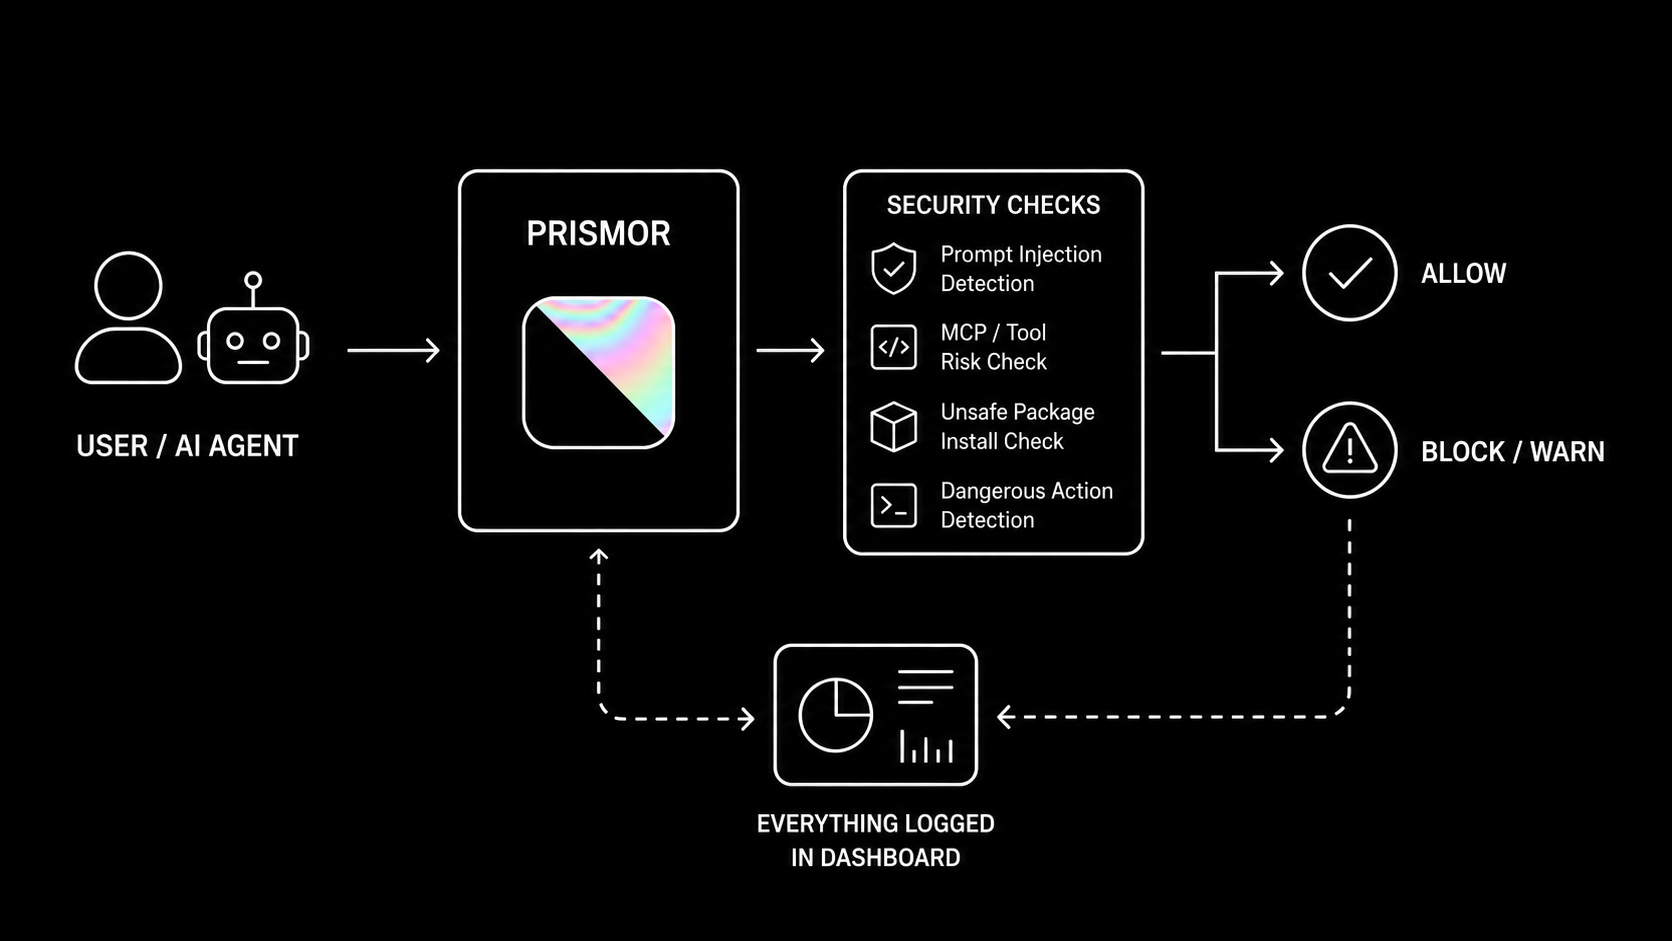


AI agents execute shell commands, read and write files, access credentials, and call external APIs. They do this autonomously, often across many steps, with limited checkpoints.
This creates risks that traditional security tooling isn't designed for:
.env or credential files as part of a debugging task and sends the content outboundStandard OS-level and endpoint security tools monitor the kernel and filesystem. But they lack the context to make AI usable
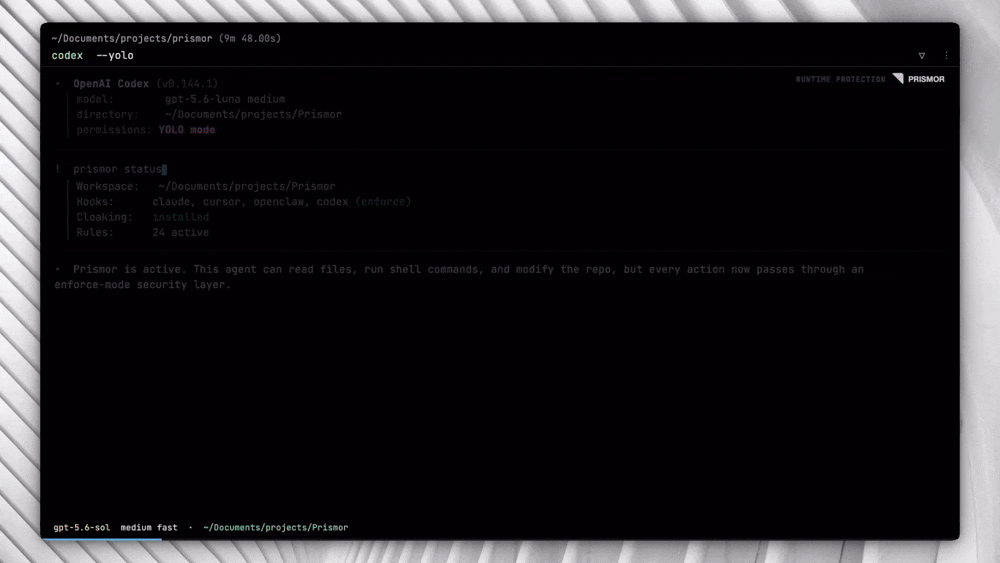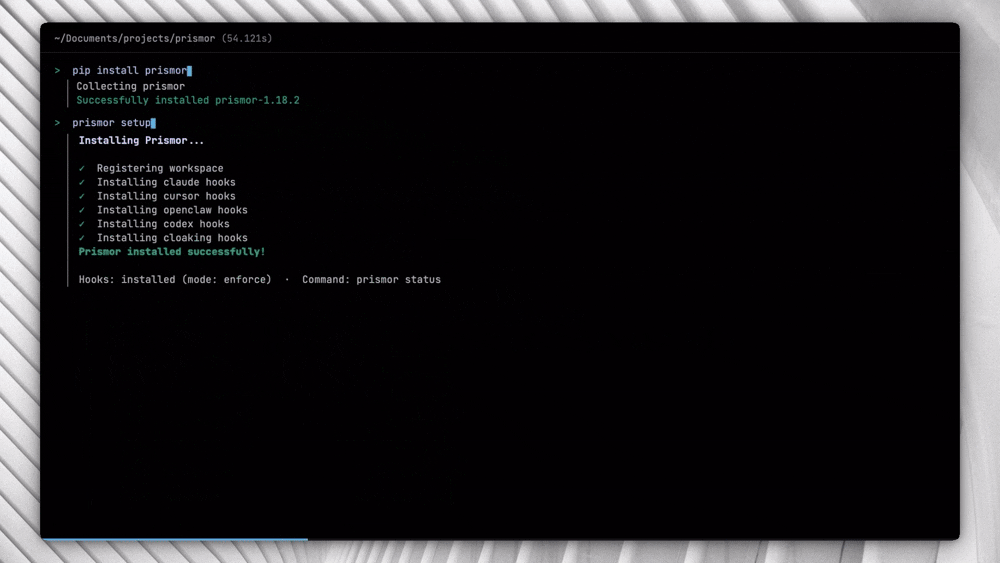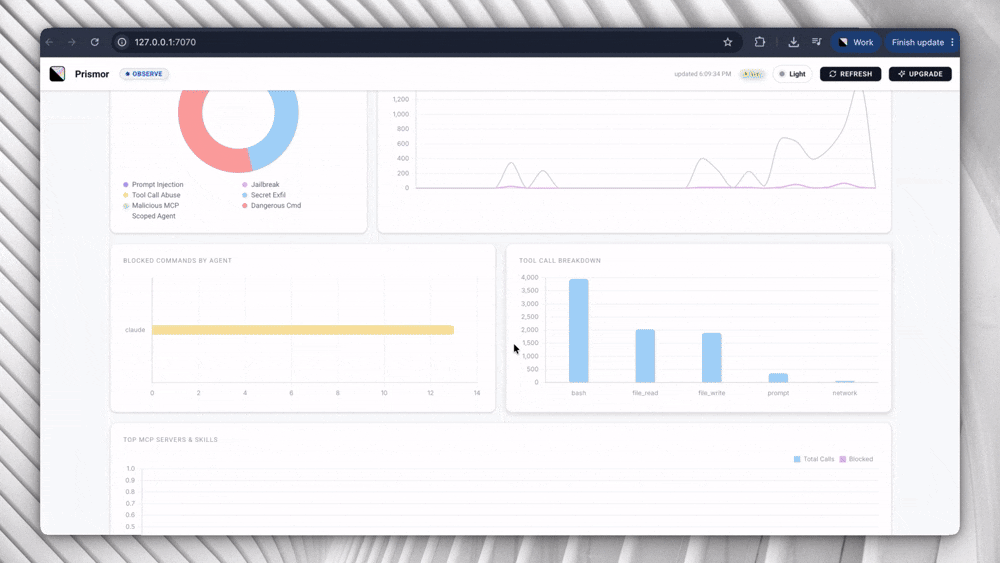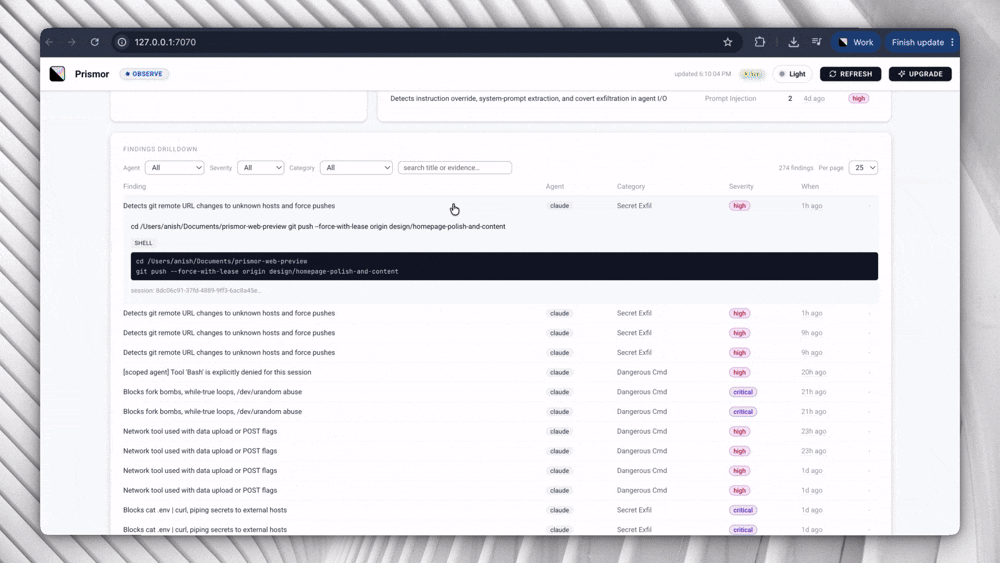
pip install prismor
prismor setup
For the Skill, curl, and git-clone alternatives, plus PEP 668 systems and secret-cloaking setup, see the full installation guide.
tools/call is policy-evaluated before it forwards and each response is injection-scanned before the model sees it, so a poisoned tool result never becomes context. prismor mcp-gateway install moves an existing .mcp.json behind itprismor proxy with ANTHROPIC_BASE_URL, OPENAI_BASE_URL, or the Google Gen AI SDK's HttpOptions(base_url=...) and nothing else about the agent changes. Every tool call the model proposes — Anthropic tool_use, OpenAI tool_calls, Gemini functionCall — is reshaped into the same event a Bash hook produces and judged by the same rule, with streamed calls held until they can be judgedprismor inference-hook serve, which runs your policy on the transcript and answers allow/deny before the model runs — signed requests (Standard Webhooks), fail-closed, shadow mode, nothing to install on user devices. prismor inference-hook test sends signed sample frames to check the wiring_meta, and prismor tags lists, tests, and lints the rule expressionsinstall-hooks --portable writes a hook config that is safe to commitprismor rca, blame, friction and session --changes answer where an agent run went wrong, who wrote a line, and what agents keep tripping overStars on GitHub
Reverse engineer anything with agents, from app behavior down to native binaries.
@morlutoA skill pack for authorized reverse engineering, security research, and penetration testing that routes tasks to the right skill and sets up needed tools on demand. It covers API security assessment and Android APK analysis, among others.
 @zhaoxuya520
Gives an AI agent the step-by-step workflow a senior security analyst follows, covering when to use each technique, what to check first, how to run it and how to verify the result. Covers incident response, forensics, threat intelligence, malware analysis, penetration testing and red teaming.
 @mukul975
Agent skill + stdlib Python service to strip multi-vendor AI provenance marks from text and files, for privacy and hygiene on content you own. The skill is a thin client: it drives the machinery over HTTP, so the agent host needs no Python.
 @guillaumemeyer
Install it with the command on its page. It includes prismor. Its skills do not fire on their own yet. Free and open source.
Is this plugin yours?
Claim it with GitHubSubmit a pluginPromote it