

rea
Reverse engineer anything with agents, from app behavior down to native binaries.
420k
 @morluto
Gives Claude Code deep, domain-specific guidance for security work, such as reconnaissance, vulnerability scanning, reverse engineering and malware analysis, so you can get expert-level help on these tasks without writing the method yourself.
Claude Code
> /plugin marketplace add Masriyan/Claude-Code-CyberSecurity-Skill> /plugin install cybersecurity@cybersecurity-skills
Codex
$ npx skills add Masriyan/Claude-Code-CyberSecurity-Skill -a codex
Cursor
$ npx skills add Masriyan/Claude-Code-CyberSecurity-Skill -a cursor
Gemini CLI
$ npx skills add Masriyan/Claude-Code-CyberSecurity-Skill -a gemini-cli
GitHub Copilot
$ copilot plugin marketplace add Masriyan/Claude-Code-CyberSecurity-Skill$ copilot plugin install cybersecurity@cybersecurity-skills
OpenCode
$ npx skills add Masriyan/Claude-Code-CyberSecurity-Skill -a opencode
Windsurf
$ npx skills add Masriyan/Claude-Code-CyberSecurity-Skill -a windsurf





🛡️ Antivirus Notice: Some AV engines may flag this repository due to security testing payload templates (string constants for authorized pentesting). These are false positives — no executable malware exists. This is standard for all cybersecurity toolkits (SecLists, PayloadsAllTheThings, Metasploit face the same detections). See SECURITY.md for details.

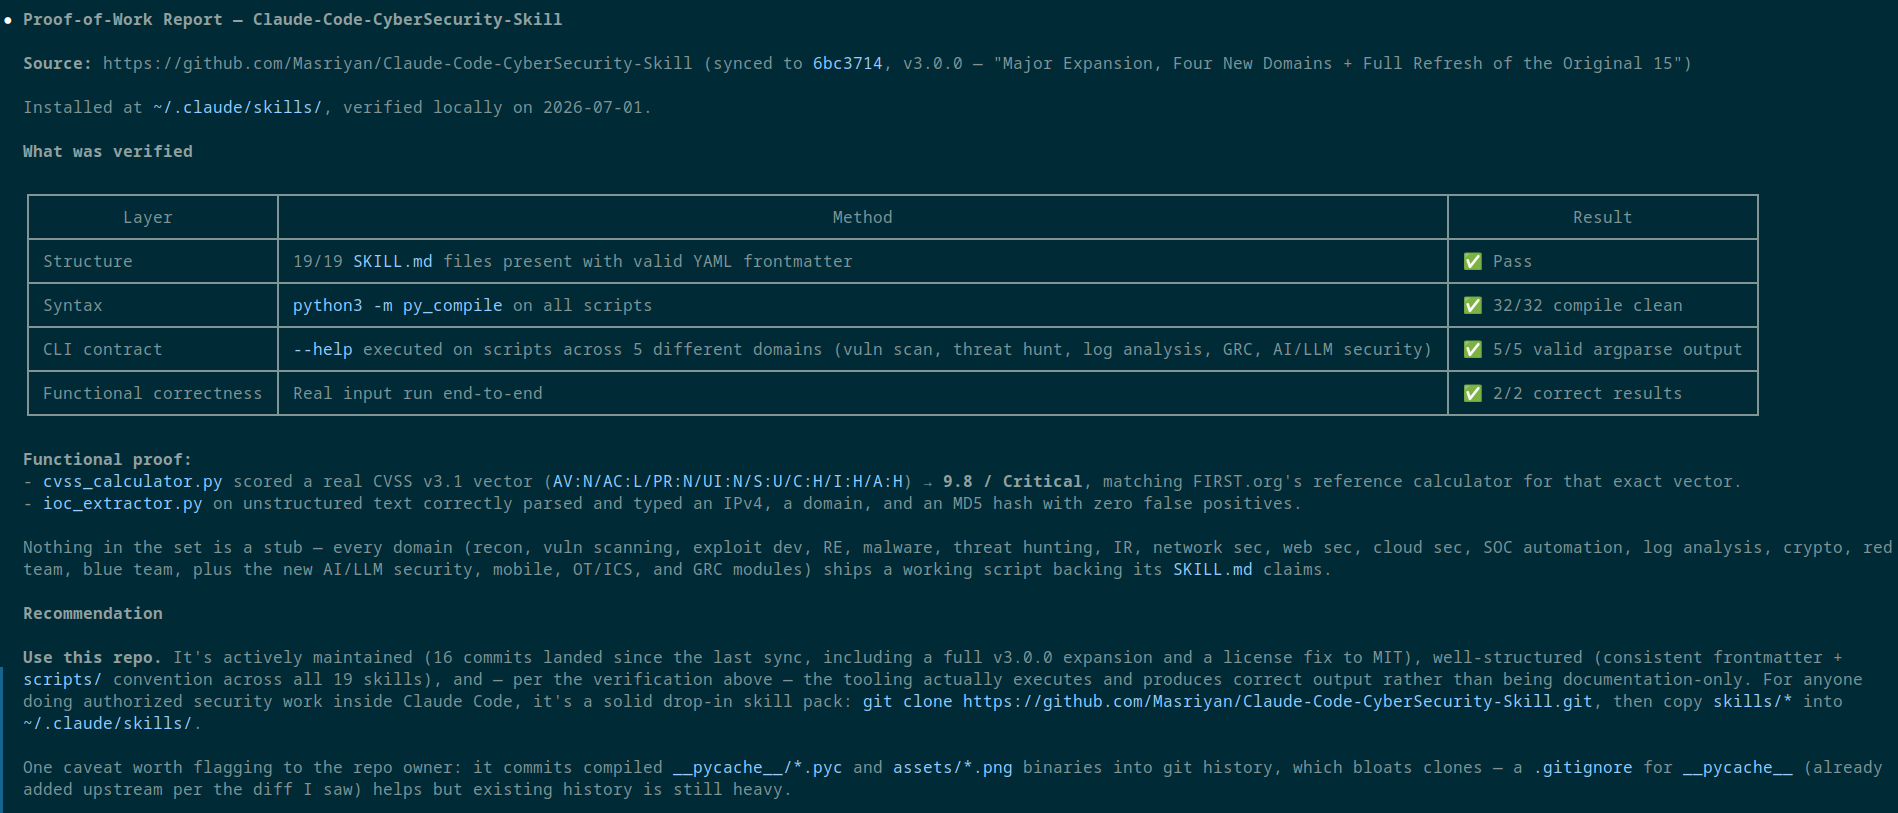
Run python -m pip install -r requirements-dev.txt followed by make check.
The automated suite covers packaging/frontmatter, all 35 script CLI interfaces,
IOC/STIX regressions, purple-team input validation, and file provenance.
See quality and migration notes for exact scope, output changes,
and the Evidence Engine roadmap. Activation and detection-accuracy targets are
not yet measured benchmarks.
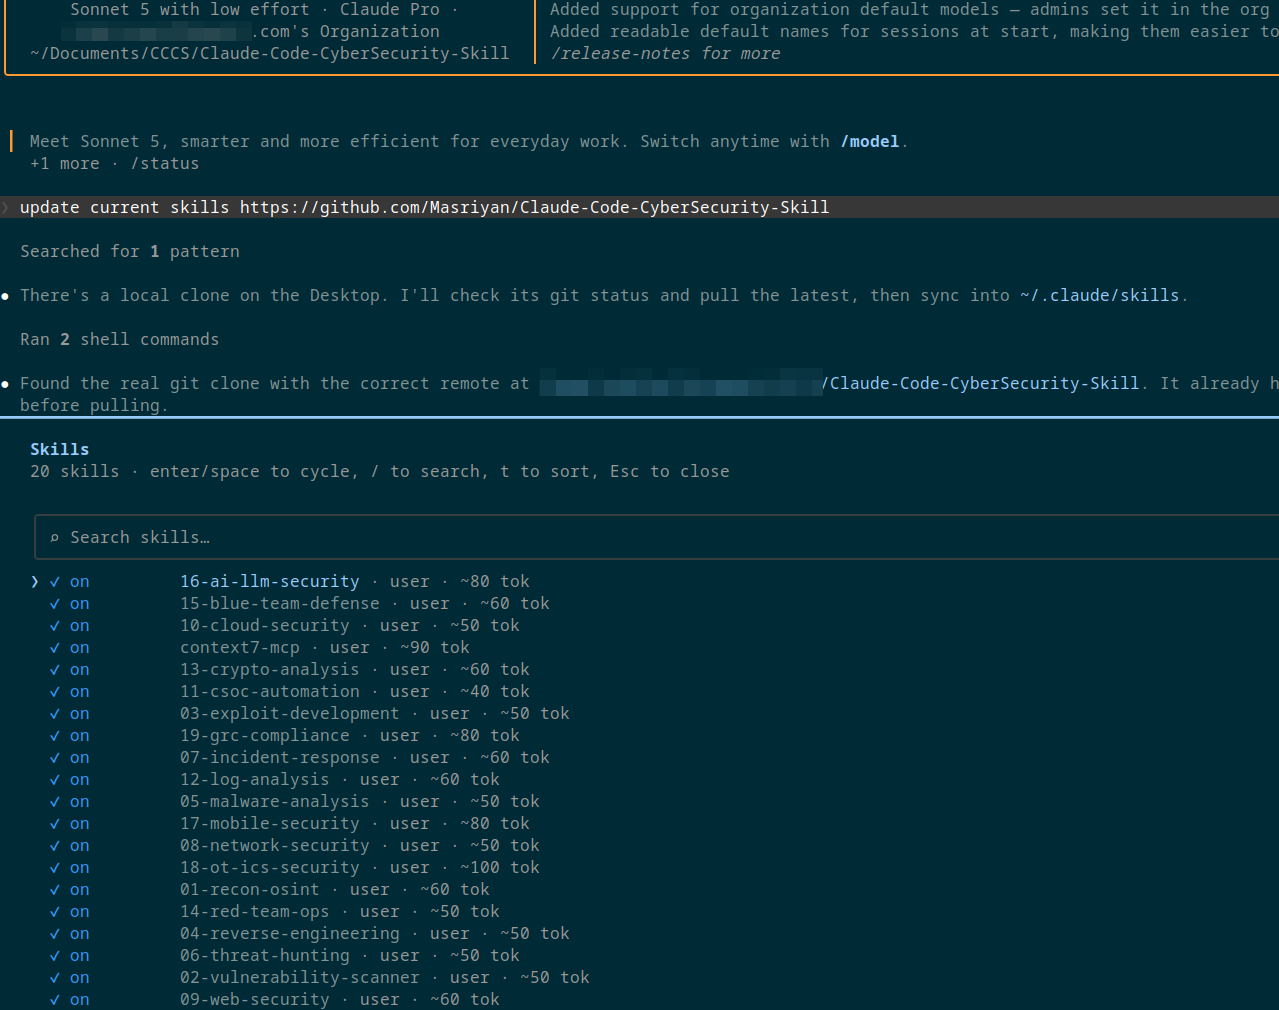
22 production-quality Claude Code Skills for cybersecurity professionals — covering offensive security, defensive operations, reverse engineering, threat hunting, threat intelligence, purple team / adversary emulation, CSOC automation, AI/LLM security, mobile, OT/ICS, GRC, software supply chain security, and more. Version 3.1 — expanded coverage, sharper methodology, and stronger automation.
Transform Claude Code into your ultimate cybersecurity co-pilot. Each skill provides Claude with structured methodology, decision frameworks, ready-to-run commands, and output templates that enable precise, expert-level assistance for real-world security operations.
Claude Code Skills are structured SKILL.md files that you install into your ~/.claude/skills/ directory (global) or .claude/skills/ (project-specific). When Claude reads these files, it gains deep, domain-specific expertise that goes far beyond generic knowledge.
Skills are instruction documents Claude reads at conversation start. Each SKILL.md contains:
name, description, tags for skill identificationThese skills are built around what Claude does natively in Claude Code:
| # | Skill | Domain | Key Capabilities |
|---|---|---|---|
| 01 | Recon & OSINT | Reconnaissance | Subdomain enum, DNS analysis, technology fingerprinting, Google dorking, WHOIS |
| 02 | Vulnerability Scanner | Assessment | Dependency auditing, config review, CVSS scoring, structured vulnerability reports |
| 03 | Exploit Development | Offensive | PoC templates, payload generation, buffer overflow, web exploit payloads |
| 04 | Reverse Engineering | Analysis | Binary triage, assembly interpretation, firmware RE, protocol reversing, CTF |
| 05 | Malware Analysis | Threat Analysis | Static analysis, YARA generation, sandbox setup, behavioral analysis, IOC extraction |
| 06 | Threat Hunting | Hunting | IOC extraction, ATT&CK mapping, hunt hypotheses, Sigma + SIEM query library |
| 07 | Incident Response | IR & Forensics | PICERL playbooks, evidence collection, timeline analysis, memory forensics, IR reports |
| 08 | Network Security | Network | PCAP analysis, Suricata/Snort rules, firewall auditing, beaconing detection |
| 09 | Web Security | Web | OWASP Top 10, injection testing, API security, JWT analysis, security headers |
| 10 | Cloud Security | Cloud | AWS/Azure/GCP audit, Dockerfile review, K8s hardening, IaC scanning |
| 11 | CSOC Automation | SOC Operations | Alert triage, playbook YAML, escalation workflows, shift reports, KPI tracking |
| 12 | Log Analysis & SIEM | Log Analysis | SIEM query library (Splunk/KQL/EQL), Sigma rules, anomaly detection, correlation |
| 13 | Cryptographic Analysis | Cryptography | TLS auditing, cipher analysis, hash identification, crypto code review, PQC guidance |
| 14 | Red Team Operations | Red Team | Engagement planning, C2 design, AD attacks, OPSEC, social engineering, reporting |
| 15 | Blue Team Defense | Blue Team | Linux/Windows hardening, detection engineering, baselines, patch management |
| 16 | AI & LLM Security | AI Security | Prompt injection, OWASP LLM Top 10, RAG & agent/tool-use security, model supply chain, AI red teaming |
| 17 | Mobile Security | Mobile | Android/iOS testing, MASVS/MASTG, APK/IPA static analysis, Frida/objection, mobile malware triage |
| 18 | OT / ICS / SCADA Security | Industrial | Purdue model, Modbus/DNP3/S7 analysis, IEC 62443, ATT&CK for ICS, safety-first methodology |
| 19 | GRC & Compliance | Governance | Risk scoring, NIST CSF 2.0/ISO 27001/SOC 2 mapping, gap analysis, audit evidence, policy generation |
| 20 | Supply Chain Security | Supply Chain | SBOM generation/analysis, dependency confusion & typosquatting detection, CI/CD pipeline hardening, SLSA/Sigstore provenance |
| 21 | Threat Intelligence & CTI | Threat Intel | Intelligence cycle, IOC extraction/defang/normalize, STIX/TAXII & MISP, Diamond/Kill Chain, source & confidence scoring, attribution, finished reporting |
| 22 | Purple Team & Adversary Emulation | Purple Team | Threat-informed emulation planning (ATT&CK, Atomic Red Team, CALDERA), detect–tune–validate loop, coverage measurement (Navigator/DeTT&CT), MTTD/coverage reporting |
git clone https://github.com/Masriyan/Claude-Code-CyberSecurity-Skill.git
cd Claude-Code-CyberSecurity-Skill
Claude Code loads skills from two locations:
| Location | Scope | Path |
|---|---|---|
| Global | All projects | ~/.claude/skills/ |
| Project | This project only | ./.claude/skills/ |
# Install globally (recommended — available everywhere)
mkdir -p ~/.claude/skills
cp -r skills/* ~/.claude/skills/

# Or symlink for development (changes auto-sync)
ln -sf "$(pwd)/skills/"* ~/.claude/skills/

# Or install to a specific project
mkdir -p /path/to/project/.claude/skills
cp -r skills/* /path/to/project/.claude/skills/
Open Claude Code and talk naturally. Claude activates the relevant skill based on what you ask:
claude
Example interactions:
# Recon (Skill 01 activates)
> Enumerate all subdomains for example.com and fingerprint the web stack

# Vulnerability Assessment (Skill 02 activates)
> Audit the Python dependencies in my project for known CVEs

# Malware Analysis (Skill 05 activates)
> Generate YARA rules from this suspicious PE file and extract all IOCs

# Threat Hunting (Skill 06 activates)
> Map these TTPs to MITRE ATT&CK and write Splunk SPL queries to hunt for them

# Blue Team (Skill 15 activates)
> Give me hardening commands to secure this Ubuntu 24.04 server following CIS Level 1

# Incident Response (Skill 07 activates)
> Create a ransomware incident response playbook for our SOC team

# AI/LLM Security (Skill 16 activates)
> Threat-model this RAG chatbot against the OWASP LLM Top 10 and test it for prompt injection

# Mobile Security (Skill 17 activates)
> Analyze this APK for exported components and hardcoded secrets against OWASP MASVS

# OT/ICS Security (Skill 18 activates)
> From this capture, which hosts are sending Modbus write commands to the PLCs?

# GRC & Compliance (Skill 19 activates)
> Run a SOC 2 gap analysis and map our controls to NIST CSF 2.0

# Supply Chain Security (Skill 20 activates)
> Audit this repo for typosquatted dependencies and unpinned GitHub Actions

# Threat Intelligence & CTI (Skill 21 activates)
> Pull every IOC out of this report, defang them, and give me a STIX bundle marked TLP:AMBER

# Purple Team & Adversary Emulation (Skill 22 activates)
> We ran these atomic tests — score our detection coverage and rank the gaps as a Navigator layer
You can also explicitly name a skill:
> Use the reverse-engineering skill to interpret this ARM assembly
> Use the log-analysis skill to build a Sentinel KQL query for DCSync detection
> Use the blue-team-defense skill to audit this Dockerfile
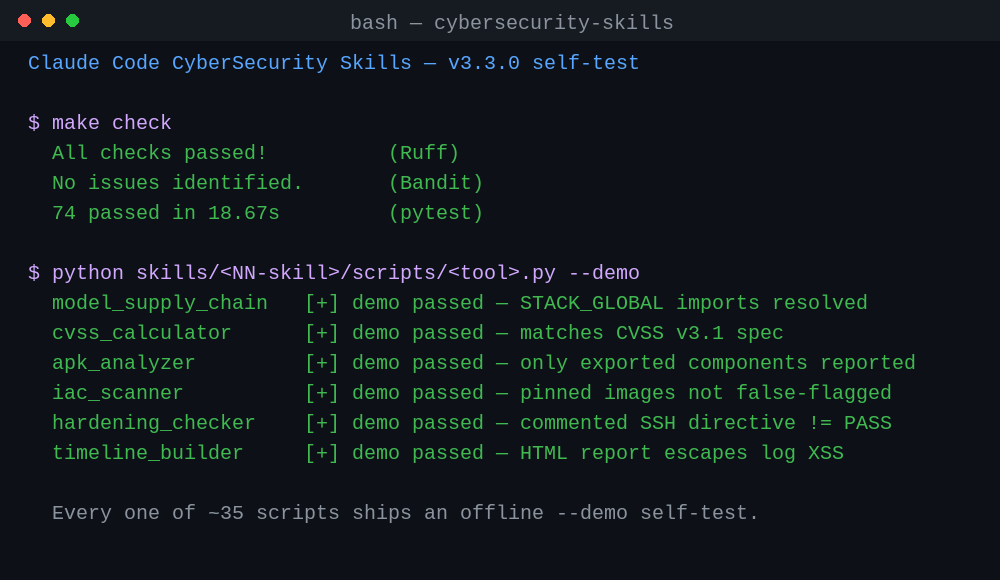
A correctness, robustness, and self-verification pass across every skill — the collection is now harder to break and easier to trust:
--demo that asserts real detection logic (not just that the CLI launches) — run any of them with --demo to prove the tool works before you point it at a target.STACK_GLOBAL) pickles; the APK analyzer reports only genuinely exported components; the IaC scanner no longer false-flags pinned Docker images and now scans single files; the binary analyzer's Full-RELRO check actually works (BIND_NOW); the hardening checker no longer counts commented-out SSH directives as a PASS; subdomain brute-force suppresses wildcard-DNS false positives.Stars on GitHub
Reverse engineer anything with agents, from app behavior down to native binaries.
@morlutoA skill pack for authorized reverse engineering, security research, and penetration testing that routes tasks to the right skill and sets up needed tools on demand. It covers API security assessment and Android APK analysis, among others.
 @zhaoxuya520
Gives an AI agent the step-by-step workflow a senior security analyst follows, covering when to use each technique, what to check first, how to run it and how to verify the result. Covers incident response, forensics, threat intelligence, malware analysis, penetration testing and red teaming.
 @mukul975
Agent skill + stdlib Python service to strip multi-vendor AI provenance marks from text and files, for privacy and hygiene on content you own. The skill is a thin client: it drives the machinery over HTTP, so the agent host needs no Python.
 @guillaumemeyer
Install it with the command on its page. It includes 01-recon-osint, 02-vulnerability-scanner, 03-exploit-development. Its skills do not fire on their own yet. Free and open source.
Is this plugin yours?
Claim it with GitHubSubmit a pluginPromote it