
rea
Reverse engineer anything with agents, from app behavior down to native binaries.
460k
 @morluto
A Claude Code plugin for static analysis and security auditing of Java JAR and WAR packages. It builds a SQLite analysis database and runs audit queries such as method call tracing and vulnerability pattern detection.
Claude Code
> /plugin marketplace add jar-analyzer/jar-analyzer-claude> /plugin install jar-analyzer-plugin@jar-analyzer-marketplace
Codex
$ npx skills add jar-analyzer/jar-analyzer-claude -a codex
Cursor
$ npx skills add jar-analyzer/jar-analyzer-claude -a cursor
Gemini CLI
$ npx skills add jar-analyzer/jar-analyzer-claude -a gemini-cli
GitHub Copilot
$ copilot plugin marketplace add jar-analyzer/jar-analyzer-claude$ copilot plugin install jar-analyzer-plugin@jar-analyzer-marketplace
OpenCode
$ npx skills add jar-analyzer/jar-analyzer-claude -a opencode
Windsurf
$ npx skills add jar-analyzer/jar-analyzer-claude -a windsurf
基于 jar-analyzer 的 Claude Code 插件,用于 Java JAR/WAR 包静态分析与安全审计。
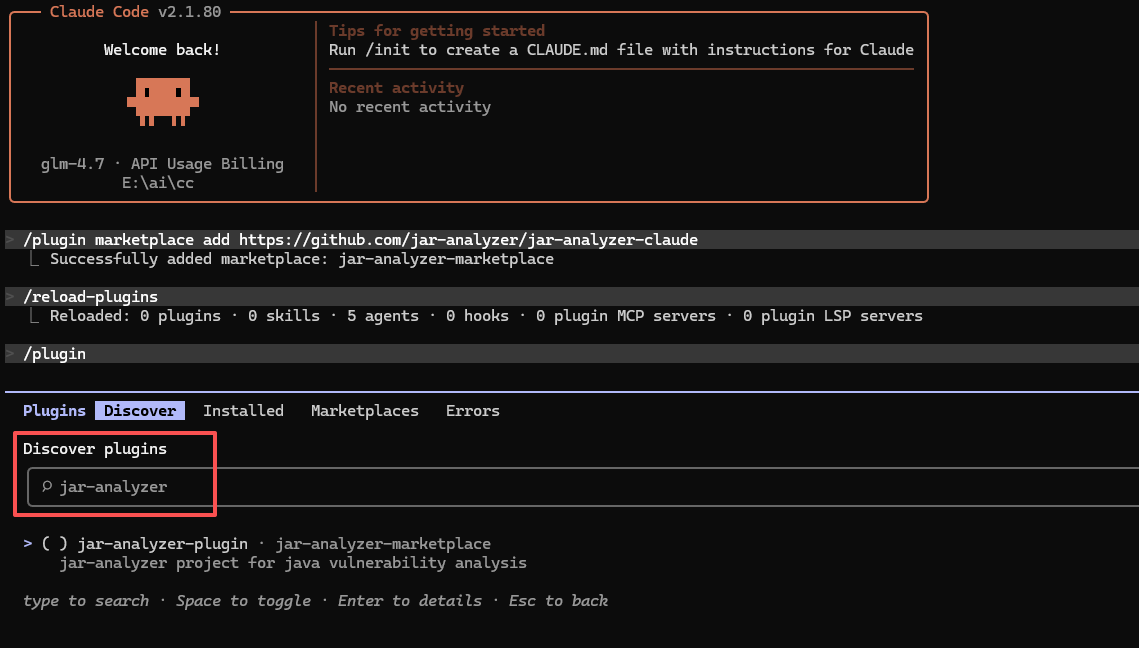
一行命令添加插件市场:
/plugin marketplace add https://github.com/jar-analyzer/jar-analyzer-claude
添加完成后,在插件市场中选择 jar-analyzer-plugin 进行安装。
⚠️ 插件内置了打包好的
jar-analyzer-engine,文件较大,下载可能需要一些时间,请耐心等待。
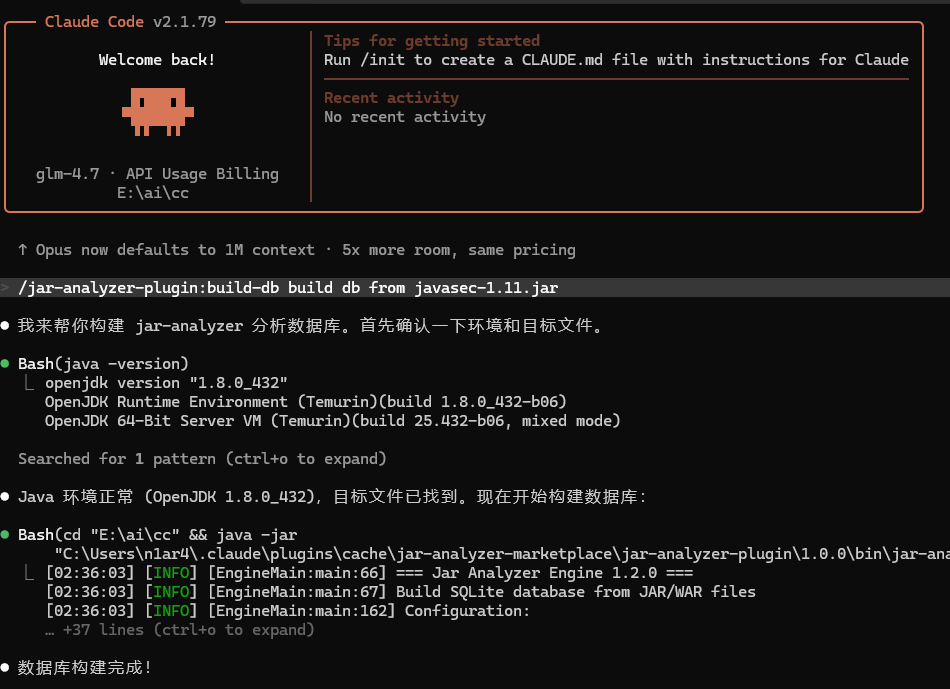
使用 /build-db 命令,指定需要审计分析的 JAR/WAR 文件,构建分析数据库。
💡 建议在空目录中执行,分析完成后当前目录下会生成
jar-analyzer-temp临时目录和jar-analyzer.db数据库文件。
使用 /do-analyze 命令,对数据库执行安全审计查询(优先使用 sqlite3 命令,其次回退到 python 脚本)。
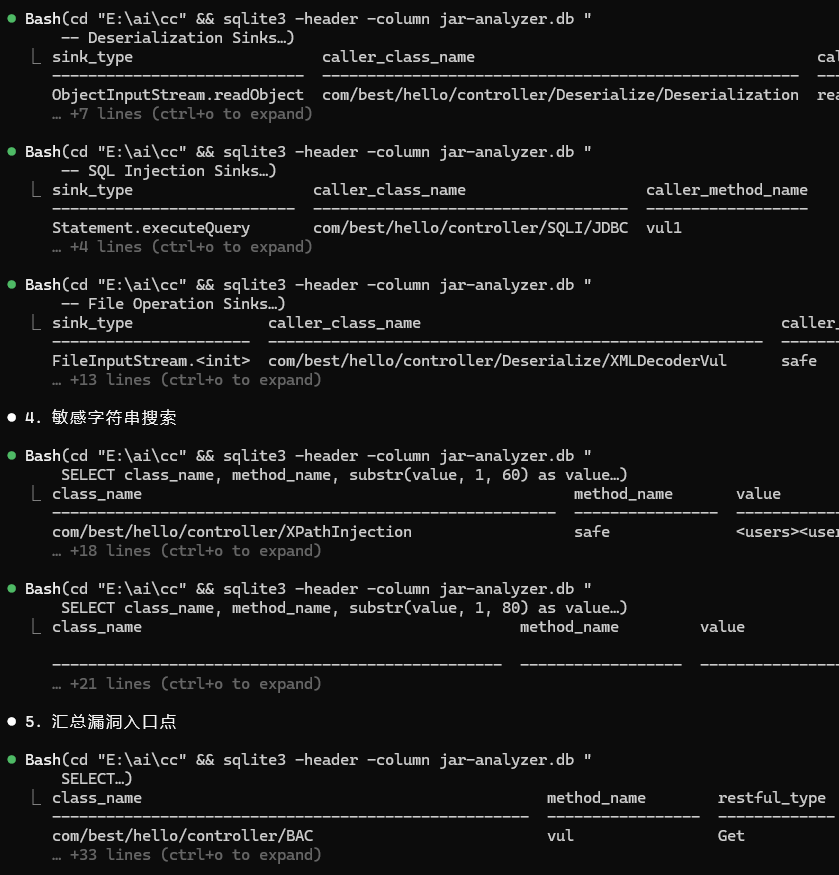
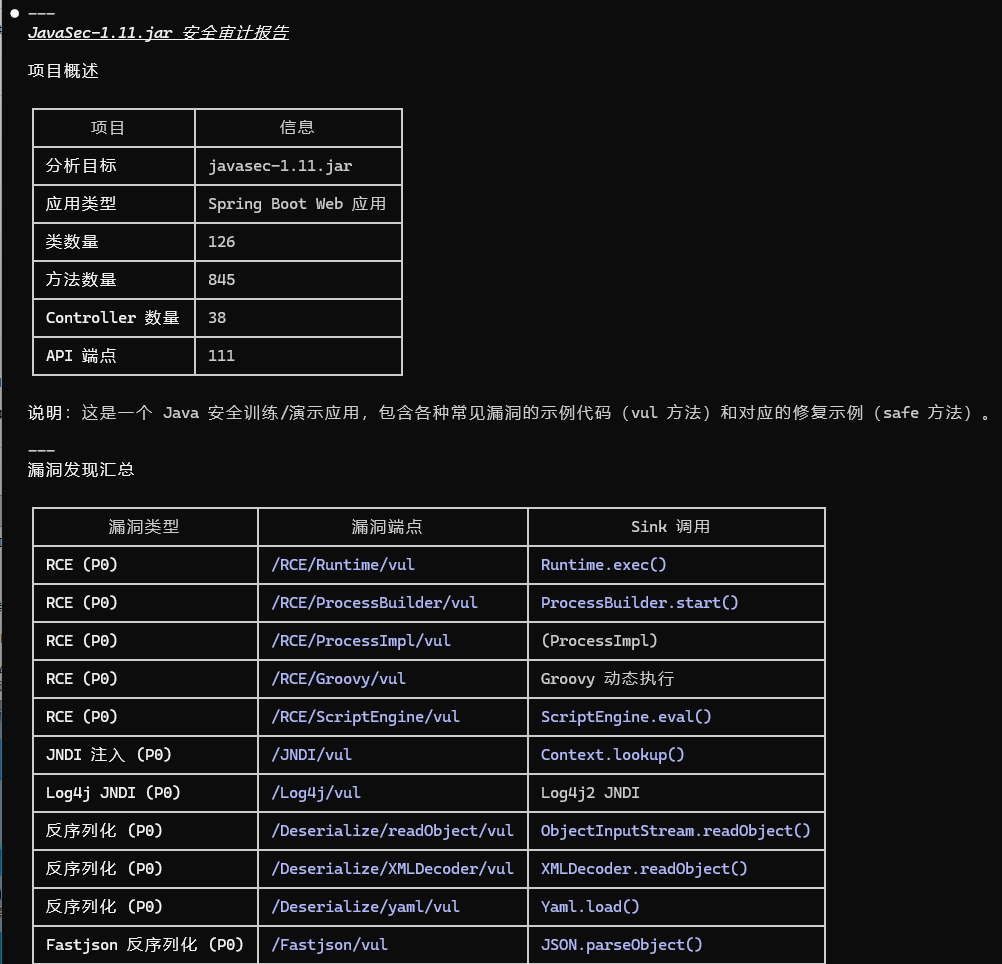
分析完成后,自动生成详细的安全审计报告,坐等结果即可。
| 依赖 | 版本 | 用途 |
|---|---|---|
| Java | 8+ | 运行分析引擎和反编译 |
| Python | 3+(可选) | 执行 SQL 查询脚本(作为 sqlite3 的备选方案) |
Stars on GitHub
Reverse engineer anything with agents, from app behavior down to native binaries.
@morlutoA skill pack for authorized reverse engineering, security research, and penetration testing that routes tasks to the right skill and sets up needed tools on demand. It covers API security assessment and Android APK analysis, among others.
 @zhaoxuya520
Gives an AI agent the step-by-step workflow a senior security analyst follows, covering when to use each technique, what to check first, how to run it and how to verify the result. Covers incident response, forensics, threat intelligence, malware analysis, penetration testing and red teaming.
 @mukul975
Agent skill + stdlib Python service to strip multi-vendor AI provenance marks from text and files, for privacy and hygiene on content you own. The skill is a thin client: it drives the machinery over HTTP, so the agent host needs no Python.
 @guillaumemeyer
A Claude Code plugin for static analysis and security auditing of Java JAR and WAR packages. It builds a SQLite analysis database and runs audit queries such as method call tracing and vulnerability pattern detection. Install it with the command on its page. It includes build-db, do-analyze. Its skills do not fire on their own yet. Free and open source.
Is this plugin yours?
Claim it with GitHubSubmit a pluginPromote it