

rea
Reverse engineer anything with agents, from app behavior down to native binaries.
420k
 @morluto
Scans source code, dependencies and repositories for security weaknesses such as injection flaws and leaked secrets, then merges the findings into one prioritized report. It also captures and replays HTTP traffic through a proxy to help test running applications.
Auto-invoked ships a router so the right skill fires automatically as you prompt. No remembering which skill to call.
Normal is the plain upstream plugin, installed as-is. You invoke its skills yourself.
Claude Code
The plugin> /plugin marketplace add ghostsecurity/skillsAuto-invocation> /plugin marketplace add flowy-sh/flowy-core> /plugin install flowy-core> /plugin install flowy-ghost
Codex
$ npx skills add ghostsecurity/skills --skill exo proxy repo-context report scan-code scan-deps scan-secrets validate -a codex
Cursor
$ npx skills add ghostsecurity/skills --skill exo proxy repo-context report scan-code scan-deps scan-secrets validate -a cursor
Gemini CLI
$ npx skills add ghostsecurity/skills --skill exo proxy repo-context report scan-code scan-deps scan-secrets validate -a gemini-cli
GitHub Copilot
$ npx skills add ghostsecurity/skills --skill exo proxy repo-context report scan-code scan-deps scan-secrets validate -a github-copilot
OpenCode
$ npx skills add ghostsecurity/skills --skill exo proxy repo-context report scan-code scan-deps scan-secrets validate -a opencode
Windsurf
$ npx skills add ghostsecurity/skills --skill exo proxy repo-context report scan-code scan-deps scan-secrets validate -a windsurf
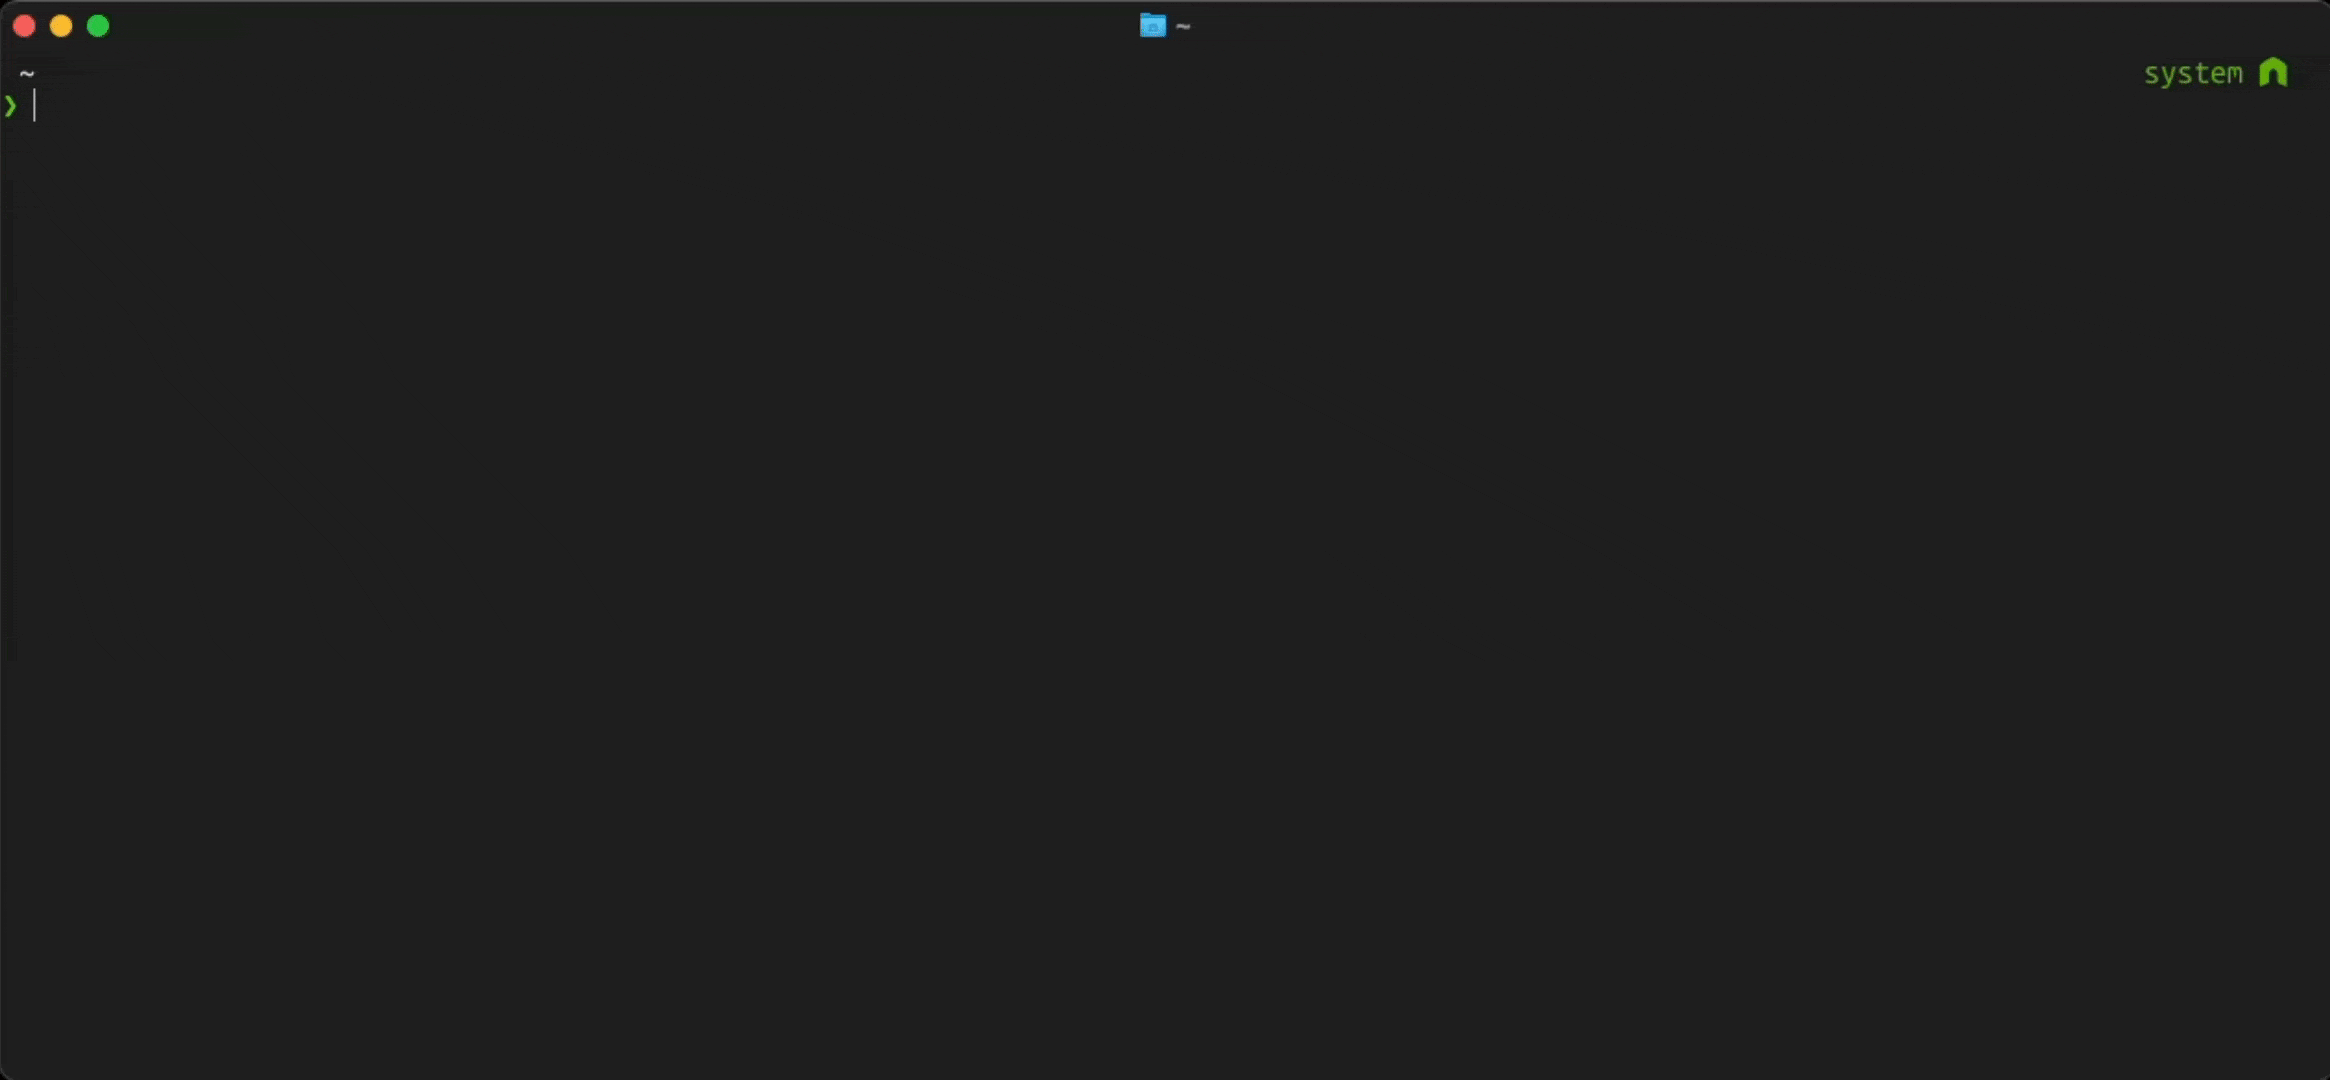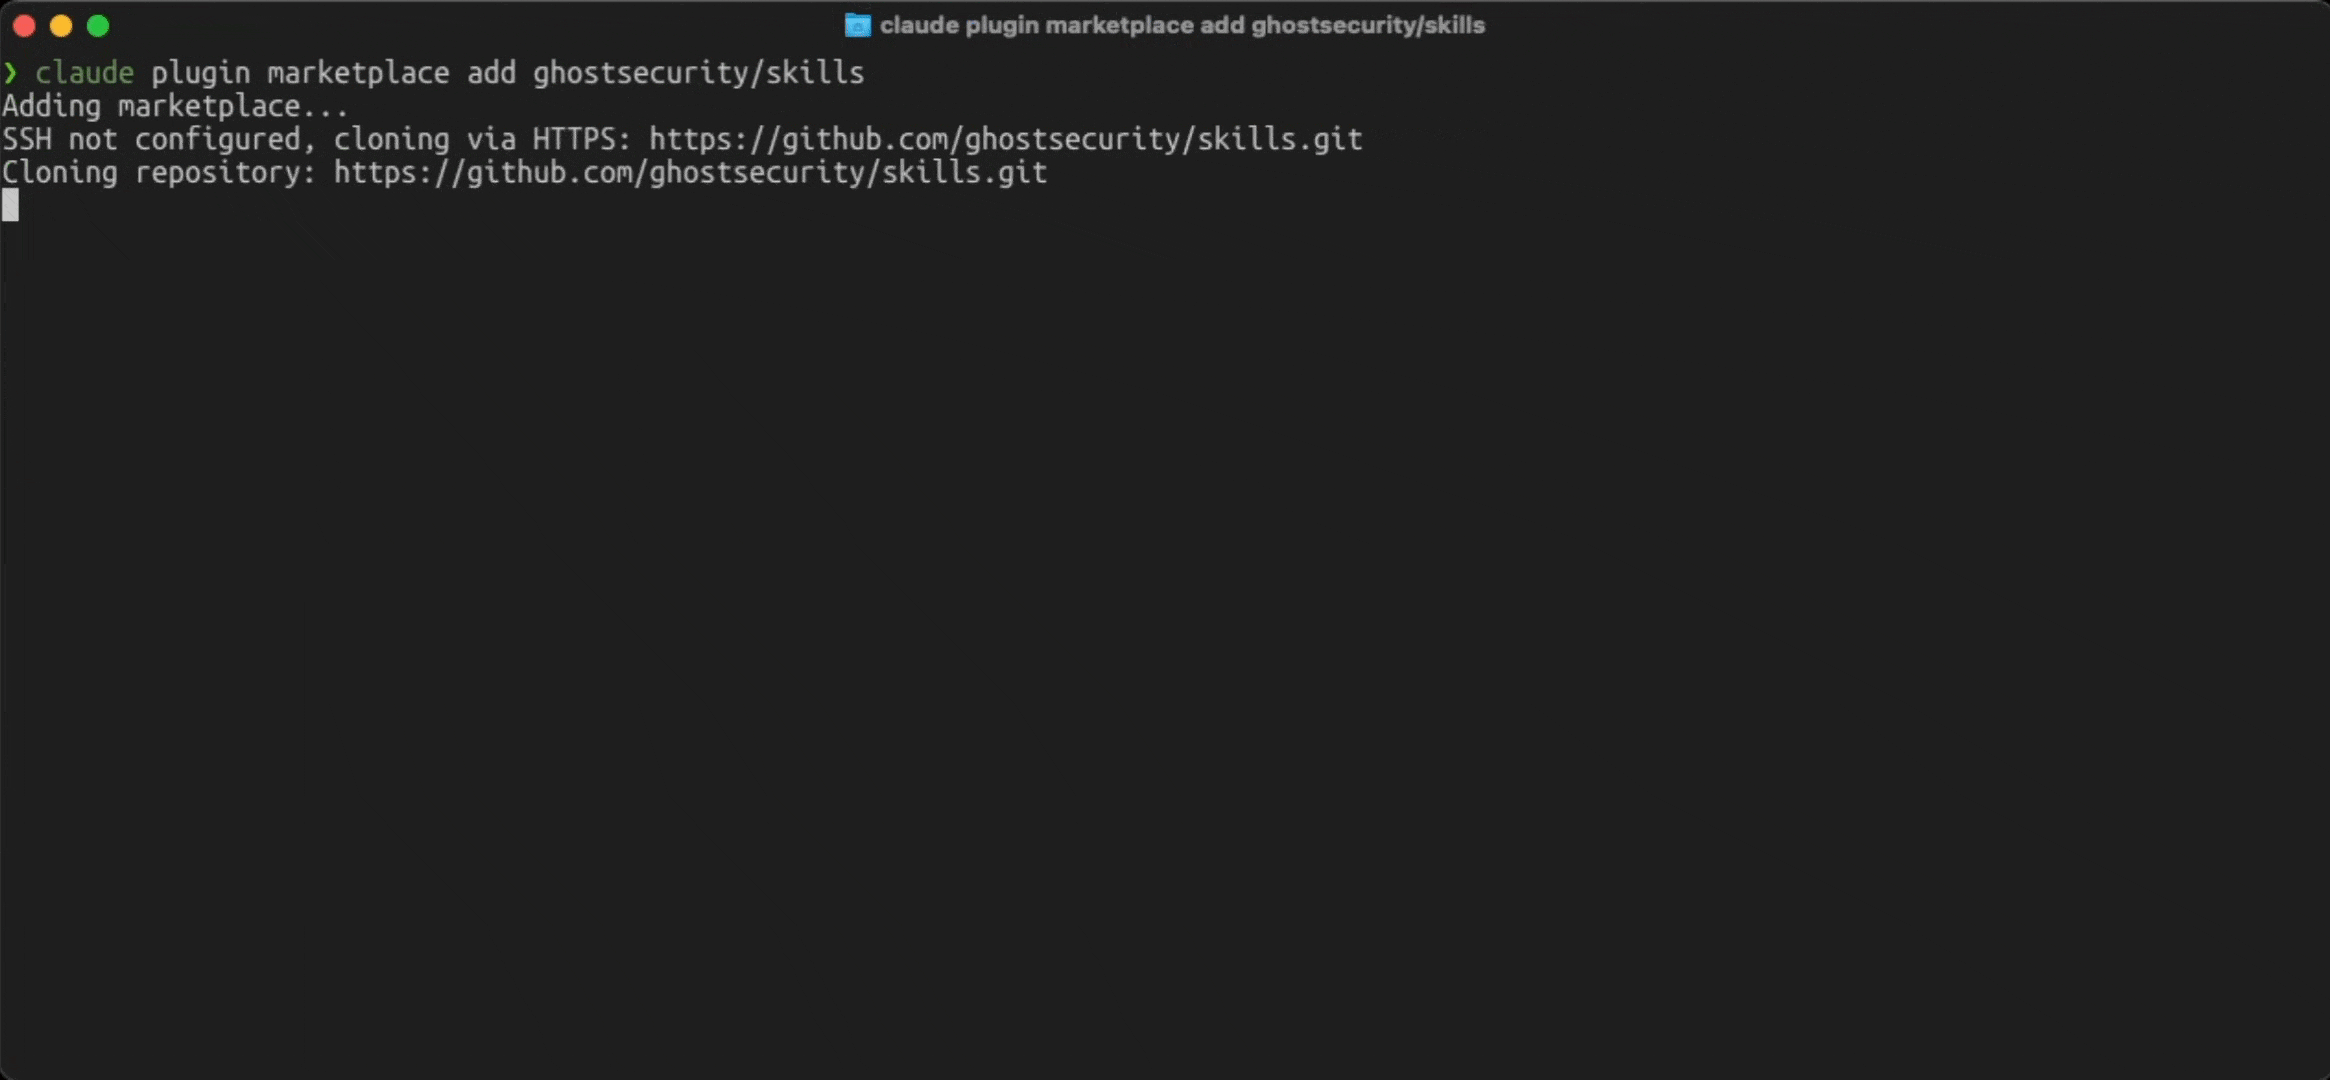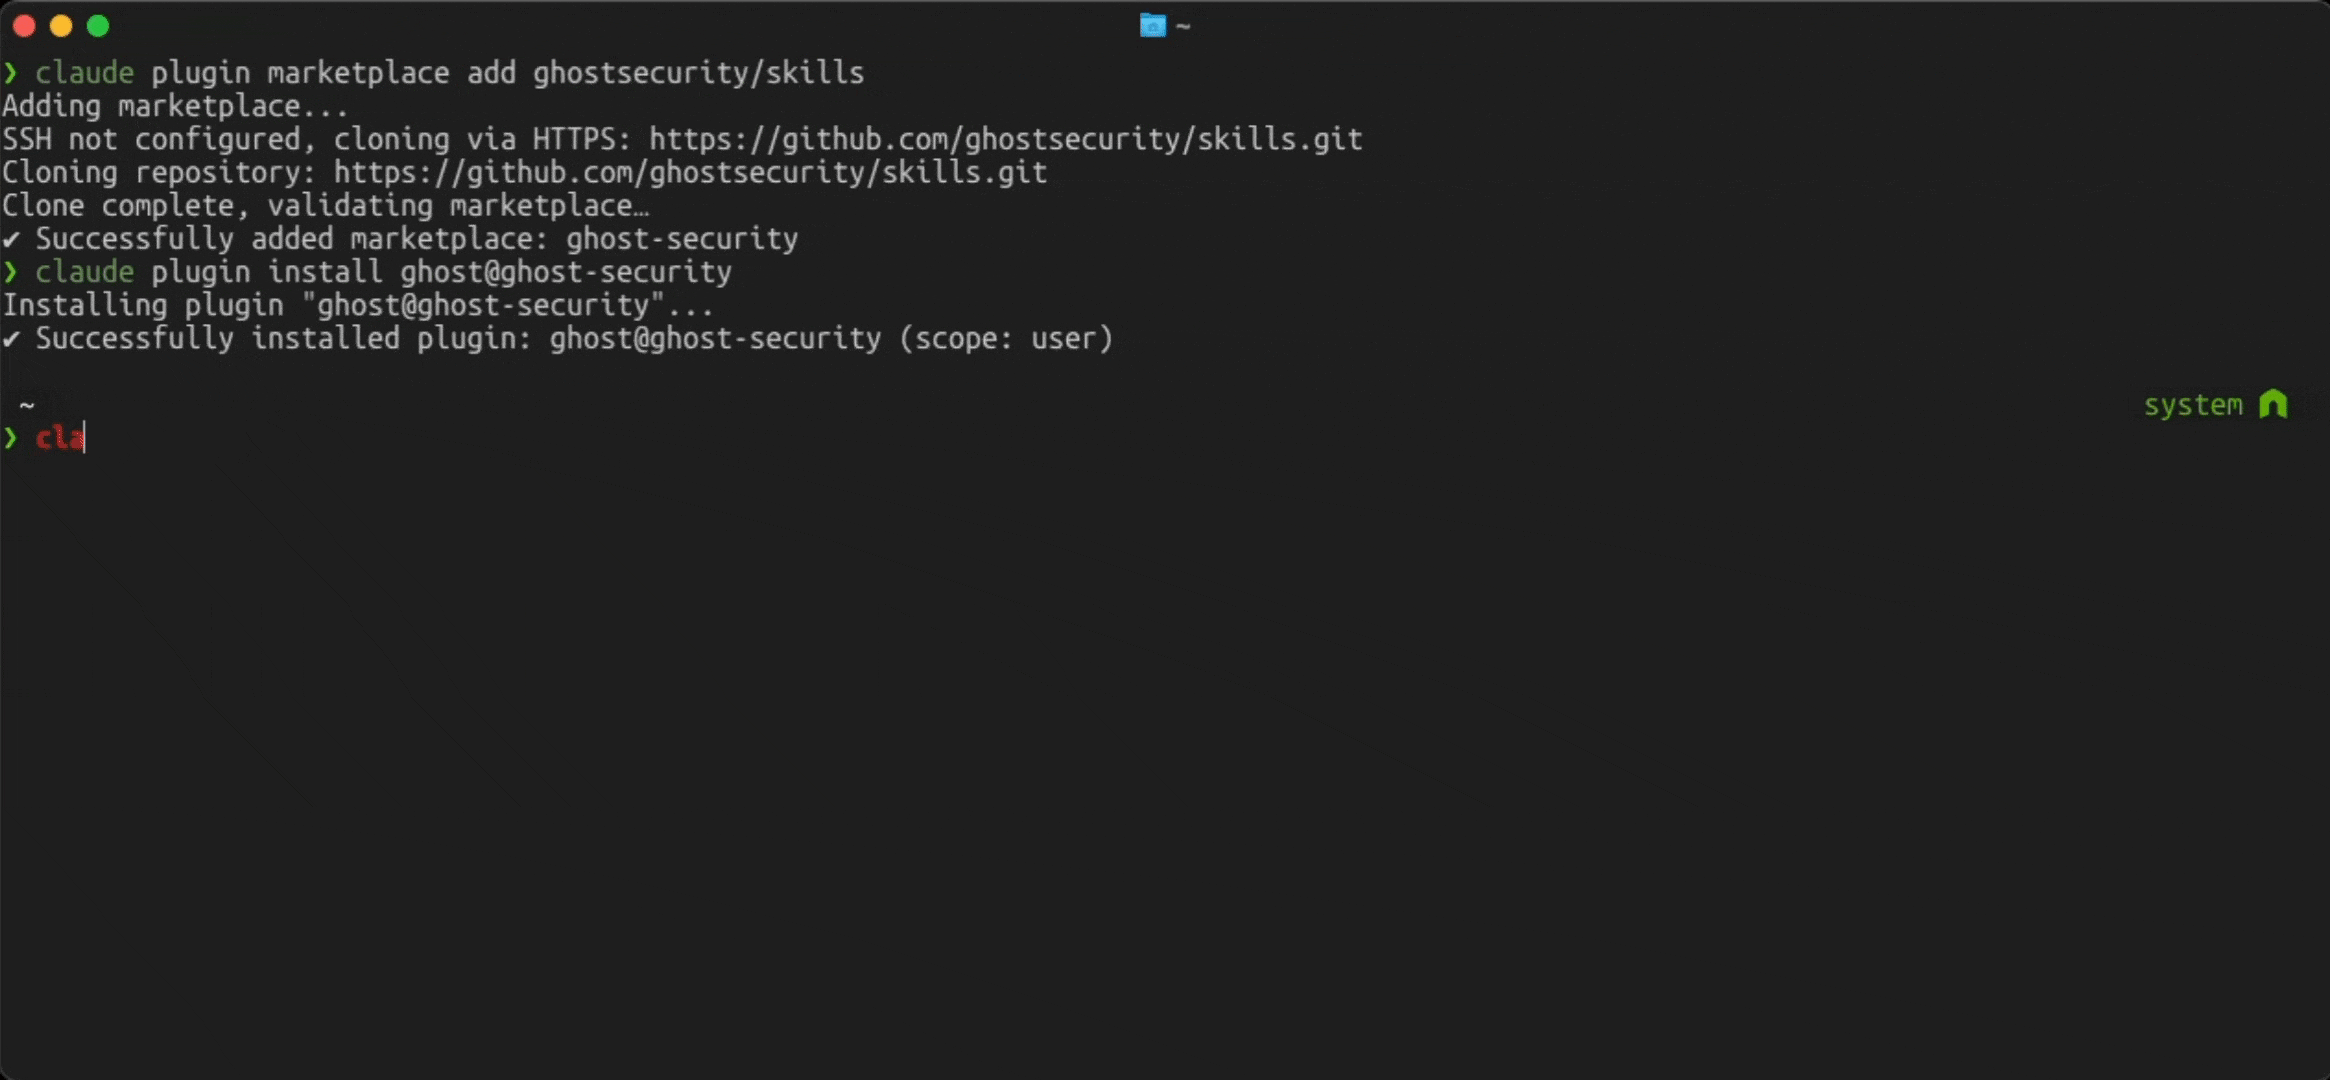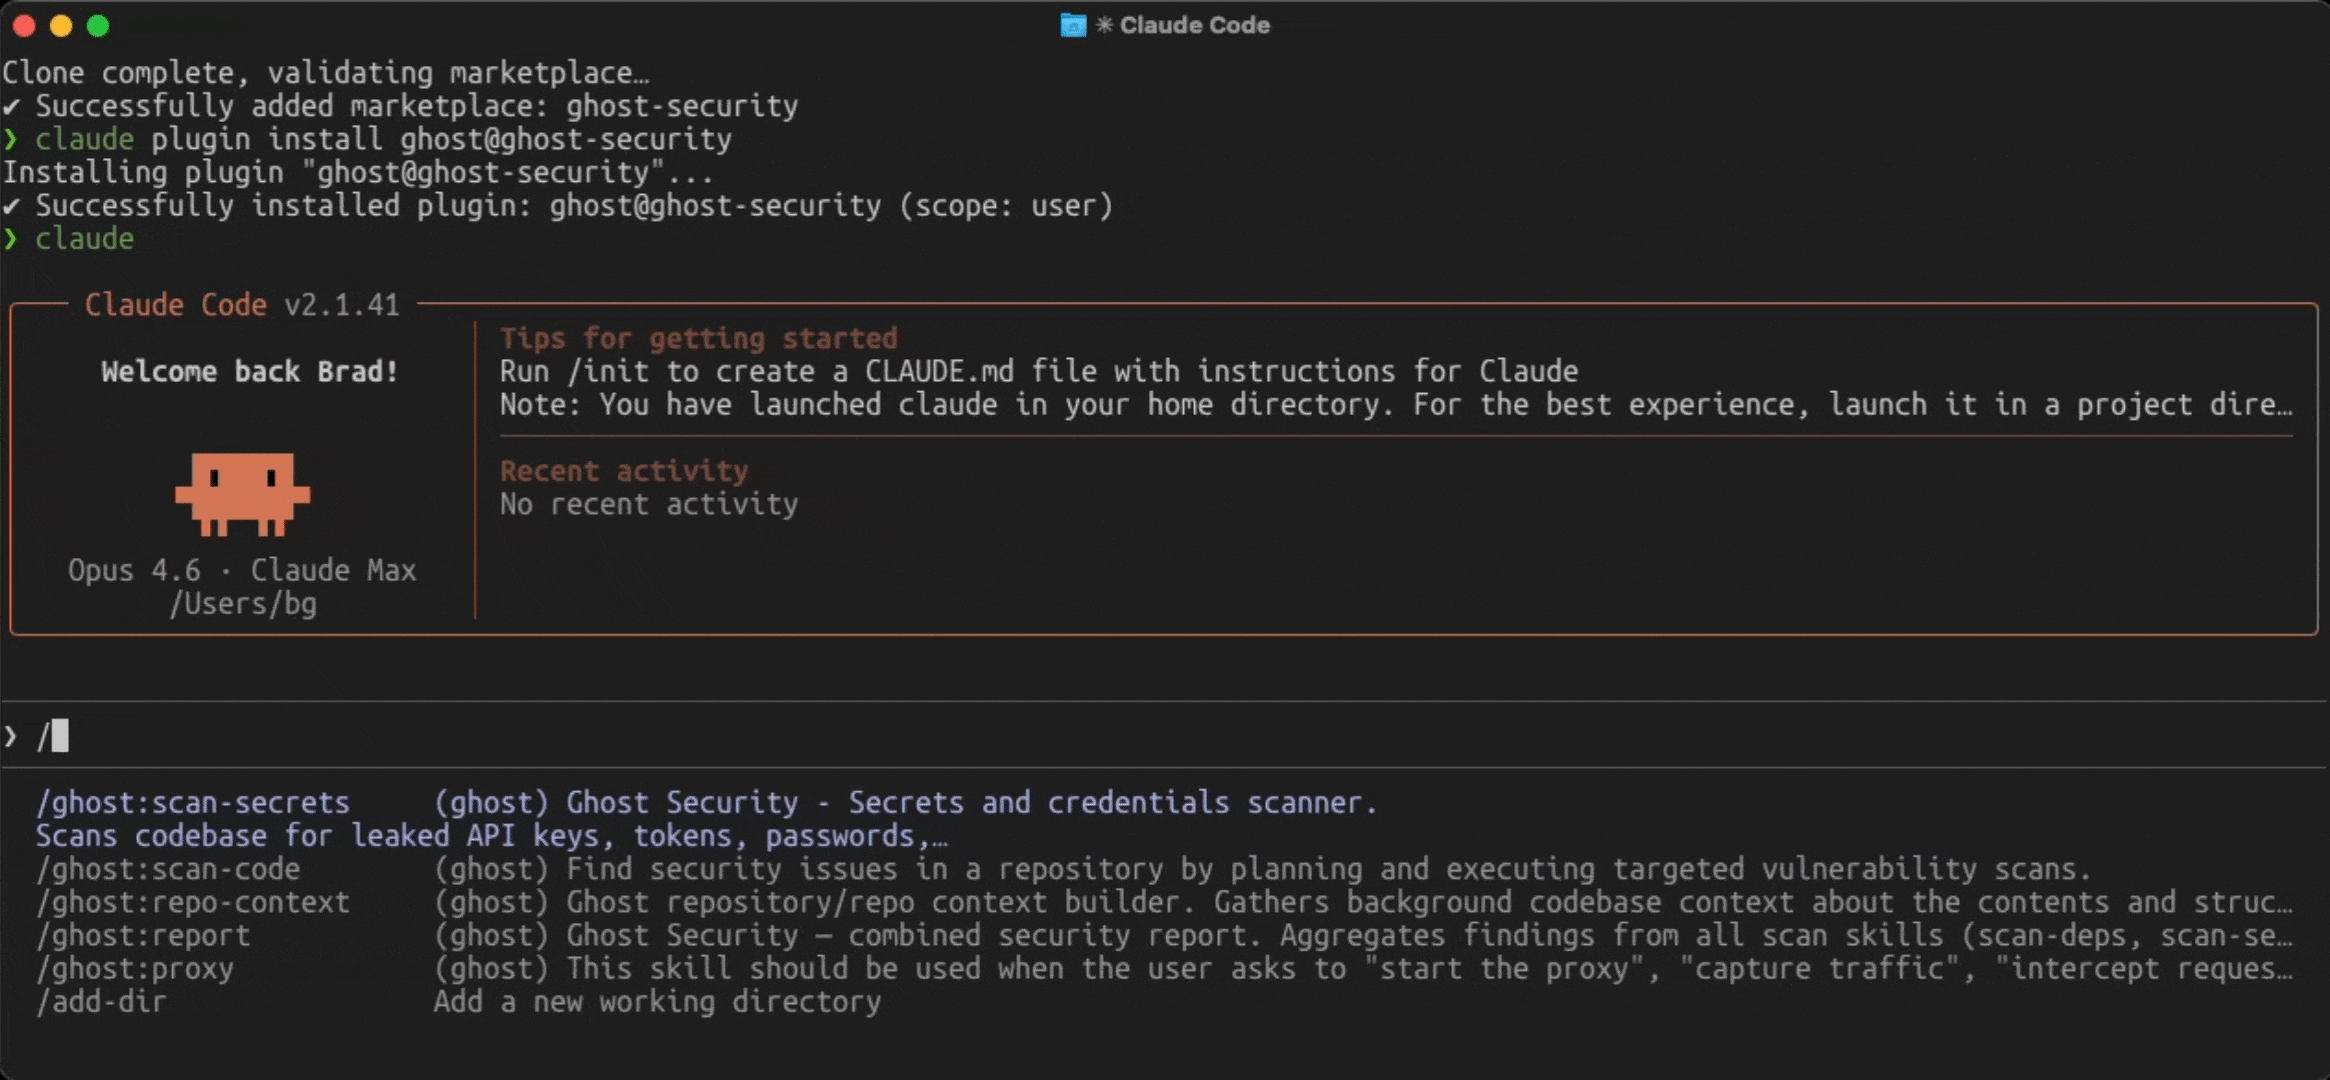
This repository is the Ghost Security plugin marketplace for Claude Code. It ships two plugins: Ghost Security AppSec Skills (ghost) and Ghost Security Exo (exo).
With Claude Code:
claude plugin marketplace add ghostsecurity/skills
claude plugin install ghost@ghost-security
claude plugin install exo@ghost-security
claude
Alternatively, install the plugins within Claude Code:
/plugin marketplace add ghostsecurity/skills
/plugin install ghost@ghost-security
/plugin install exo@ghost-security
Install only the plugins you need. If the install summary asks for it, run /reload-plugins to activate the plugin.
See Installation and usage for loading the plugins without installing them, where data is stored, and updating.
Ghost Security AppSec Skills are an agent-native application security plugin for Claude Code. They give your AI coding agent the tools and skills to find vulnerabilities, prove they're real, and fix them, all inside your existing development workflow.
| Tool | What it does |
|---|---|
| Poltergeist | Secret scanner with dual-engine pattern matching and entropy analysis. |
| Wraith | Dependency scanner powered by the OSV database. |
| Reaper | MITM HTTPS proxy for live vulnerability validation. |
| Exorcist | AI-powered code analysis covering 102 vulnerability types. |
These four tools are composed by an AI skills layer that orchestrates them into a complete security pipeline, from discovery to proof to fix. Get started with the installation and usage guide.
| Skill | Description |
|---|---|
ghost-repo-context | Build shared repository context (business criticality, sensitive data, component map) |
ghost-scan-deps | Exploitability analysis of dependency vulnerabilities (SCA) |
ghost-scan-secrets | Context assessment of detected secrets and credentials |
ghost-scan-code | AI-powered detection of code security issues (SAST) |
ghost-report | Combined security report across all scan results |
ghost-validate | Dynamic validation of findings against a live application (DAST) |
ghost-proxy | HTTP proxy for the ghost-validate skill |
Ghost Security AppSec Skills are built on a simple idea: real tools produce real data, and AI adds judgment on top.
Poltergeist, Wraith, and Reaper are standalone binaries that each do one job well. Poltergeist scans for secrets. Wraith scans dependencies. Reaper captures live traffic. These are deterministic tools that produce structured, reliable output.
The AI layer comes in through AI skills, orchestration prompts that compose these tools with reasoning. A skill runs Poltergeist, reads the results, examines the surrounding code, and tells you whether each match is a real leaked credential or a benign artifact that can be ignored.
This two-layer architecture means:
Ghost Security AppSec Skills follow a three-stage loop: find, validate, fix. Scanners find candidates, AI analyzes each candidate for exploitability, and findings include remediation guidance your agent can apply directly. Read more about how the scan lifecycle works.
Ghost Security AppSec Skills and their underlying tools are fully open source. Everything is available for inspection and contribution.
The tools can also be used standalone. You can use Poltergeist for secret scanning without touching the rest of the skills. The skills compose them into a pipeline, but the pipeline is optional. Use as much or as little as your workflow needs.
The ghost-exo skill builds, improves, and debugs workflows on exo, an agent orchestration platform. It routes each request to one of three intents: build, improve, or debug. See Ghost Security Exo for connecting the exo MCP server and using each intent.
Getting started
How it works
Capabilities
Tools
Community
Ghost Security Exo
Open an Issue per the Contributing guidelines and Code of Conduct
This repository is licensed under the Apache License 2.0. See LICENSE for details.
Stars on GitHub
Reverse engineer anything with agents, from app behavior down to native binaries.
@morlutoA skill pack for authorized reverse engineering, security research, and penetration testing that routes tasks to the right skill and sets up needed tools on demand. It covers API security assessment and Android APK analysis, among others.
 @zhaoxuya520
Gives an AI agent the step-by-step workflow a senior security analyst follows, covering when to use each technique, what to check first, how to run it and how to verify the result. Covers incident response, forensics, threat intelligence, malware analysis, penetration testing and red teaming.
 @mukul975
Agent skill + stdlib Python service to strip multi-vendor AI provenance marks from text and files, for privacy and hygiene on content you own. The skill is a thin client: it drives the machinery over HTTP, so the agent host needs no Python.
 @guillaumemeyer
Install it once and the right skill fires as you prompt, with no slash command to remember. It is listed on Flowy in the Security category. It includes exo, proxy, repo-context. Free and open source.
Is this plugin yours?
Claim it with GitHubSubmit a pluginPromote it