


rea
Reverse engineer anything with agents, from app behavior down to native binaries.
420k
 @morluto
A multi-agent code audit plugin that scans for security vulnerabilities, logic errors, and runtime bugs, then applies minimal fixes on a separate branch. It also reviews commit diffs and maps trust boundaries for threat modeling.
Claude Code
$ npx -y skills add codexstar69/bug-hunter --agent claude-code
Codex
$ npx skills add codexstar69/bug-hunter -a codex
Cursor
$ npx skills add codexstar69/bug-hunter -a cursor
Gemini CLI
$ npx skills add codexstar69/bug-hunter -a gemini-cli
GitHub Copilot
$ npx skills add codexstar69/bug-hunter -a github-copilot
OpenCode
$ npx skills add codexstar69/bug-hunter -a opencode
Windsurf
$ npx skills add codexstar69/bug-hunter -a windsurf
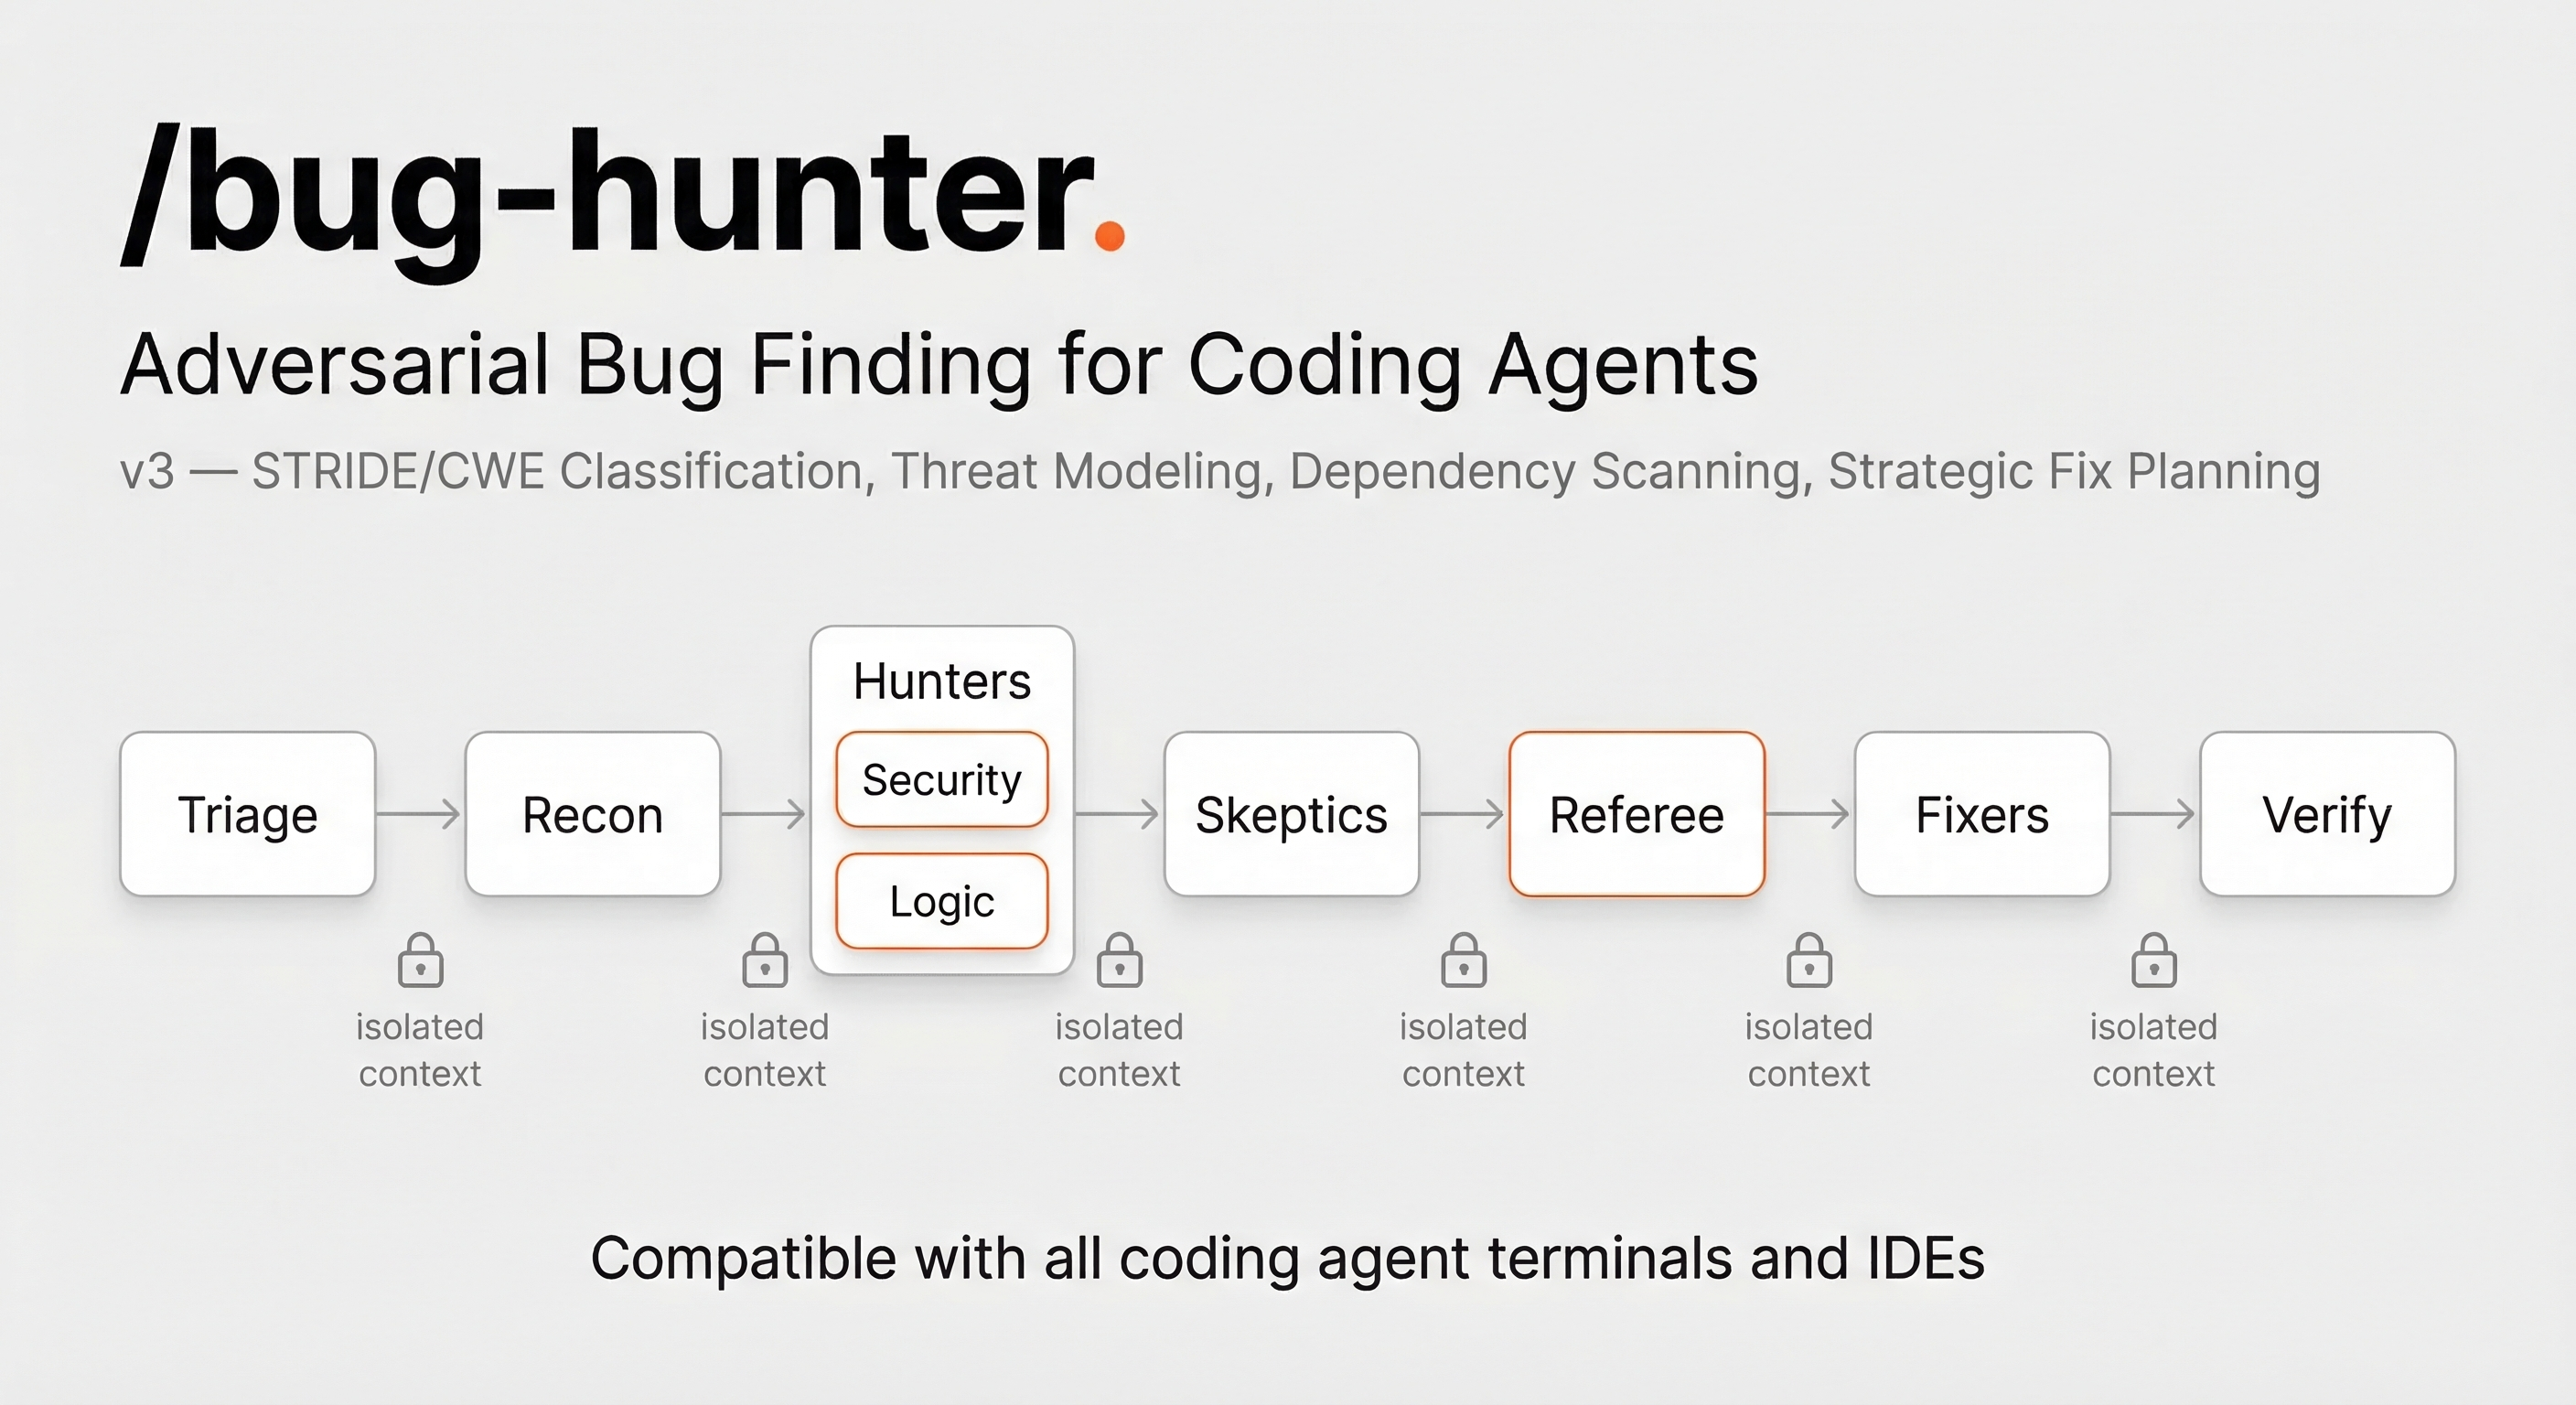
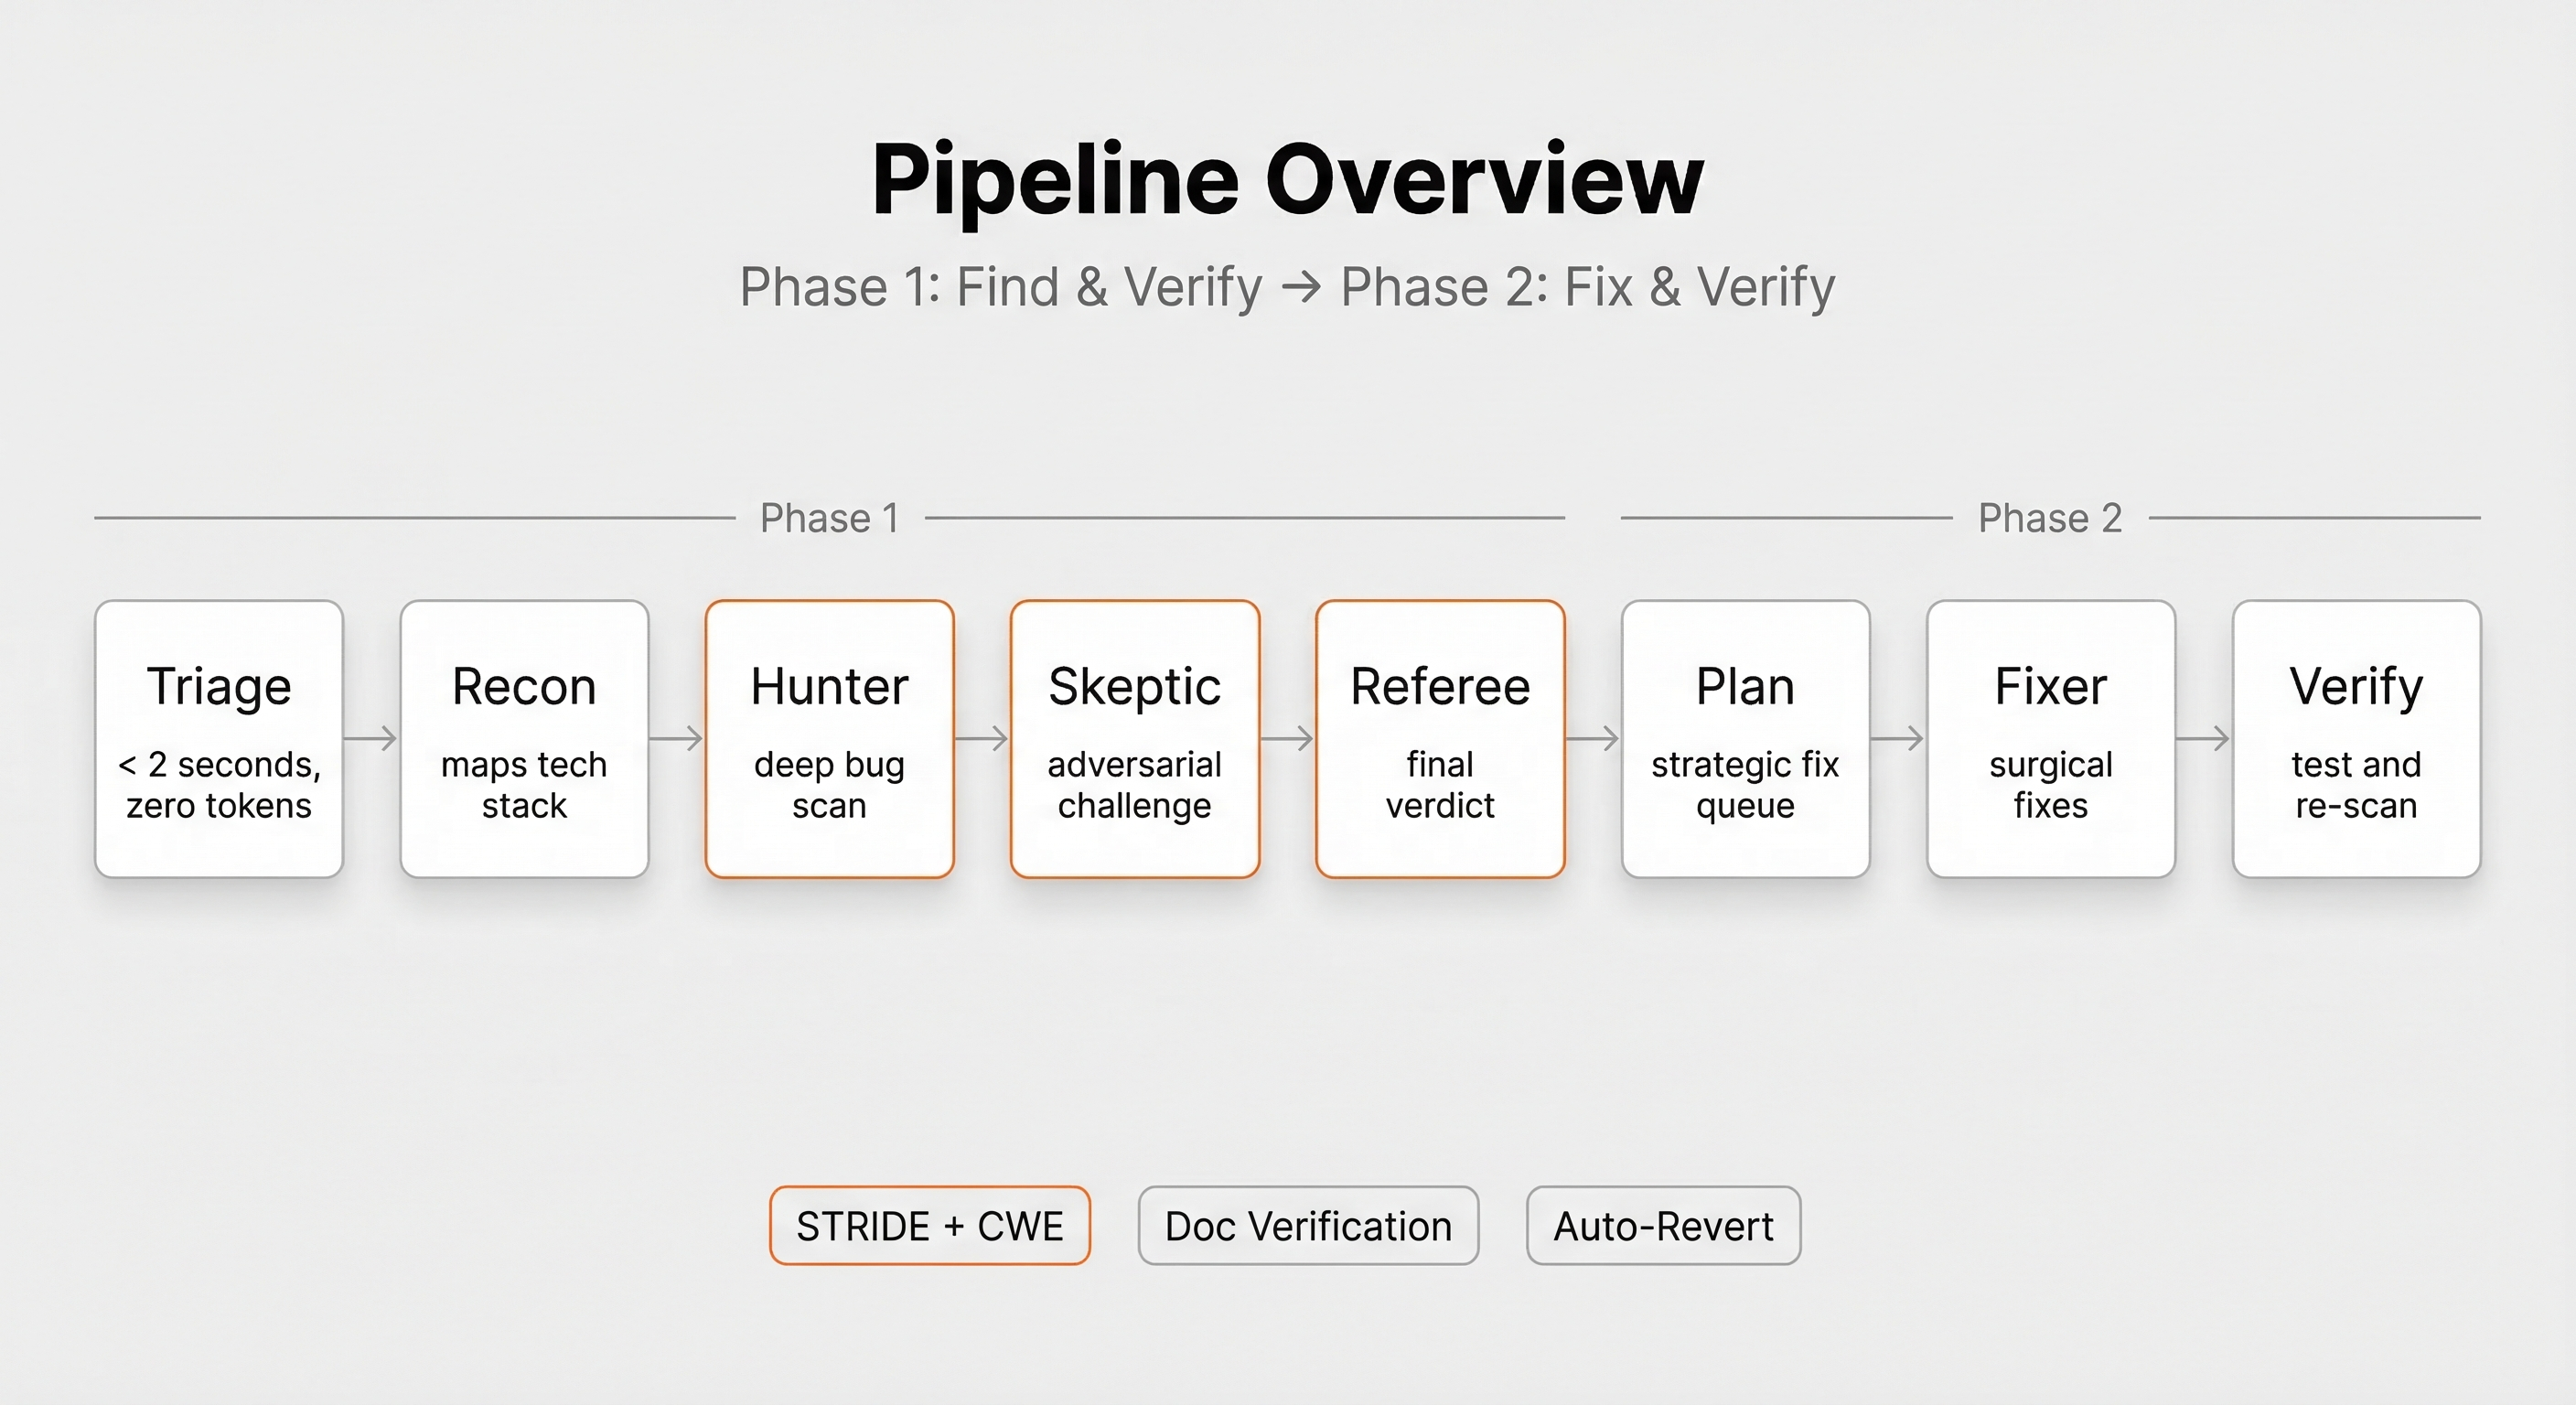

Bug Hunter is an AI-agent skill for code review and security auditing. A Hunter finds possible bugs, a Skeptic challenges each claim, and a Referee decides what the evidence supports. The default run only scans and reports. It is single-pass unless --loop is explicitly requested. Editing, autonomous fixing, and commits each require explicit permission.
The current v3.2.0 source makes the precision-first pipeline measurable and adaptive while preserving the scan-only default and fail-closed safety boundaries. The latest published npm release may lag GitHub main; use the current-source command below when you need the exact implementation documented on this page.
fast, balanced, or assurance behavior from triage risk, security scope, benchmark evidence, stability, calibration, and token efficiency.The bundled deterministic regression fixture currently records precision 1.00, recall 1.00, F1 1.00, repeat stability 1.00, zero false positives, median 12,090 tokens per true positive, p95 duration 61.3s, and expected calibration error about 0.048. These figures validate the bundled harness and fixture; they are not an independent benchmark of every repository or model.
See the measurable world-class protocol for the full architecture, artifact contracts, quality thresholds, and verification design.
Install the exact current GitHub source documented here. Replace codex with a target from the table below.
npx --yes https://github.com/codexstar69/bug-hunter/archive/refs/heads/main.tar.gz install --agent codex
npx --yes https://github.com/codexstar69/bug-hunter/archive/refs/heads/main.tar.gz doctor --agent codex
For the latest published npm release—which may lag current GitHub source—use:
npm exec --yes --package=@codexstar/bug-hunter@latest -- bug-hunter install --agent codex
npm exec --yes --package=@codexstar/bug-hunter@latest -- bug-hunter doctor --agent codex
Restart the agent if it was open during installation. Then send this prompt from the repository you want to audit:
Use the bug-hunter skill to scan this repository. Do not edit files.
Return the final report and call out every item that needs manual review.
That is the recommended first run. It is scan-only and single-pass. Request --loop when complete queued coverage is required.
| Agent | Install target |
|---|---|
| Claude Code | claude-code |
| Codex | codex |
| Cursor | cursor |
| GitHub Copilot | copilot |
| Kiro | kiro |
| Windsurf | windsurf |
| OpenCode | opencode |
| Factory Droid CLI | droid |
| Other file-based agents | agents |
Always pass --agent when more than one coding agent is installed. Auto-detection is available, but an explicit target prevents installation into the wrong skill directory.
Factory Droid CLI (droid) installs into ~/.factory/skills/bug-hunter and loads the skill for every repository. Use --path "$PWD/.factory/skills/bug-hunter" instead when the skill should be checked into a single repository. Droid also reads the legacy ~/.agents/skills location, so an existing --agent agents install already works there.
See agent installation for paths, source installs, updates, removal, and custom targets.
Natural language is the portable interface:
Use the bug-hunter skill to scan src/auth. Do not edit files.
Agents that expose skill commands may also accept:
/bug-hunter src/auth
For a reviewed fix run:
Use the bug-hunter skill to scan this repository. Build a fix plan.
Ask for approval before every edit. Do not commit.
The closest flag-based mode is:
/bug-hunter --fix --approve
--approve requests the host agent's reviewed/default permission mode. The
host decides when approval prompts appear. Use --plan or --preview when
source edits must be impossible.
For a plan without edits:
/bug-hunter --plan
Do not use --autonomous or --auto-commit unless you intend to grant those permissions.
See usage guide for common human and agent prompts.
your code
  -> risk triage
  -> optional adaptive plan
  -> architecture recon
  -> hypothesis-driven retrieval
  -> Hunter findings
  -> documentation checks
  -> Skeptic challenges
  -> Referee verdicts
  -> optional hybrid verification
  -> report
  -> optional approved fix plan
  -> optional approved fixes and verification
The pipeline:
Read how it works for the full model and safety boundaries.
| Goal | Skill request |
|---|---|
| Scan the whole repository once | /bug-hunter |
| Complete queued coverage | /bug-hunter --loop |
| Scan one path | /bug-hunter src/auth |
| Review staged changes | /bug-hunter --staged |
| Review the current pull request | /bug-hunter --pr |
| Run a pull-request security review | /bug-hunter --pr-security |
| Add Node.js dependency scanning | /bug-hunter --deps |
| Generate a STRIDE threat model | /bug-hunter --threat-model |
| Create a fix plan without edits | /bug-hunter --plan |
| Request host-interactive fixing | /bug-hunter --fix --approve |
| Build a no-edit remediation preview | /bug-hunter --preview |
| Allow unattended fixing | /bug-hunter --autonomous |
The executable bug-hunter command installs and verifies the skill. Scans are started through your coding agent, not by running bug-hunter scan in a shell.
See CLI reference for installer commands and skill arguments.
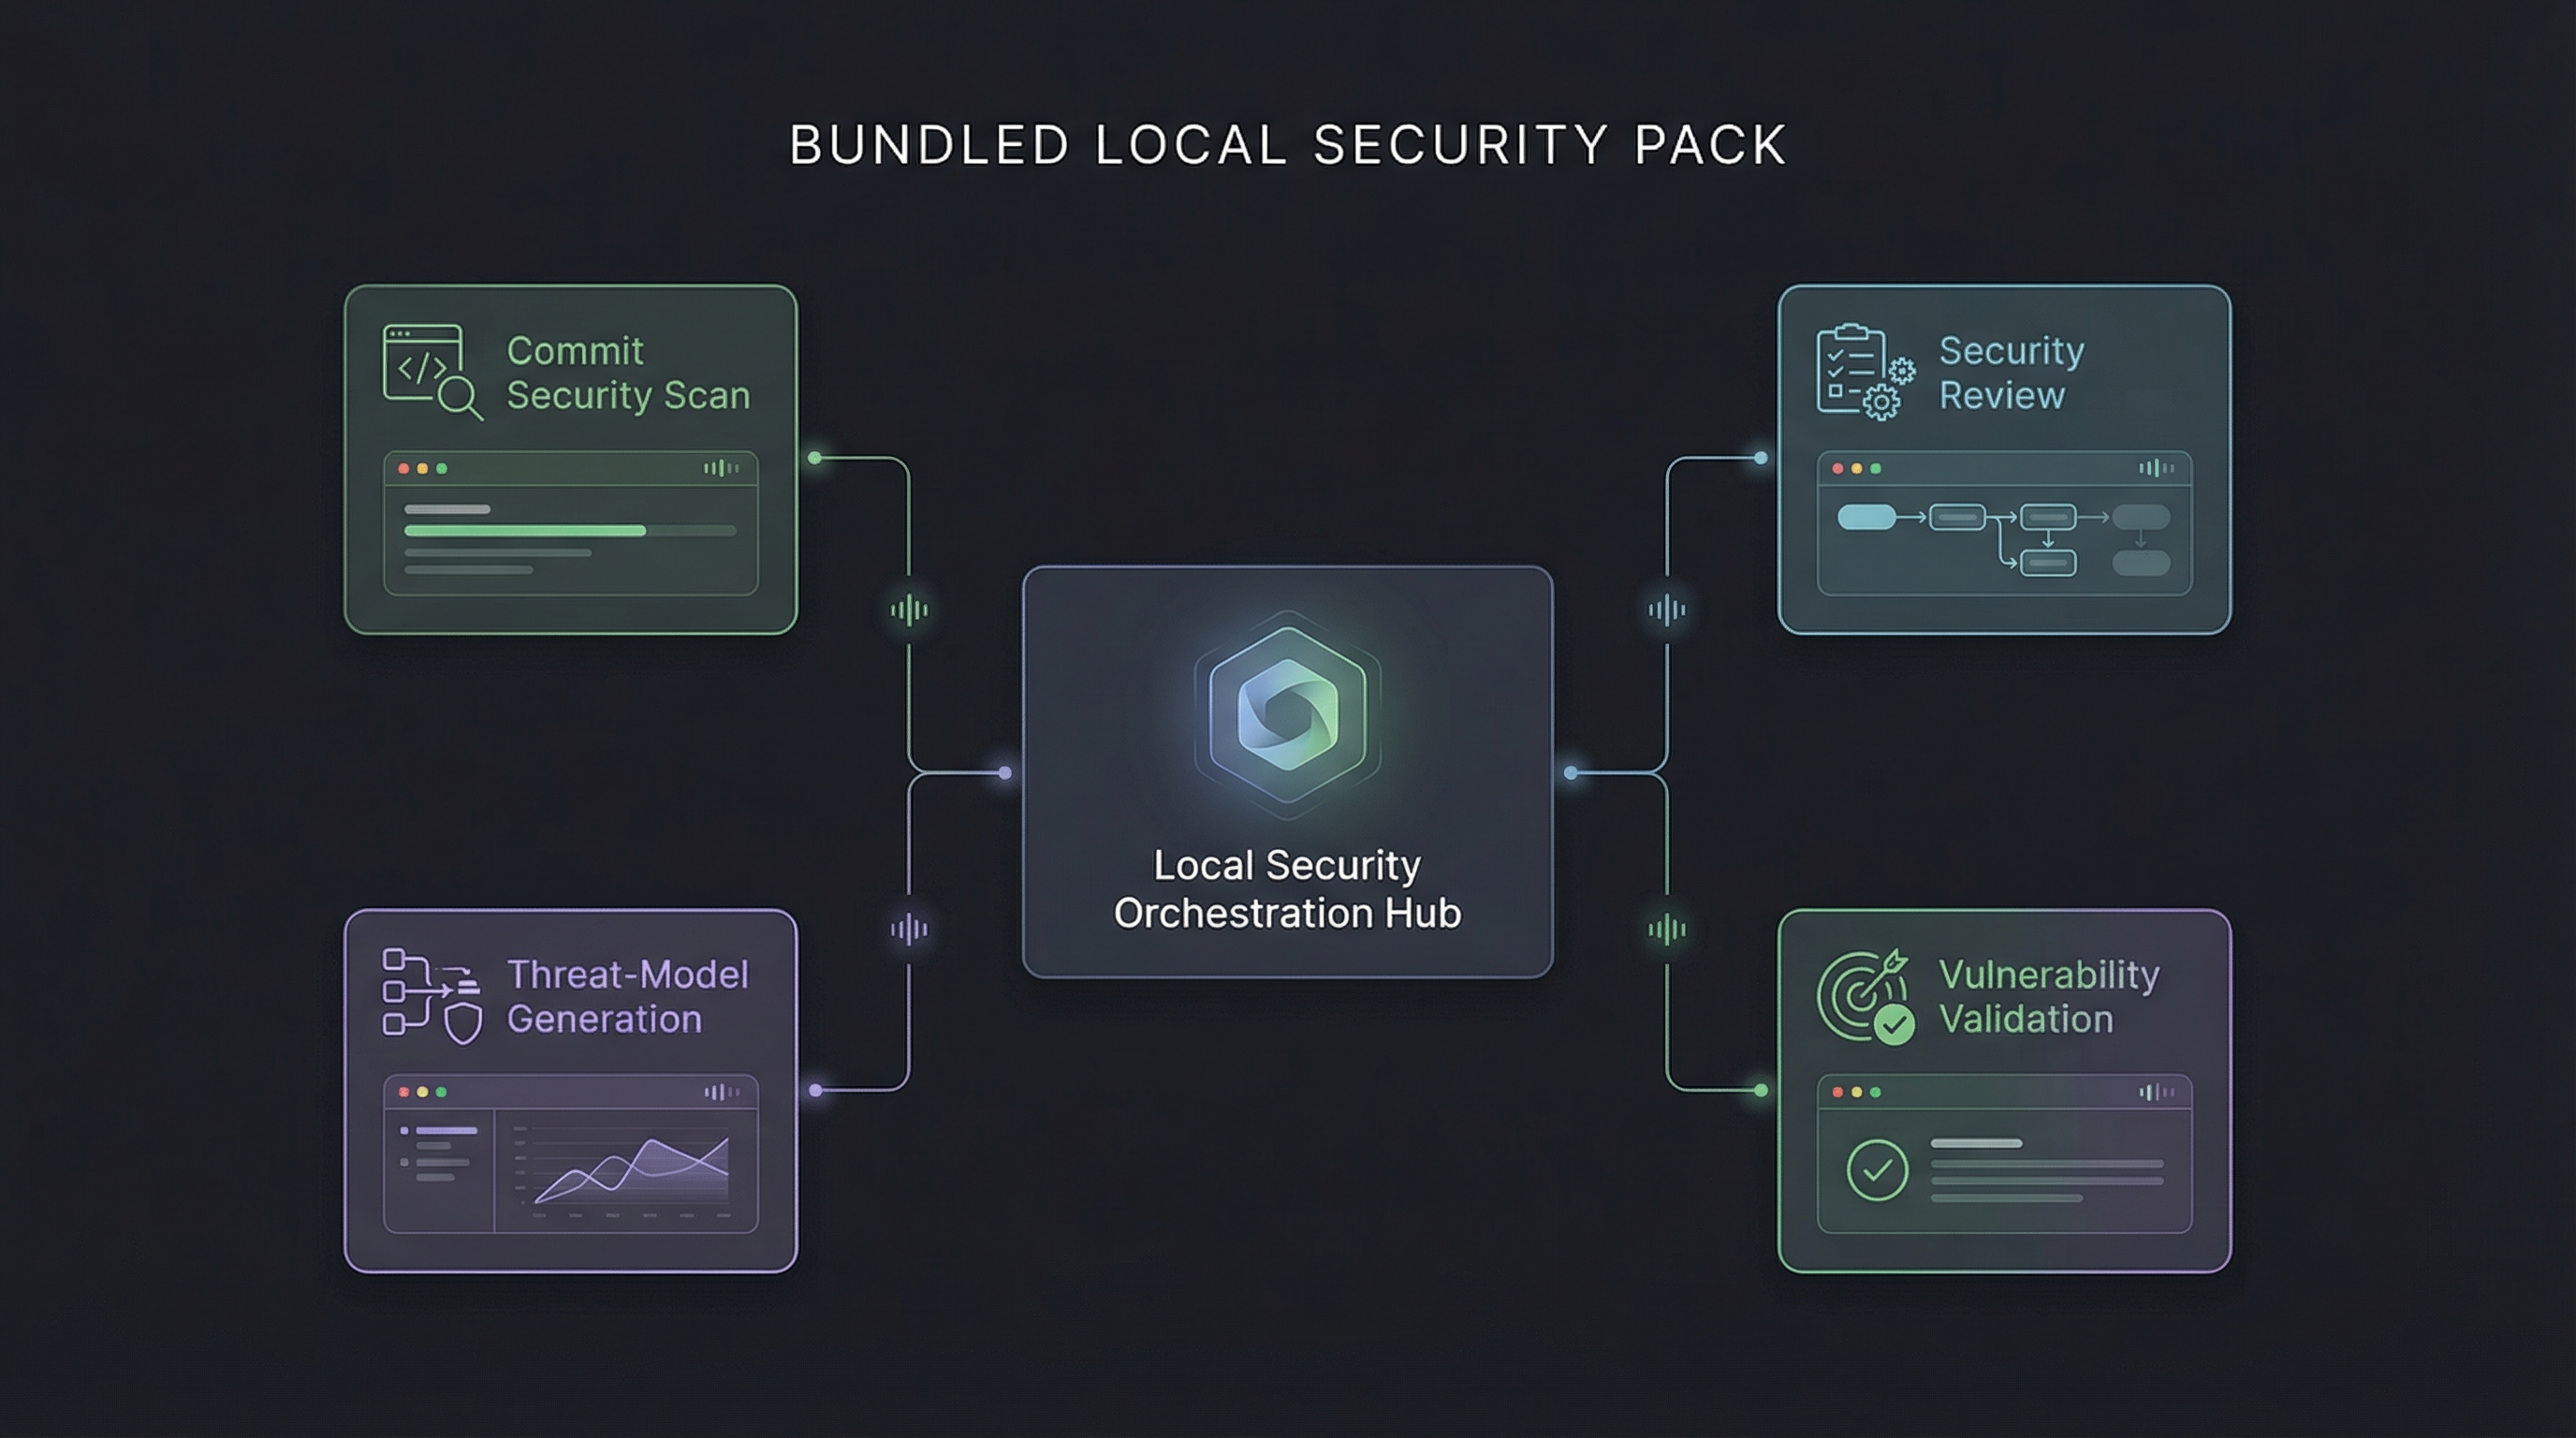
The security flags use bundled local skills:
commit-security-scan through
--pr-security.--threat-model routes into threat-model-generation.security-review through
--security-review.--validate-security routes into vulnerability-validation.These skills are part of the managed runtime. They do not require separate installation.
Many AI code-review tools produce a long list of possible issues but leave the developer to discover which claims are real. A plausible explanation is not proof that a runtime bug is reachable. Framework behavior, middleware, validation in another file, and language guarantees can turn an alarming finding into a false positive.
Bug Hunter treats a finding as a claim that must survive opposition:
For teams comparing an AI code-review tool, security code scanner, vulnerability scanner, or static-analysis assistant, this separation matters: automated code review stays useful only when the evidence and uncertainty are visible.
This adversarial code review is designed to reduce false-positive overload
Stars on GitHub
Reverse engineer anything with agents, from app behavior down to native binaries.
@morlutoA skill pack for authorized reverse engineering, security research, and penetration testing that routes tasks to the right skill and sets up needed tools on demand. It covers API security assessment and Android APK analysis, among others.
 @zhaoxuya520
Gives an AI agent the step-by-step workflow a senior security analyst follows, covering when to use each technique, what to check first, how to run it and how to verify the result. Covers incident response, forensics, threat intelligence, malware analysis, penetration testing and red teaming.
 @mukul975
Agent skill + stdlib Python service to strip multi-vendor AI provenance marks from text and files, for privacy and hygiene on content you own. The skill is a thin client: it drives the machinery over HTTP, so the agent host needs no Python.
 @guillaumemeyer
Install it with the command on its page. It includes commit-security-scan, doc-lookup, fixer. Its skills do not fire on their own yet. Free and open source.
Is this plugin yours?
Claim it with GitHubSubmit a pluginPromote it