
council
Runs structured deliberation across several reasoning perspectives, so a user can weigh a hard decision from multiple angles before settling on one path.
1 skill18 agents4.8k
 @0xnyk
Adds policy and safety controls to coding agents like Claude Code: approval gates, pretool guards that block destructive commands, quality scoring on session stop, structured work modes, and execution records with rollback.
Claude Code
> /plugin marketplace add 0xNyk/lacp> /plugin install lacp-hardening@lacp-plugins
Codex
$ npx skills add 0xNyk/lacp -a codex
Cursor
$ npx skills add 0xNyk/lacp -a cursor
Gemini CLI
$ npx skills add 0xNyk/lacp -a gemini-cli
GitHub Copilot
$ copilot plugin marketplace add 0xNyk/lacp$ copilot plugin install lacp-hardening@lacp-plugins
OpenCode
$ npx skills add 0xNyk/lacp -a opencode
Windsurf
$ npx skills add 0xNyk/lacp -a windsurf
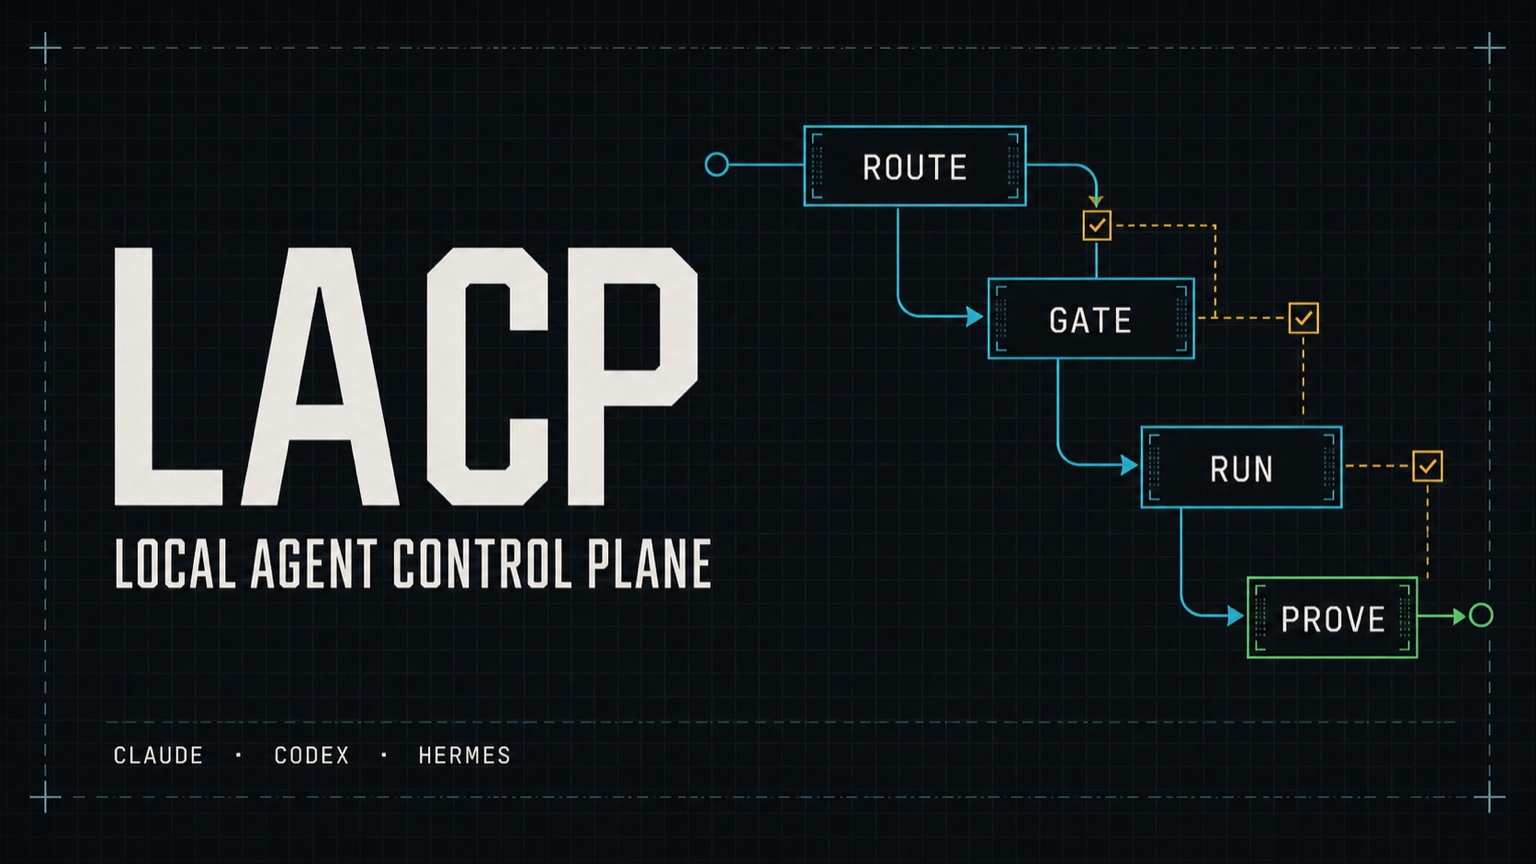
Local policy, evidence, and recovery controls for coding agents.
LACP wraps Claude, Codex, Hermes, and other CLI agents with deterministic routing, approval gates, execution records, memory controls, and rollback paths. It runs on your machine and keeps remote execution opt-in.



Development status:
mainand the GitHub release are v0.10.1. Homebrew's last bottled release may lag until the tap is updated;brew install --HEADtracksmain. Git worktrees isolate files, not ports — see Runtime isolation.
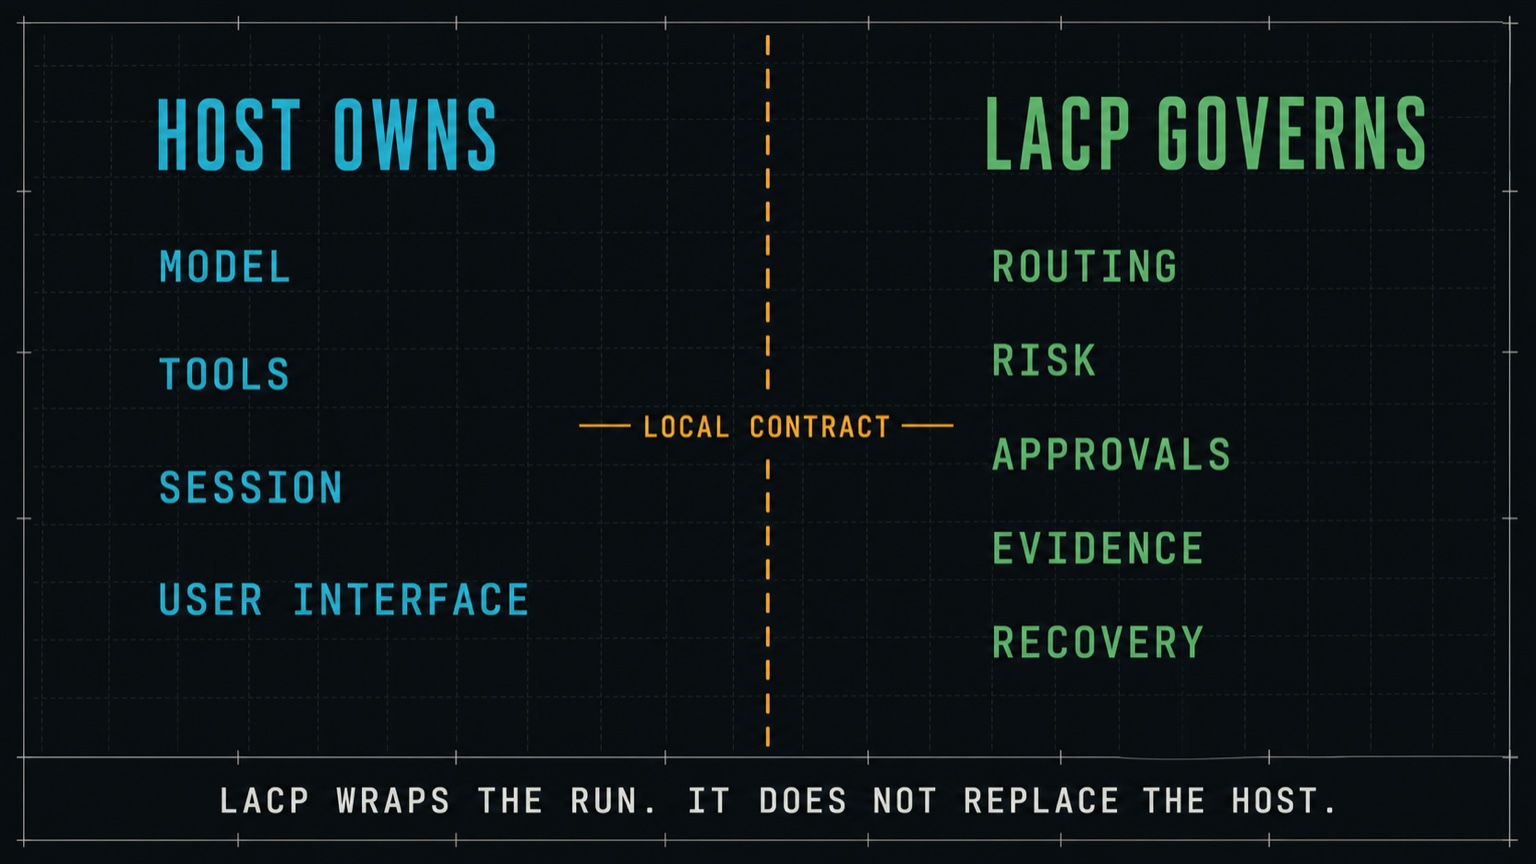
LACP is a local execution wrapper and control plane. The coding-agent host still owns its model, tools, session, and interface. LACP owns the contract around a run: where it may execute, which risk tier applies, when approval is required, what evidence must be kept, and how a failed change is recovered.
# Homebrew (recommended)
brew tap 0xNyk/lacp && brew install lacp

# or inspect and run the bootstrap at a published tag
curl -fsSLo /tmp/lacp-install.sh \
  https://raw.githubusercontent.com/0xNyk/lacp/v0.10.1/install.sh
LACP_REF=v0.10.1 bash /tmp/lacp-install.sh
lacp bootstrap-system --profile starter --with-verify
lacp doctor --json | jq '.ok,.summary'
After bootstrap: .env is created, dependencies installed, directories scaffolded, Obsidian vault wired, and verification artifacts produced.
For the full setup and daily operator flow, start with the Runbook and Local Dev Loop.
# Route a task through LACP policy gates
lacp run --task "hello world" --repo-trust trusted -- echo "LACP is working"

# Make claude/codex/hermes default to LACP routing (reversible)
lacp adopt-local --json | jq
lacp bootstrap-system --profile starter --with-verify
lacp adopt-local --json | jq   # wraps claude + codex only; Hermes stays native
lacp posture --strict
lacp run \
  --task "dependency update with tests" \
  --repo-trust trusted \
  --context-profile default \
  -- pnpm up && pnpm test
lacp e2e smoke --workdir . --init-template --command "npx playwright test --grep @smoke"
lacp api-e2e smoke --workdir . --init-template --command "npx schemathesis run --checks all"
lacp pr-preflight --changed-files ./changed-files.txt --checks-json ./checks.json
lacp worktree create --repo-root . --name feature-a --base HEAD
lacp up --session feature-a --instances 3 --command "claude"
lacp swarm launch --manifest ./swarm.json
| Guide | What You'll Learn |
|---|---|
| Runbook | Daily operator workflow, command map, troubleshooting entry points |
| Local Dev Loop | Fast build/test/verify loop for contributors |
| Framework Scope | What LACP is, what it is not, and design boundaries |
| Implementation Path | Step-by-step rollout plan for full control-plane adoption |
| Memory Quality Workflow | How memory ingestion, expansion, and validation are run safely |
| Incident Response | Triage and recovery flow when policy gates fail |
| Release Checklist | Pre-release, release, and post-release controls |
| Troubleshooting | Common errors, doctor diagnostics, fix hints |
| Runtime isolation | Worktrees vs ports vs Claude host isolation |
lacp/
├── bin/                    # CLI commands (lacp <command>)
│   ├── lacp                # Top-level dispatcher
│   ├── lacp-bootstrap-system
│   ├── lacp-doctor         # Diagnostics (--json, --fix-hints)
│   ├── lacp-route          # Policy-driven tier/provider routing
│   ├── lacp-sandbox-run    # Gated execution with artifact logging
│   ├── lacp-brain-*        # Memory stack (ingest, expand, doctor, stack)
│   ├── lacp-obsidian       # Vault config management
│   ├── lacp-up             # Multi-instance agent sessions
│   ├── lacp-swarm          # Batch orchestration
│   └── lacp-claude-hooks   # Hook profile management
├── config/
│   ├── sandbox-policy.json     # Routing + cost ceilings
│   ├── risk-policy-contract.json
│   ├── obsidian/               # Vault manifest + optimization profiles
│   └── harness/                # Task schemas, sandbox profiles, verification policies
├── hooks/                  # Python hook pipeline for Claude Code
├── scripts/
│   ├── ci/                 # Test suites
│   └── runners/            # Daytona/E2B execution adapters
└── docs/                   # Guides and reference docs
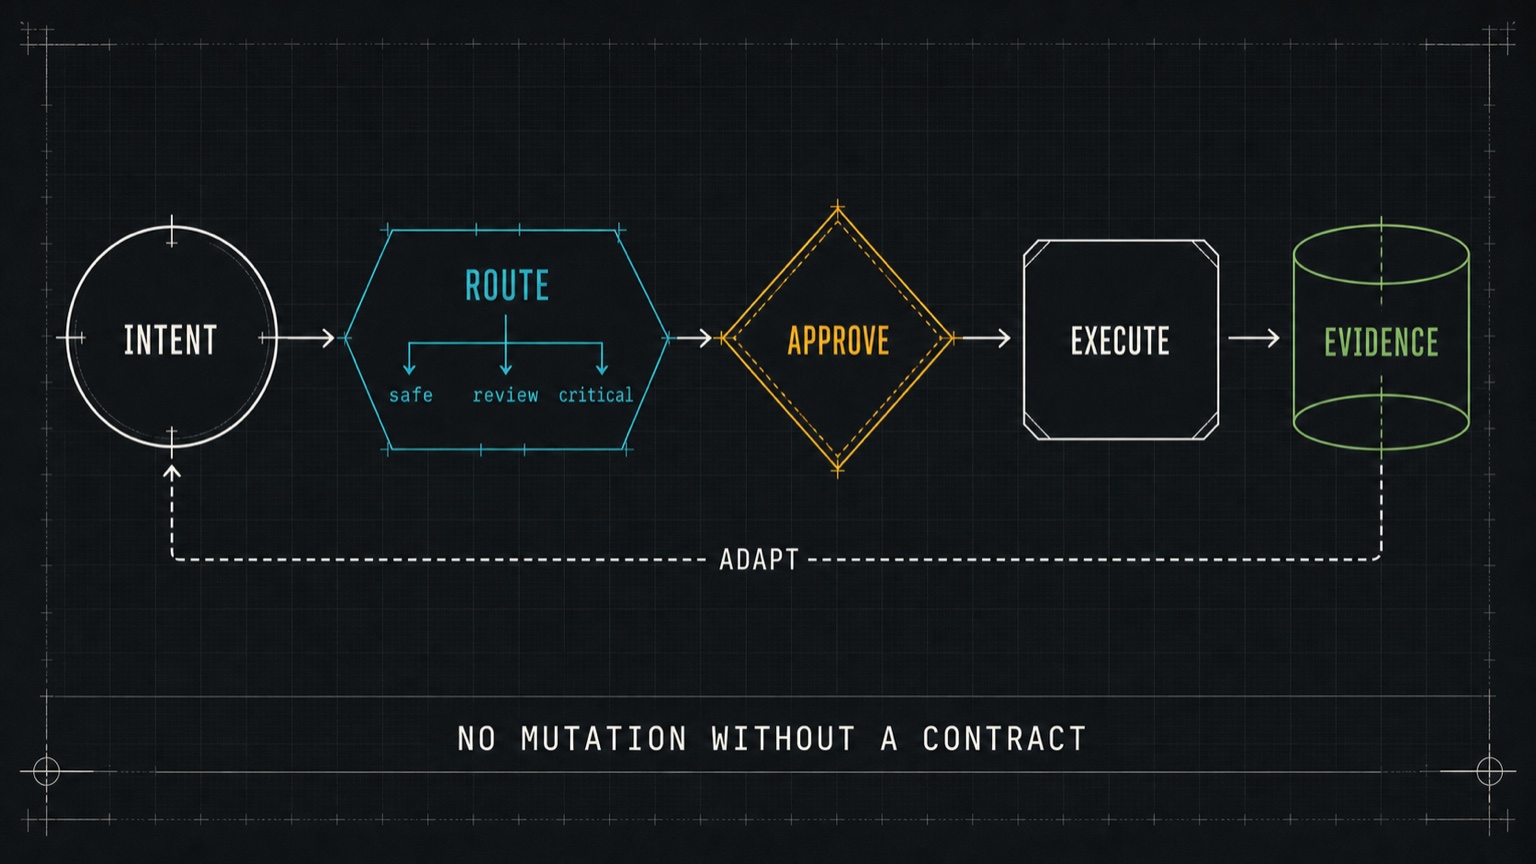
Agent invocation
  → lacp route (risk tier + provider selection)
    → context contract validation
      → budget gate check
        → session fingerprint verification
          → sandbox-run (dispatch + artifact logging)
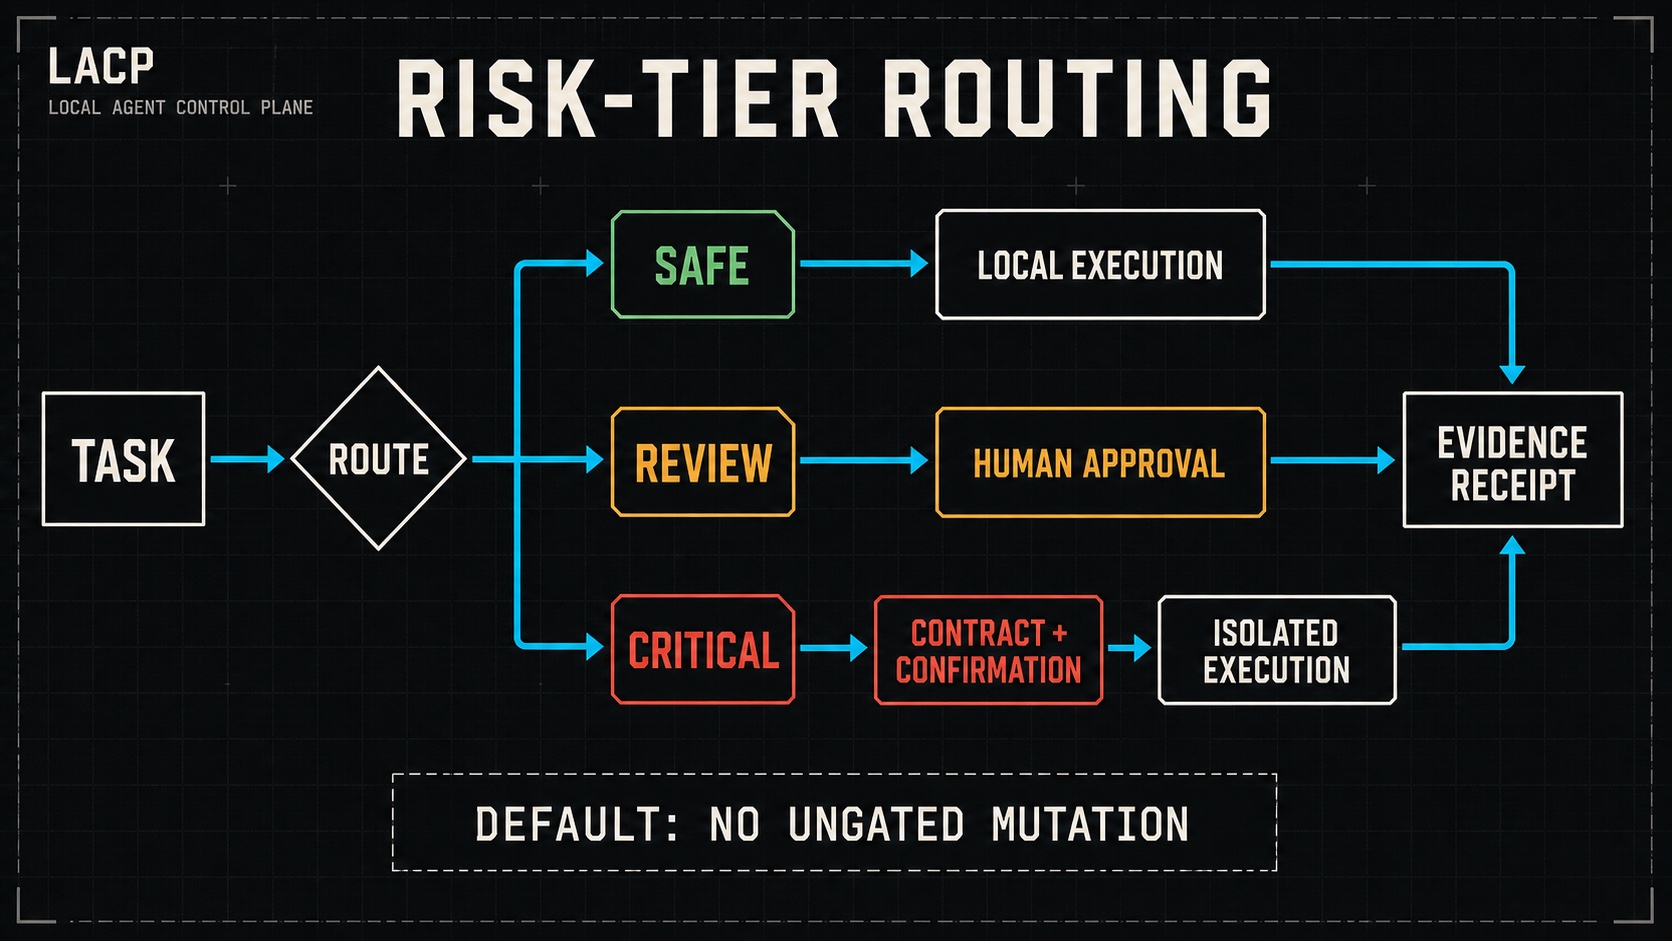
Every command routes through risk tiers (safe → review → critical), budget ceilings per tier, and context contracts that validate host, working directory, git branch, and remote targets before execution.
| Layer | Purpose |
|---|---|
| Session memory | Per-project scaffolding under ~/.claude/projects/ |
| Knowledge graph | Obsidian vault with MCP wiring (smart-connections, QMD, ori-mnemos) |
| Ingestion pipeline | brain-ingest converts text/audio/video/URLs into structured notes |
| Code intelligence | GitNexus AST-level knowledge graph via MCP (optional) |
| Agent identity | Persistent IDs per (hostname, project) + SHA-256 hash-chained provenance |
lacp brain-stack init --json | jq          # Bootstrap all layers
lacp brain-ingest --url "https://..." --apply --json | jq
lacp brain-expand --apply --json | jq      # Full expansion loop
Modular Python hooks enforcing quality at every session stage:
| Hook | Event | Purpose |
|---|---|---|
session_start.py | SessionStart | Git context injection, test command caching |
pretool_guard.py | PreToolUse | Block dangerous operations (publish, chmod 777, fork bombs, secrets) |
write_validate.py | PostToolUse | YAML frontmatter schema validation |
stop_quality_gate.py | Stop | 3-tier eval: heuristics, test verification, local LLM rationalization detection |
Profiles: minimal-stop, balanced, hardened-exec, quality-gate-v2. Apply with lacp claude-hooks apply-profile <profile>.
hardened-exec also logs SubagentStart / SubagentStop. It does not install a
WorktreeCreate hook (that event replaces Claude's git worktree creation).
Biologically-inspired memory consolidation modeled on fungal networks:
| Mechanism | Description |
|---|---|
| Adaptive path reinforcement | Frequently-traversed edges strengthen (like mycelium hyphae) |
| Self-healing | Pruned nodes trigger reconnection of orphaned neighbors |
| Exploratory tendrils | Frontier nodes in active categories shielded from pruning |
| Flow scoring | Betweenness centrality identifies critical knowledge hubs |
| Temporal decay | FSRS dual-strength model with forgetting curve |
# dmux-style multi-instance launch
lacp up --session dev --instances 3 --command "claude"

# Git worktree isolation
lacp worktree create --repo-root . --name "feature-a" --base HEAD

# Batch swarm execution
lacp swarm launch --manifest ./swarm.json
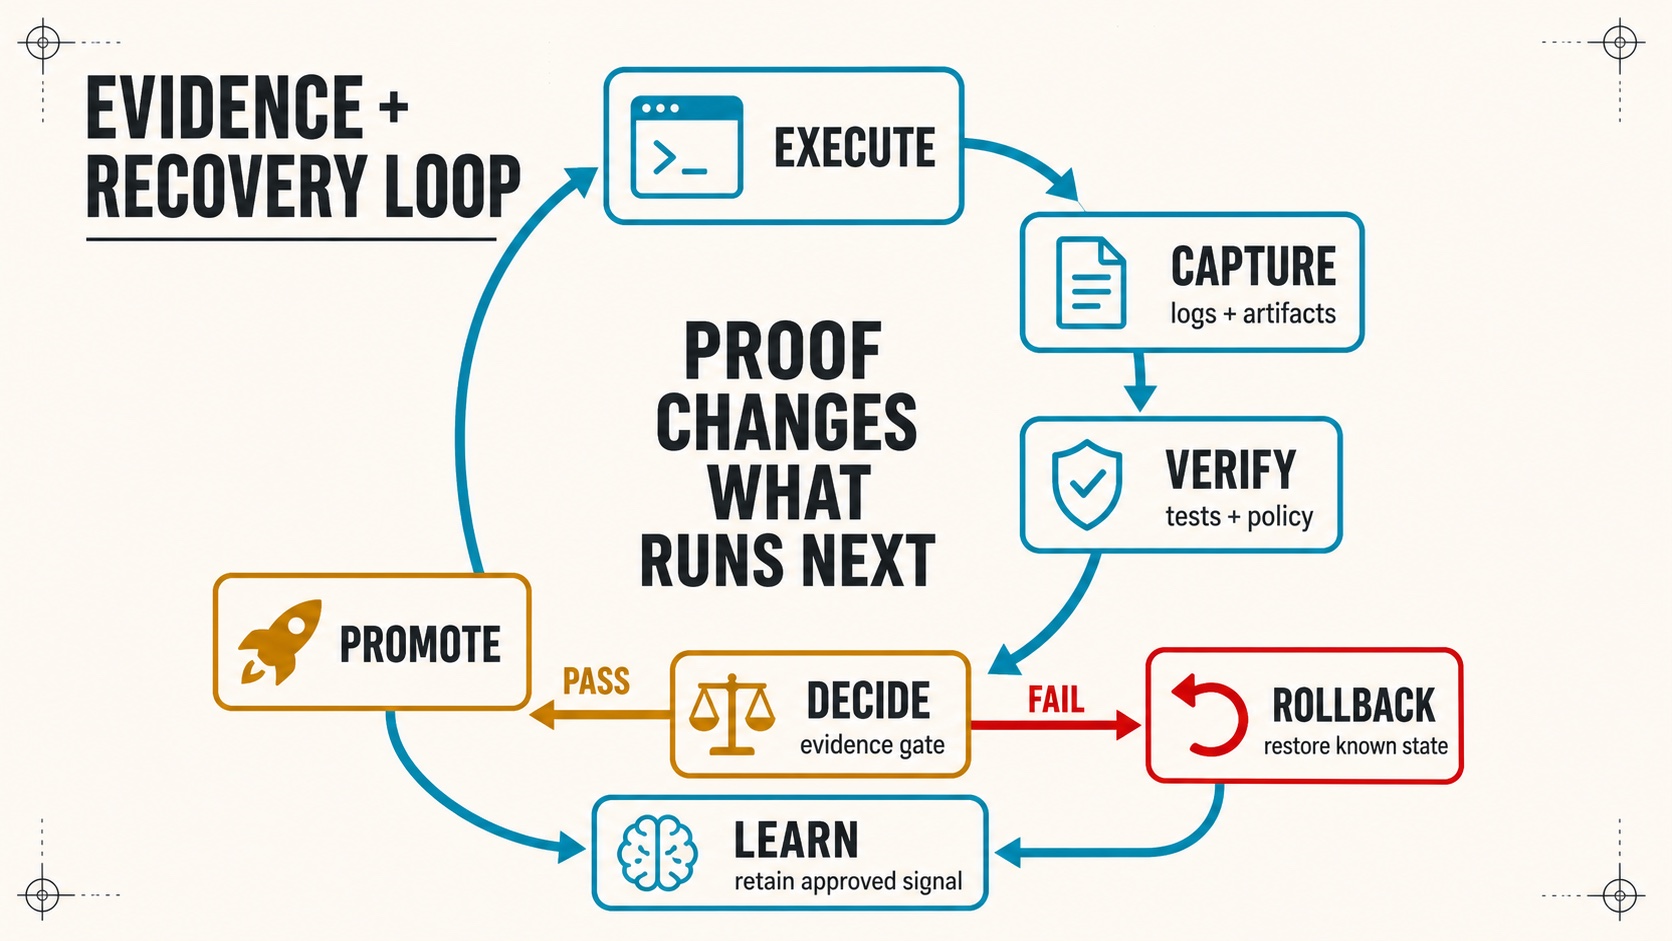
Generate machine-verifiable evidence for PR gates:
lacp e2e smoke --workdir . --init-template --command "npx playwright test --grep @smoke"
lacp api-e2e smoke --workdir . --init-template --command "npx schemathesis run --checks all"
lacp contract-e2e smoke --workdir . --init-template --command "forge test -vv"
lacp pr-preflight --changed-files ./changed-files.txt --checks-json ./checks.json
| Required | Recommended |
|---|---|
bash, python3, jq, rg (ripgrep) | shellcheck, tmux, gh |
The installer auto-detects and installs missing dependencies on macOS via Homebrew.
All installation methods
brew tap 0xNyk/lacp
brew install lacp            # published v0.10.1 release (tap may lag)
brew install --HEAD lacp     # current main
curl -fsSLo /tmp/lacp-install.sh \
  https://raw.githubusercontent.com/0xNyk/lacp/v0.10.1/install.sh
LACP_REF=v0.10.1 bash /tmp/lacp-install.sh
Change both references to main only when you intend to install unreleased development
code. The script also accepts --dir, --profile, and --with-verify; run it with
Stars on GitHub
View @0xnyk’s profileRuns structured deliberation across several reasoning perspectives, so a user can weigh a hard decision from multiple angles before settling on one path.
@0xnykA local-first command line tool for searching, monitoring, and analyzing X (formerly Twitter), with structured exports and actions such as bookmarks, likes, and follower tracking, usable by agents too.
@0xnykReverse engineer anything with agents, from app behavior down to native binaries.
 @morluto
A skill pack for authorized reverse engineering, security research, and penetration testing that routes tasks to the right skill and sets up needed tools on demand. It covers API security assessment and Android APK analysis, among others.
 @zhaoxuya520
Gives an AI agent the step-by-step workflow a senior security analyst follows, covering when to use each technique, what to check first, how to run it and how to verify the result. Covers incident response, forensics, threat intelligence, malware analysis, penetration testing and red teaming.
 @mukul975
Agent skill + stdlib Python service to strip multi-vendor AI provenance marks from text and files, for privacy and hygiene on content you own. The skill is a thin client: it drives the machinery over HTTP, so the agent host needs no Python.
 @guillaumemeyer
Install it with the command on its page. It includes context-modes, quality-gate, session-hardening. Its skills do not fire on their own yet. Free and open source.
Is this plugin yours?
Claim it with GitHubSubmit a pluginPromote it